#include <tls_channel_impl_13.h>
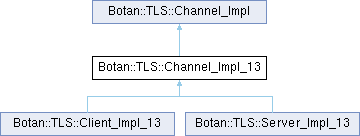
Public Member Functions | |
| virtual std::string | application_protocol () const =0 |
| Channel_Impl_13 (Channel_Impl_13 &&other)=delete | |
| Channel_Impl_13 (const Channel_Impl_13 &other)=delete | |
| Channel_Impl_13 (const std::shared_ptr< Callbacks > &callbacks, const std::shared_ptr< Session_Manager > &session_manager, const std::shared_ptr< Credentials_Manager > &credentials_manager, const std::shared_ptr< RandomNumberGenerator > &rng, const std::shared_ptr< const Policy > &policy, bool is_server) | |
| void | close () |
| virtual std::optional< std::string > | external_psk_identity () const =0 |
| size_t | from_peer (std::span< const uint8_t > data) override |
| bool | is_active () const override |
| bool | is_closed () const override |
| bool | is_closed_for_reading () const override |
| bool | is_closed_for_writing () const override |
| virtual bool | is_handshake_complete () const =0 |
| SymmetricKey | key_material_export (std::string_view label, std::string_view context, size_t length) const override |
| virtual bool | new_session_ticket_supported () const |
| virtual std::optional< std::chrono::milliseconds > | next_retransmission_timeout () const |
| Channel_Impl_13 & | operator= (Channel_Impl_13 &&other)=delete |
| Channel_Impl_13 & | operator= (const Channel_Impl_13 &other)=delete |
| virtual std::vector< X509_Certificate > | peer_cert_chain () const =0 |
| virtual std::shared_ptr< const Public_Key > | peer_raw_public_key () const =0 |
| void | renegotiate (bool) override |
| bool | secure_renegotiation_supported () const override |
| void | send_alert (const Alert &alert) override |
| void | send_fatal_alert (Alert::Type type) |
| virtual size_t | send_new_session_tickets (const size_t) |
| void | send_warning_alert (Alert::Type type) |
| bool | timeout_check () override |
| void | to_peer (std::span< const uint8_t > data) override |
| void | update_traffic_keys (bool request_peer_update=false) override |
| ~Channel_Impl_13 () override | |
Protected Attributes | |
| std::optional< Active_Connection_State_13 > | m_active_state |
| std::shared_ptr< Channel_IO > | m_channel_io |
| std::shared_ptr< Cipher_State > | m_cipher_state |
| const Connection_Side | m_side |
| std::optional< Transcript_Hash_State > | m_transcript_hash |
Detailed Description
Generic interface for TLS 1.3 endpoint
Definition at line 28 of file tls_channel_impl_13.h.
Constructor & Destructor Documentation
◆ Channel_Impl_13() [1/3]
|
explicit |
Set up a new TLS 1.3 session
- Parameters
-
callbacks contains a set of callback function references required by the TLS endpoint. session_manager manages session state credentials_manager manages application/user credentials rng a random number generator policy specifies other connection policy information is_server whether this is a server session or not
Definition at line 43 of file tls_channel_impl_13.cpp.
References BOTAN_ASSERT_NONNULL, callbacks(), credentials_manager(), m_channel_io, m_side, m_transcript_hash, policy(), rng(), and session_manager().
Referenced by Channel_Impl_13(), Channel_Impl_13(), Botan::TLS::Client_Impl_13::Client_Impl_13(), operator=(), operator=(), and Botan::TLS::Server_Impl_13::Server_Impl_13().
◆ Channel_Impl_13() [2/3]
|
delete |
References Channel_Impl_13().
◆ Channel_Impl_13() [3/3]
|
delete |
References Channel_Impl_13().
◆ ~Channel_Impl_13()
|
overridedefault |
Member Function Documentation
◆ application_protocol()
|
pure virtualinherited |
Return the protocol notification set for this connection, if any (ALPN). This value is not tied to the session and a later renegotiation of the same session can choose a new protocol.
Implemented in Botan::TLS::Client_Impl_12, Botan::TLS::Client_Impl_13, and Botan::TLS::Server_Impl_13.
◆ callbacks()
|
inlineprotected |
Definition at line 146 of file tls_channel_impl_13.h.
Referenced by Channel_Impl_13(), Botan::TLS::Client_Impl_13::Client_Impl_13(), Botan::TLS::Client_Impl_13::create(), Botan::TLS::Server_Impl_13::create(), Botan::TLS::Server_Impl_13::send_new_session_tickets(), and Botan::TLS::Server_Impl_13::Server_Impl_13().
◆ close()
|
inlineinherited |
Send a close notification alert
Definition at line 90 of file tls_channel_impl.h.
References send_warning_alert().
◆ compat_mode_ccs_requested()
|
protectedpure virtual |
Referenced by send_alert().
◆ credentials_manager()
|
inlineprotected |
Definition at line 150 of file tls_channel_impl_13.h.
Referenced by Channel_Impl_13(), Botan::TLS::Server_Impl_13::create(), and Botan::TLS::Server_Impl_13::Server_Impl_13().
◆ expects_downgrade()
|
inlineprotectedinherited |
Definition at line 314 of file tls_channel_impl.h.
Referenced by Botan::TLS::Channel_Impl_13::from_peer().
◆ external_psk_identity()
|
pure virtualinherited |
Implemented in Botan::TLS::Channel_Impl_12, Botan::TLS::Client_Impl_13, and Botan::TLS::Server_Impl_13.
◆ from_peer()
|
overridevirtual |
Inject TLS traffic received from counterparty
- Returns
- a hint as the how many more bytes we need to q the current record (this may be 0 if on a record boundary)
Implements Botan::TLS::Channel_Impl.
Definition at line 75 of file tls_channel_impl_13.cpp.
References BOTAN_STATE_CHECK, Botan::TLS::Channel_Impl::expects_downgrade(), Botan::TLS::Channel_Impl::is_downgrading(), Botan::TLS::Channel_Impl::is_handshake_complete(), m_channel_io, m_transcript_hash, Botan::TLS::Channel_Impl::send_fatal_alert(), and Botan::TLS::TLS_Exception::type().
◆ handle()
|
protected |
Definition at line 146 of file tls_channel_impl_13.cpp.
References m_channel_io.
◆ is_active()
|
overridevirtual |
- Returns
- true iff the connection is active for sending application data
Note that the connection is active until the application has called close(), even if a CloseNotify has been received from the peer.
Implements Botan::TLS::Channel_Impl.
Definition at line 197 of file tls_channel_impl_13.cpp.
References m_cipher_state.
Referenced by to_peer(), and update_traffic_keys().
◆ is_closed()
|
inlineoverridevirtual |
- Returns
- true iff the connection has been closed, i.e. CloseNotify has been received from the peer.
Implements Botan::TLS::Channel_Impl.
Definition at line 77 of file tls_channel_impl_13.h.
References is_closed_for_reading(), and is_closed_for_writing().
Referenced by Botan::TLS::Server_Impl_13::is_handshake_complete().
◆ is_closed_for_reading()
|
inlineoverridevirtual |
- Returns
- true iff the connection is active for sending application data
Implements Botan::TLS::Channel_Impl.
Definition at line 79 of file tls_channel_impl_13.h.
Referenced by is_closed().
◆ is_closed_for_writing()
|
inlineoverridevirtual |
- Returns
- true iff the connection has been definitely closed
Implements Botan::TLS::Channel_Impl.
Definition at line 81 of file tls_channel_impl_13.h.
Referenced by is_closed().
◆ is_downgrading()
|
inlineprotectedinherited |
Indicates whether a downgrade to TLS 1.2 or lower is in progress
- See also
- Downgrade_Information
Definition at line 306 of file tls_channel_impl.h.
Referenced by Botan::TLS::Channel_Impl_13::from_peer(), Botan::TLS::Channel_Impl_13::key_material_export(), Botan::TLS::Channel_Impl_13::send_flight(), Botan::TLS::Channel_Impl_13::to_peer(), and Botan::TLS::Channel_Impl_13::update_traffic_keys().
◆ is_handshake_complete()
|
pure virtualinherited |
- Returns
- true iff the TLS handshake has finished successfully
Implemented in Botan::TLS::Channel_Impl_12, Botan::TLS::Client_Impl_13, and Botan::TLS::Server_Impl_13.
Referenced by Botan::TLS::Channel_Impl_13::from_peer(), and Botan::TLS::Channel_Impl_13::update_traffic_keys().
◆ key_material_export()
|
overridevirtual |
Key material export (RFC 5705)
- Parameters
-
label a disambiguating label string context a per-association context value length the length of the desired key in bytes
- Returns
- key of length bytes
Implements Botan::TLS::Channel_Impl.
Definition at line 202 of file tls_channel_impl_13.cpp.
References BOTAN_STATE_CHECK, Botan::TLS::Channel_Impl::is_downgrading(), and m_cipher_state.
◆ maybe_log_secret()
|
protectedpure virtual |
◆ new_session_ticket_supported()
|
inlinevirtualinherited |
- Returns
- true if this channel can issue TLS 1.3 style session tickets.
Reimplemented in Botan::TLS::Server_Impl_13.
Definition at line 156 of file tls_channel_impl.h.
◆ next_retransmission_timeout()
|
inlinevirtualinherited |
Reimplemented in Botan::TLS::Channel_Impl_12.
Definition at line 102 of file tls_channel_impl.h.
◆ note_useless_record()
|
protectedinherited |
Called for each received record that was dropped without having any effect, eg an empty record or a warning alert. Throws if too many of these arrive without any useful record between.
Definition at line 14 of file tls_channel_impl.cpp.
References Botan::TLS::Policy::max_useless_records().
Referenced by Botan::TLS::Channel_Impl_12::from_peer().
◆ operator=() [1/2]
|
delete |
References Channel_Impl_13().
◆ operator=() [2/2]
|
delete |
References Channel_Impl_13().
◆ peer_cert_chain()
|
pure virtualinherited |
- Returns
- certificate chain of the peer (may be empty)
Implemented in Botan::TLS::Channel_Impl_12, Botan::TLS::Client_Impl_13, and Botan::TLS::Server_Impl_13.
◆ peer_raw_public_key()
|
pure virtualinherited |
- Returns
- raw public key of the peer (may be nullptr)
Implemented in Botan::TLS::Channel_Impl_12, Botan::TLS::Client_Impl_13, and Botan::TLS::Server_Impl_13.
◆ policy()
|
inlineprotected |
Definition at line 154 of file tls_channel_impl_13.h.
Referenced by Channel_Impl_13(), Botan::TLS::Client_Impl_13::Client_Impl_13(), Botan::TLS::Client_Impl_13::create(), Botan::TLS::Server_Impl_13::create(), Botan::TLS::Server_Impl_13::send_new_session_tickets(), and Botan::TLS::Server_Impl_13::Server_Impl_13().
◆ process_dummy_change_cipher_spec()
|
protectedpure virtual |
◆ process_handshake_msg()
|
protectedpure virtual |
◆ process_post_handshake_msg()
|
protectedpure virtual |
◆ renegotiate()
|
inlineoverridevirtual |
Attempt to renegotiate the session
Implements Botan::TLS::Channel_Impl.
Definition at line 95 of file tls_channel_impl_13.h.
◆ reset_useless_records()
|
inlineprotectedinherited |
Called for each received record that made progress
Definition at line 211 of file tls_channel_impl.h.
Referenced by Botan::TLS::Channel_Impl_12::from_peer().
◆ rng()
|
inlineprotected |
Definition at line 152 of file tls_channel_impl_13.h.
Referenced by Channel_Impl_13(), Botan::TLS::Client_Impl_13::Client_Impl_13(), Botan::TLS::Client_Impl_13::create(), Botan::TLS::Server_Impl_13::create(), Botan::TLS::Server_Impl_13::send_new_session_tickets(), and Botan::TLS::Server_Impl_13::Server_Impl_13().
◆ secret_logger()
|
protected |
Definition at line 215 of file tls_channel_impl_13.cpp.
◆ secure_renegotiation_supported()
|
inlineoverridevirtual |
- Returns
- true iff the counterparty supports the secure renegotiation extensions.
Implements Botan::TLS::Channel_Impl.
Definition at line 111 of file tls_channel_impl_13.h.
◆ send_alert()
|
overridevirtual |
Send a TLS alert message. If the alert is fatal, the internal state (keys, etc) will be reset.
- Parameters
-
alert the Alert to send
Implements Botan::TLS::Channel_Impl.
Definition at line 160 of file tls_channel_impl_13.cpp.
References Botan::TLS::Alert, compat_mode_ccs_requested(), Botan::TLS::Alert::is_fatal(), Botan::TLS::Alert::is_valid(), m_channel_io, m_cipher_state, and Botan::TLS::Alert::type().
◆ send_fatal_alert()
|
inlineinherited |
Send a fatal alert
Definition at line 85 of file tls_channel_impl.h.
References Botan::TLS::Alert, and send_alert().
Referenced by Botan::TLS::Channel_Impl_12::from_peer(), and Botan::TLS::Channel_Impl_13::from_peer().
◆ send_flight()
|
protected |
Definition at line 223 of file tls_channel_impl_13.cpp.
References BOTAN_STATE_CHECK, Botan::TLS::Channel_Impl::is_downgrading(), and m_channel_io.
Referenced by Botan::TLS::Server_Impl_13::send_new_session_tickets().
◆ send_new_session_tickets()
|
inlinevirtualinherited |
Send tickets new session tickets to the peer. This is only supported on TLS 1.3 servers.
If the server's Session_Manager does not accept the generated Session objects, the server implementation won't be able to send new tickets. Additionally, anything but TLS 1.3 servers will return 0 (because they don't support sending such session tickets).
- Returns
- the number of session tickets successfully sent to the client
Reimplemented in Botan::TLS::Server_Impl_13.
Definition at line 169 of file tls_channel_impl.h.
◆ send_warning_alert()
|
inlineinherited |
Send a warning alert
Definition at line 80 of file tls_channel_impl.h.
References Botan::TLS::Alert, and send_alert().
Referenced by close().
◆ session_manager()
|
inlineprotected |
Definition at line 148 of file tls_channel_impl_13.h.
Referenced by Channel_Impl_13(), Botan::TLS::Client_Impl_13::Client_Impl_13(), Botan::TLS::Client_Impl_13::create(), Botan::TLS::Server_Impl_13::create(), Botan::TLS::Server_Impl_13::send_new_session_tickets(), and Botan::TLS::Server_Impl_13::Server_Impl_13().
◆ set_record_size_limits()
|
protected |
Set the record size limits as negotiated by the "record_size_limit" extension (RFC 8449).
- Parameters
-
outgoing_limit the maximal number of plaintext bytes to be sent in a protected record incoming_limit the maximal number of plaintext bytes to be accepted in a received protected record
Definition at line 379 of file tls_channel_impl_13.cpp.
References m_channel_io.
◆ set_selected_certificate_type()
|
protected |
Set the expected certificate type needed to parse Certificate messages in the handshake layer. See RFC 7250 and 8446 4.4.2 for further details.
Definition at line 383 of file tls_channel_impl_13.cpp.
References m_channel_io.
◆ setup_cipher_state()
|
protected |
Hands ownership of the channel's cipher state to this channel and its associated Channel_IO. Typically called once the handshake's key schedule produced the first traffic secrets.
- Returns
- a reference to the handed-off cipher state for convenience
Definition at line 66 of file tls_channel_impl_13.cpp.
References BOTAN_ASSERT_NONNULL, m_channel_io, and m_cipher_state.
◆ timeout_check()
|
inlineoverridevirtual |
Perform a handshake timeout check. This does nothing unless this is a DTLS channel with a pending handshake state, in which case we check for timeout and potentially retransmit handshake packets.
In the TLS 1.3 implementation, this always returns false.
Implements Botan::TLS::Channel_Impl.
Definition at line 125 of file tls_channel_impl_13.h.
◆ to_peer()
|
overridevirtual |
Inject plaintext intended for counterparty Throws an exception if is_active() is false
Implements Botan::TLS::Channel_Impl.
Definition at line 150 of file tls_channel_impl_13.cpp.
References BOTAN_STATE_CHECK, is_active(), Botan::TLS::Channel_Impl::is_downgrading(), and m_channel_io.
◆ update_traffic_keys()
|
overridevirtual |
Attempt to update the session's traffic key material Note that this is possible with a TLS 1.3 channel, only.
- Parameters
-
request_peer_update if true, require a reciprocal key update
Implements Botan::TLS::Channel_Impl.
Definition at line 210 of file tls_channel_impl_13.cpp.
References BOTAN_STATE_CHECK, is_active(), Botan::TLS::Channel_Impl::is_downgrading(), Botan::TLS::Channel_Impl::is_handshake_complete(), and m_channel_io.
Member Data Documentation
◆ m_active_state
|
protected |
Definition at line 177 of file tls_channel_impl_13.h.
Referenced by Botan::TLS::Client_Impl_13::application_protocol(), Botan::TLS::Server_Impl_13::application_protocol(), Botan::TLS::Client_Impl_13::external_psk_identity(), Botan::TLS::Server_Impl_13::external_psk_identity(), Botan::TLS::Client_Impl_13::is_handshake_complete(), Botan::TLS::Server_Impl_13::is_handshake_complete(), Botan::TLS::Server_Impl_13::new_session_ticket_supported(), Botan::TLS::Client_Impl_13::peer_cert_chain(), Botan::TLS::Server_Impl_13::peer_cert_chain(), Botan::TLS::Client_Impl_13::peer_raw_public_key(), Botan::TLS::Server_Impl_13::peer_raw_public_key(), and Botan::TLS::Server_Impl_13::send_new_session_tickets().
◆ m_channel_io
|
protected |
Definition at line 180 of file tls_channel_impl_13.h.
Referenced by Channel_Impl_13(), from_peer(), handle(), send_alert(), send_flight(), set_record_size_limits(), set_selected_certificate_type(), setup_cipher_state(), to_peer(), and update_traffic_keys().
◆ m_cipher_state
|
protected |
Definition at line 176 of file tls_channel_impl_13.h.
Referenced by is_active(), key_material_export(), send_alert(), Botan::TLS::Server_Impl_13::send_new_session_tickets(), and setup_cipher_state().
◆ m_side
|
protected |
Definition at line 174 of file tls_channel_impl_13.h.
Referenced by Channel_Impl_13().
◆ m_transcript_hash
|
protected |
Definition at line 175 of file tls_channel_impl_13.h.
Referenced by Channel_Impl_13(), and from_peer().
The documentation for this class was generated from the following files:
- src/lib/tls/tls13/tls_channel_impl_13.h
- src/lib/tls/tls13/tls_channel_impl_13.cpp
Generated by
 1.16.1