Botan 3.14.1
Crypto and TLS for C&
Botan::TLS::Channel_Impl_12 Class Referenceabstract

#include <tls_channel_impl_12.h>
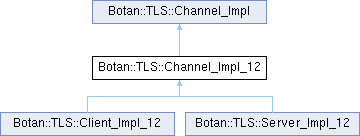
Inheritance diagram for Botan::TLS::Channel_Impl_12:
Botan::TLS::Channel_Impl Botan::TLS::Client_Impl_12 Botan::TLS::Server_Impl_12

Public Member Functions

virtual std::string application_protocol () const =0
 Channel_Impl_12 (Channel_Impl_12 &&other)=delete
 Channel_Impl_12 (const Channel_Impl_12 &other)=delete
 Channel_Impl_12 (const std::shared_ptr< Callbacks > &callbacks, const std::shared_ptr< Session_Manager > &session_manager, const std::shared_ptr< RandomNumberGenerator > &rng, const std::shared_ptr< const Policy > &policy, bool is_server, TLS_Flavor flavor, size_t io_buf_sz=TLS::Channel::IO_BUF_DEFAULT_SIZE)
void close ()
std::optional< std::string > external_psk_identity () const override
size_t from_peer (std::span< const uint8_t > data) override
bool is_active () const override
bool is_closed () const override
bool is_closed_for_reading () const override
bool is_closed_for_writing () const override
bool is_handshake_complete () const override
SymmetricKey key_material_export (std::string_view label, std::string_view context, size_t length) const override
virtual bool new_session_ticket_supported () const
std::optional< std::chrono::milliseconds > next_retransmission_timeout () const override
Channel_Impl_12 & operator= (Channel_Impl_12 &&other)=delete
Channel_Impl_12 & operator= (const Channel_Impl_12 &other)=delete
std::vector< X509_Certificate > peer_cert_chain () const override
std::shared_ptr< const Public_Key > peer_raw_public_key () const override
void renegotiate (bool force_full_renegotiation=false) override
bool secure_renegotiation_supported () const override
void send_alert (const Alert &alert) override
void send_fatal_alert (Alert::Type type)
virtual size_t send_new_session_tickets (const size_t)
void send_warning_alert (Alert::Type type)
bool timeout_check () override
void to_peer (std::span< const uint8_t > data) override
void update_traffic_keys (bool request_peer_update=false) override
 ~Channel_Impl_12 () override

Protected Types

enum class  TimerGeneration : bool { Advance , Keep }

Protected Member Functions

void activate_session ()
const std::optional< Active_Connection_State_12 > & active_state () const
Callbacks & callbacks () const
void change_cipher_spec_reader (Connection_Side side)
void change_cipher_spec_writer (Connection_Side side)
Handshake_State & create_handshake_state (Protocol_Version version, bool epoch0_restart=false, std::optional< uint64_t > read_sequence_number=std::nullopt, std::optional< uint64_t > write_sequence_number=std::nullopt)
virtual bool dtls_epoch0_restart_enabled () const
bool expects_downgrade () const
TLS_Flavor flavor () const
virtual void initiate_handshake (Handshake_State &state, bool force_full_renegotiation)=0
void inspect_handshake_message (const Handshake_Message &msg)
bool is_downgrading () const
void maybe_arm_dtls_retransmission_timer (TimerGeneration generation_policy=TimerGeneration::Advance)
virtual std::string negotiated_application_protocol () const =0
virtual std::unique_ptr< Handshake_State > new_handshake_state (std::unique_ptr< Handshake_IO > io)=0
void note_resumption_handle (std::optional< Session_Handle > handle)
void note_useless_record (const Policy &policy)
const Policy & policy () const
virtual void process_handshake_msg (Handshake_State &pending_state, Handshake_Type type, const std::vector< uint8_t > &contents, bool epoch0_restart)=0
void reset_active_association_state ()
void reset_useless_records ()
RandomNumberGenerator & rng ()
void secure_renegotiation_check (const Client_Hello_12 *client_hello, bool fresh_handshake_mode=false)
void secure_renegotiation_check (const Server_Hello_12 *server_hello)
std::vector< uint8_t > secure_renegotiation_data_for_client_hello () const
std::vector< uint8_t > secure_renegotiation_data_for_server_hello () const
Session_Manager & session_manager ()

Detailed Description

Generic interface for TLSv.12 endpoint

Definition at line 40 of file tls_channel_impl_12.h.

Member Enumeration Documentation

◆ TimerGeneration

enum class Botan::TLS::Channel_Impl_12::TimerGeneration : bool
strongprotected
Enumerator
Advance 
Keep 

Definition at line 167 of file tls_channel_impl_12.h.

167 : bool {
168 Advance,
169 Keep,
170 };

Constructor & Destructor Documentation

◆ Channel_Impl_12() [1/3]

Botan::TLS::Channel_Impl_12::Channel_Impl_12 ( const std::shared_ptr< Callbacks > & callbacks,
const std::shared_ptr< Session_Manager > & session_manager,
const std::shared_ptr< RandomNumberGenerator > & rng,
const std::shared_ptr< const Policy > & policy,
bool is_server,
TLS_Flavor flavor,
size_t io_buf_sz = TLS::Channel::IO_BUF_DEFAULT_SIZE )
explicit

Set up a new TLS session

Parameters
callbackscontains a set of callback function references required by the TLS endpoint.
session_managermanages session state
rnga random number generator
policyspecifies other connection policy information
is_serverwhether this is a server session or not
flavorspecifies the TLS flavor (TLS or DTLS)
io_buf_szThis many bytes of memory will be preallocated for the read and write buffers. Smaller values just mean reallocations and copies are more likely.

Definition at line 92 of file tls_channel_impl_12.cpp.

98 :
99 m_is_server(is_server),
100 m_flavor(flavor),
101 m_callbacks(callbacks),
102 m_session_manager(session_manager),
103 m_policy(policy),
104 m_rng(rng),
105 m_has_been_closed(false) {
106 BOTAN_ASSERT_NONNULL(m_callbacks);
107 BOTAN_ASSERT_NONNULL(m_session_manager);
109 BOTAN_ASSERT_NONNULL(m_policy);
110
111 /* epoch 0 is plaintext, thus null cipher state */
112 m_write_cipher_states[0] = nullptr;
113 m_read_cipher_states[0] = {};
114
115 m_writebuf.reserve(reserved_io_buffer_size);
116 m_readbuf.reserve(reserved_io_buffer_size);
117}
#define BOTAN_ASSERT_NONNULL(ptr)
Definition assert.h:121
RandomNumberGenerator & rng()
Session_Manager & session_manager()
const Policy & policy() const

References BOTAN_ASSERT_NONNULL, callbacks(), flavor(), policy(), rng(), and session_manager().

Referenced by Channel_Impl_12(), Channel_Impl_12(), Botan::TLS::Client_Impl_12::Client_Impl_12(), operator=(), operator=(), and Botan::TLS::Server_Impl_12::Server_Impl_12().

◆ Channel_Impl_12() [2/3]

Botan::TLS::Channel_Impl_12::Channel_Impl_12 ( const Channel_Impl_12 & other)
delete

References Channel_Impl_12().

◆ Channel_Impl_12() [3/3]

Botan::TLS::Channel_Impl_12::Channel_Impl_12 ( Channel_Impl_12 && other)
delete

References Channel_Impl_12().

◆ ~Channel_Impl_12()

Botan::TLS::Channel_Impl_12::~Channel_Impl_12 ( )
overridedefault

Member Function Documentation

◆ activate_session()

void Botan::TLS::Channel_Impl_12::activate_session ( )
protected

Definition at line 568 of file tls_channel_impl_12.cpp.

568 {
569 BOTAN_ASSERT_NONNULL(m_pending_state);
570
571 const auto& state = *m_pending_state;
572
573 if(!state.version().is_datagram_protocol()) {
574 // TLS is easy just remove all but the current state
575 const uint16_t current_epoch = sequence_numbers().current_write_epoch();
576
577 const auto not_current_epoch = [current_epoch](uint16_t epoch) { return (epoch != current_epoch); };
578
579 map_remove_if(not_current_epoch, m_write_cipher_states);
580 map_remove_if(not_current_epoch, m_read_cipher_states);
581 }
582
583 // RFC 6347 4.2.4: "the node that transmits the last flight (the server in an
584 // ordinary handshake or the client in a resumed handshake) MUST respond to a
585 // retransmit of the peer's last flight with a retransmit of the last
586 // flight." Both endpoints retain handshake sequence state, but only that
587 // node replays its outgoing flight.
588 const bool sent_terminal_dtls_flight =
589 (m_flavor == TLS_Flavor::DTLS) && (m_is_server == state.has_server_hello_done());
590
591 const bool encrypt_then_mac_used = m_active_state.has_value() && m_active_state->encrypt_then_mac_used();
592
593 if(m_flavor == TLS_Flavor::DTLS) {
594 m_active_state =
595 Active_Connection_State_12(state, negotiated_application_protocol(), m_pending_state->take_handshake_io());
596 if(auto* dtls_io = m_active_state->dtls_handshake_io()) {
597 // Retain receive sequence state on both endpoints to distinguish a
598 // retransmission from an unexpected new handshake message. Only the
599 // terminal-flight sender responds by replaying its final flight.
600 dtls_io->finalize_handshake(sent_terminal_dtls_flight);
601 }
602 } else {
603 m_active_state = Active_Connection_State_12(state, negotiated_application_protocol());
604 }
605
606 if(encrypt_then_mac_used) {
607 m_active_state->note_encrypt_then_mac_used();
608 }
609
610 clear_pending_handshake_state();
611
613}
virtual void tls_session_activated()
virtual std::string negotiated_application_protocol() const =0
void map_remove_if(Pred pred, T &assoc)
Definition stl_util.h:54

References BOTAN_ASSERT_NONNULL, callbacks(), Botan::TLS::DTLS, Botan::map_remove_if(), negotiated_application_protocol(), and Botan::TLS::Callbacks::tls_session_activated().

◆ active_state()

const std::optional< Active_Connection_State_12 > & Botan::TLS::Channel_Impl_12::active_state ( ) const
inlineprotected

Definition at line 154 of file tls_channel_impl_12.h.

154{ return m_active_state; }

Referenced by Botan::TLS::Client_Impl_12::application_protocol().

◆ application_protocol()

virtual std::string Botan::TLS::Channel_Impl::application_protocol ( ) const
pure virtualinherited

Return the protocol notification set for this connection, if any (ALPN). This value is not tied to the session and a later renegotiation of the same session can choose a new protocol.

Implemented in Botan::TLS::Client_Impl_12, Botan::TLS::Client_Impl_13, and Botan::TLS::Server_Impl_13.

◆ callbacks()

◆ change_cipher_spec_reader()

void Botan::TLS::Channel_Impl_12::change_cipher_spec_reader ( Connection_Side side)
protected

Definition at line 483 of file tls_channel_impl_12.cpp.

483 {
484 const auto* pending = pending_state();
485
486 BOTAN_ASSERT(pending && pending->has_server_hello(), "Have received server hello");
487
488 if(pending->server_hello().compression_method() != 0) {
489 throw Internal_Error("Negotiated unknown compression algorithm");
490 }
491
492 sequence_numbers().new_read_cipher_state();
493
494 const uint16_t epoch = sequence_numbers().current_read_epoch();
495
496 BOTAN_ASSERT(!m_read_cipher_states.contains(epoch), "No read cipher state currently set for next epoch");
497
498 // flip side as we are reading
499 const auto read_state = std::make_shared<Connection_Cipher_State>(
500 pending->version(),
502 false,
503 pending->ciphersuite(),
504 pending->session_keys(),
505 pending->server_hello().supports_encrypt_then_mac());
506
507 // The epoch we just left is retained only to absorb reordering, so start its
508 // clock now (see read_cipher_state_epoch). Epoch 0 is the plaintext
509 // placeholder and holds no keys, so the window does not apply to it.
510 if(m_flavor == TLS_Flavor::DTLS && epoch > 1) {
511 if(const auto prev = m_read_cipher_states.find(static_cast<uint16_t>(epoch - 1));
512 prev != m_read_cipher_states.end()) {
513 prev->second.retired_at = callbacks().tls_current_monotonic_clock_ms();
514 }
515 }
516
517 m_read_cipher_states[epoch] = Retained_Read_Cipher_State{.state = read_state, .retired_at = std::nullopt};
518 prune_old_cipher_states(m_read_cipher_states);
519}
#define BOTAN_ASSERT(expr, assertion_made)
Definition assert.h:69
virtual uint64_t tls_current_monotonic_clock_ms()

References BOTAN_ASSERT, callbacks(), Botan::TLS::Client, Botan::TLS::DTLS, Botan::TLS::Server, and Botan::TLS::Callbacks::tls_current_monotonic_clock_ms().

◆ change_cipher_spec_writer()

void Botan::TLS::Channel_Impl_12::change_cipher_spec_writer ( Connection_Side side)
protected

Definition at line 521 of file tls_channel_impl_12.cpp.

521 {
522 const auto* pending = pending_state();
523
524 BOTAN_ASSERT(pending && pending->has_server_hello(), "Have received server hello");
525
526 if(pending->server_hello().compression_method() != 0) {
527 throw Internal_Error("Negotiated unknown compression algorithm");
528 }
529
530 sequence_numbers().new_write_cipher_state();
531
532 const uint16_t epoch = sequence_numbers().current_write_epoch();
533
534 BOTAN_ASSERT(!m_write_cipher_states.contains(epoch), "No write cipher state currently set for next epoch");
535
536 const auto write_state =
537 std::make_shared<Connection_Cipher_State>(pending->version(),
538 side,
539 true,
540 pending->ciphersuite(),
541 pending->session_keys(),
542 pending->server_hello().supports_encrypt_then_mac());
543
544 m_write_cipher_states[epoch] = write_state;
545 prune_old_cipher_states(m_write_cipher_states);
546}

References BOTAN_ASSERT.

◆ close()

void Botan::TLS::Channel_Impl::close ( )
inlineinherited

Send a close notification alert

Definition at line 90 of file tls_channel_impl.h.

90{ send_warning_alert(Alert::CloseNotify); }
void send_warning_alert(Alert::Type type)

References send_warning_alert().

◆ create_handshake_state()

Handshake_State & Botan::TLS::Channel_Impl_12::create_handshake_state ( Protocol_Version version,
bool epoch0_restart = false,
std::optional< uint64_t > read_sequence_number = std::nullopt,
std::optional< uint64_t > write_sequence_number = std::nullopt )
protected

Definition at line 246 of file tls_channel_impl_12.cpp.

249 {
250 if(pending_state() != nullptr) {
251 throw Internal_Error("create_handshake_state called during handshake");
252 }
253
254 if(m_active_state.has_value()) {
255 const Protocol_Version active_version = m_active_state->version();
256
257 if(active_version.is_datagram_protocol() != version.is_datagram_protocol()) {
258 throw TLS_Exception(Alert::ProtocolVersion,
259 "Active state using version " + active_version.to_string() + " cannot change to " +
260 version.to_string() + " in pending");
261 }
262 }
263
264 if(!m_sequence_numbers) {
265 if(version.is_datagram_protocol()) {
266 m_sequence_numbers = std::make_unique<Datagram_Sequence_Numbers>(read_sequence_number.value_or(0),
267 write_sequence_number.value_or(0));
268 } else {
269 BOTAN_ARG_CHECK(!read_sequence_number.has_value() && !write_sequence_number.has_value(),
270 "TLS does not support externally provided sequence numbers");
271 m_sequence_numbers = std::make_unique<Stream_Sequence_Numbers>();
272 }
273 }
274
275 // Read epochs at or below this one belong to the association already in place,
276 // so application data under them stays deliverable while this handshake runs.
277 // Anything above it is this handshake's own, unauthenticated until its
278 // Finished. See the application-data gate in from_peer.
279 m_epochs_before_latest_renegotiation = Epochs_Before_Latest_Renegotiation{sequence_numbers().current_read_epoch(),
280 sequence_numbers().current_write_epoch()};
281
282 // Floor for the pending handshake's reassembly: a delayed record from the
283 // handshake arrives under a lower epoch and must be rejected. It would
284 // otherwise take the sequence slot the real message needs.
285 //
286 // Zero on an epoch-zero restart, because there the peer legitimately
287 // begins again at epoch zero and the floor would reject it. This is keyed
288 // on the restart actually occurring, not on the policy allowing it: an
289 // ordinary renegotiation needs the floor either way.
290 const uint16_t initial_epoch = epoch0_restart ? 0 : m_epochs_before_latest_renegotiation->read_epoch;
291
292 using namespace std::placeholders;
293
294 std::unique_ptr<Handshake_IO> io;
295 if(version.is_datagram_protocol()) {
296 const size_t policy_mtu = policy().dtls_default_mtu();
297 if(policy_mtu > 0xFFFF) {
298 throw Invalid_Argument("Policy specifies a DTLS MTU larger than 65535");
299 }
300 const uint16_t mtu = static_cast<uint16_t>(policy_mtu);
301
302 const size_t initial_timeout_ms = policy().dtls_initial_timeout();
303 const size_t max_timeout_ms = policy().dtls_maximum_timeout();
304 // A zero timeout would cause retransmissions without any backoff
305 if(initial_timeout_ms == 0 || max_timeout_ms < initial_timeout_ms) {
306 throw Invalid_Argument("Policy specifies invalid DTLS retransmission timeouts");
307 }
308 const std::optional<size_t> max_retransmissions = policy().dtls_maximum_retransmissions();
309
310 const auto send_record_f = [this](uint16_t epoch, Record_Type record_type, const std::vector<uint8_t>& record) {
311 send_record_under_epoch(epoch, record_type, record);
312 };
313 const auto clock_f = [this]() { return callbacks().tls_current_monotonic_clock_ms(); };
314 io = std::make_unique<Datagram_Handshake_IO>(send_record_f,
315 clock_f,
316 sequence_numbers(),
317 mtu,
318 initial_timeout_ms,
319 max_timeout_ms,
320 max_retransmissions,
321 policy().maximum_handshake_message_size(),
322 m_is_server,
323 initial_epoch);
324 } else {
325 const auto send_record_f = [this](Record_Type rec_type, const std::vector<uint8_t>& record) {
326 send_record(rec_type, record);
327 };
328 io = std::make_unique<Stream_Handshake_IO>(send_record_f);
329 }
330
331 m_pending_state = new_handshake_state(std::move(io));
332
333 if(m_active_state.has_value()) {
334 m_pending_state->set_version(m_active_state->version());
335 }
336
337 return *m_pending_state;
338}
#define BOTAN_ARG_CHECK(expr, msg)
Definition assert.h:33
virtual std::unique_ptr< Handshake_State > new_handshake_state(std::unique_ptr< Handshake_IO > io)=0
virtual size_t dtls_maximum_timeout() const
virtual size_t dtls_default_mtu() const
virtual std::optional< size_t > dtls_maximum_retransmissions() const
virtual size_t dtls_initial_timeout() const

References BOTAN_ARG_CHECK, callbacks(), Botan::TLS::Policy::dtls_default_mtu(), Botan::TLS::Policy::dtls_initial_timeout(), Botan::TLS::Policy::dtls_maximum_retransmissions(), Botan::TLS::Policy::dtls_maximum_timeout(), Botan::TLS::Protocol_Version::is_datagram_protocol(), new_handshake_state(), policy(), Botan::TLS::Callbacks::tls_current_monotonic_clock_ms(), and Botan::TLS::Protocol_Version::to_string().

Referenced by renegotiate().

◆ dtls_epoch0_restart_enabled()

virtual bool Botan::TLS::Channel_Impl_12::dtls_epoch0_restart_enabled ( ) const
inlineprotectedvirtual

Definition at line 218 of file tls_channel_impl_12.h.

218{ return false; }

Referenced by from_peer().

◆ expects_downgrade()

bool Botan::TLS::Channel_Impl::expects_downgrade ( ) const
inlineprotectedinherited

Definition at line 314 of file tls_channel_impl.h.

314 {
315#if defined(BOTAN_HAS_TLS_DOWNGRADE_SUPPORT)
316 return m_downgrade_info != nullptr;
317#else
318 return false;
319#endif
320 }

Referenced by Botan::TLS::Channel_Impl_13::from_peer().

◆ external_psk_identity()

std::optional< std::string > Botan::TLS::Channel_Impl_12::external_psk_identity ( ) const
overridevirtual
Returns
identity of the PSK used for this connection or std::nullopt if no PSK was used.

Implements Botan::TLS::Channel_Impl.

Definition at line 236 of file tls_channel_impl_12.cpp.

236 {
237 if(m_active_state.has_value()) {
238 return m_active_state->psk_identity();
239 }
240 if(const auto* state = pending_state()) {
241 return state->psk_identity();
242 }
243 return std::nullopt;
244}

◆ flavor()

TLS_Flavor Botan::TLS::Channel_Impl_12::flavor ( ) const
inlineprotected

◆ from_peer()

size_t Botan::TLS::Channel_Impl_12::from_peer ( std::span< const uint8_t > data)
overridevirtual

Inject TLS traffic received from counterparty

Returns
a hint as the how many more bytes we need to q the current record (this may be 0 if on a record boundary)

Implements Botan::TLS::Channel_Impl.

Definition at line 615 of file tls_channel_impl_12.cpp.

615 {
616 const bool allow_epoch0_restart = (m_flavor == TLS_Flavor::DTLS) && dtls_epoch0_restart_enabled();
617
618 const auto* input = data.data();
619 auto input_size = data.size();
620
621 try {
622 while(input_size > 0) {
623 // A fatal alert destroys the cipher states, so nothing further can even
624 // be decrypted. Closure by close_notify is different: the responding
625 // close_notify still has to be read, so those records keep flowing
626 // through the loop and are filtered per record type below.
627 if(m_had_fatal_alert) {
628 return 0;
629 }
630
631 size_t consumed = 0;
632
633 const auto get_epoch = [this](uint16_t epoch) { return read_cipher_state_epoch(epoch); };
634
635 const Record_Header record = read_record(m_flavor,
636 m_readbuf,
637 input,
638 input_size,
639 consumed,
640 m_record_buf,
641 m_sequence_numbers.get(),
642 get_epoch,
643 allow_epoch0_restart);
644
645 const size_t needed = record.needed();
646
647 BOTAN_ASSERT(consumed > 0, "Got to eat something");
648
649 BOTAN_ASSERT(consumed <= input_size, "Record reader consumed sane amount");
650
651 input += consumed;
652 input_size -= consumed;
653
654 BOTAN_ASSERT(input_size == 0 || needed == 0, "Got a full record or consumed all input");
655
656 if(input_size == 0 && needed != 0) {
657 return needed; // need more data to complete record
658 }
659
660 // Ignore invalid records in DTLS
661 if(m_flavor == TLS_Flavor::DTLS && record.type() == Record_Type::Invalid) {
662 continue;
663 }
664
665 const bool old_unprotected_record = m_flavor == TLS_Flavor::DTLS && record.epoch() == 0 &&
666 m_active_state.has_value() && sequence_numbers().current_read_epoch() > 0;
667
668 // Once encrypted traffic is expected, epoch-zero records are
669 // unauthenticated. Only handshake records can be useful as part of a
670 // retransmitted flight or an explicitly allowed association restart.
671 if(old_unprotected_record && record.type() != Record_Type::Handshake &&
672 record.type() != Record_Type::ChangeCipherSpec) {
673 continue;
674 }
675
676 if(m_record_buf.size() > MAX_PLAINTEXT_SIZE) {
677 if(old_unprotected_record) {
678 continue;
679 }
680
681 throw TLS_Exception(Alert::RecordOverflow, "TLS plaintext record is larger than allowed maximum");
682 }
683
684 const bool epoch0_restart = allow_epoch0_restart && record.epoch() == 0 && m_active_state.has_value();
685 BOTAN_ASSERT_IMPLICATION(epoch0_restart, allow_epoch0_restart, "Allowed state");
686
687 const bool initial_record = epoch0_restart || (pending_state() == nullptr && !m_active_state.has_value());
688 bool initial_handshake_message = false;
689 if(record.type() == Record_Type::Handshake && !m_record_buf.empty()) {
690 const Handshake_Type type = static_cast<Handshake_Type>(m_record_buf[0]);
691 initial_handshake_message = (type == Handshake_Type::ClientHello);
692 }
693
694 if(record.type() != Record_Type::Alert && !old_unprotected_record) {
695 if(initial_record) {
696 // For initial records just check for basic sanity
697 if(record.version().major_version() != 3 && record.version().major_version() != 0xFE) {
698 throw TLS_Exception(Alert::ProtocolVersion, "Received unexpected record version in initial record");
699 }
700 } else if(const auto* pending = pending_state()) {
701 if(pending->has_server_hello() && !initial_handshake_message && record.version() != pending->version()) {
702 throw TLS_Exception(Alert::ProtocolVersion, "Received unexpected record version");
703 }
704 } else if(m_active_state.has_value()) {
705 if(record.version() != m_active_state->version() && !initial_handshake_message) {
706 throw TLS_Exception(Alert::ProtocolVersion, "Received unexpected record version");
707 }
708 }
709 }
710
711 // RFC 5246 7.2.1: "Any data received after a closure alert is ignored."
712 // This is about a closure alert the peer sent us. A peer that keeps
713 // talking after *our* close_notify is a different case, kept as an
714 // error below; BoGo's Shutdown-Shim-ApplicationData requires it.
715 if(m_peer_closed_connection && record.type() != Record_Type::Alert) {
716 continue;
717 }
718
719 // An off-path attacker can forge DTLS epoch-zero records, so they
720 // must neither trip nor reset the limit on useless records
721 const bool counts_for_useless_records = (m_flavor != TLS_Flavor::DTLS || record.epoch() > 0);
722
723 if(record.type() == Record_Type::Handshake || record.type() == Record_Type::ChangeCipherSpec) {
724 if(m_has_been_closed) {
725 throw TLS_Exception(Alert::UnexpectedMessage, "Received handshake data after connection closure");
726 }
727 if(counts_for_useless_records) {
728 if(m_record_buf.empty()) {
730 } else {
732 }
733 }
734 process_handshake_ccs(m_record_buf, record.sequence(), record.type(), record.version(), epoch0_restart);
735 } else if(record.type() == Record_Type::ApplicationData) {
736 if(m_has_been_closed) {
737 throw TLS_Exception(Alert::UnexpectedMessage, "Received application data after connection closure");
738 }
739 if(pending_state() != nullptr) {
740 /*
741 What matters is which epoch the record belongs to, not which role we
742 are playing.
743
744 RFC 6347 4.2.4: "Implementations MUST either discard or buffer all
745 application data packets for the new epoch until they have received
746 the Finished message for that epoch." Data under the epoch this
747 handshake installed is not authenticated until its Finished, so it
748 must not reach the application; equally it is not an error, because
749 ordinary reordering produces it whenever a peer writes immediately
750 after activating.
751
752 Data under an epoch the established association owns stays valid
753 while a renegotiation is in flight, per 4.1.
754
755 Epoch zero is neither: application data there is plaintext, so it is
756 never legitimate and no association is at stake.
757 */
758 if(m_flavor == TLS_Flavor::DTLS && record.epoch() > 0) {
759 const uint16_t active_epoch =
760 m_epochs_before_latest_renegotiation ? m_epochs_before_latest_renegotiation->read_epoch : 0;
761
762 if(!m_active_state.has_value() || record.epoch() > active_epoch) {
763 continue; // this handshake's epoch, still unauthenticated
764 }
765 } else {
766 throw TLS_Exception(Alert::UnexpectedMessage, "Can't interleave application and handshake data");
767 }
768 }
769 process_application_data(record.sequence(), m_record_buf);
770 } else if(record.type() == Record_Type::Alert) {
771 process_alert(m_record_buf, counts_for_useless_records);
772 } else if(record.type() != Record_Type::Invalid) {
773 throw Unexpected_Message("Unexpected record type " + std::to_string(static_cast<size_t>(record.type())) +
774 " from counterparty");
775 }
776 }
777
778 return 0; // on a record boundary
779 } catch(TLS_Exception& e) {
780 send_fatal_alert(e.type());
781 throw;
782 } catch(Invalid_Authentication_Tag&) {
783 send_fatal_alert(Alert::BadRecordMac);
784 throw;
785 } catch(Decoding_Error&) {
786 send_fatal_alert(Alert::DecodeError);
787 throw;
788 } catch(...) {
789 send_fatal_alert(Alert::InternalError);
790 throw;
791 }
792}
#define BOTAN_ASSERT_IMPLICATION(expr1, expr2, msg)
Definition assert.h:108
virtual bool dtls_epoch0_restart_enabled() const
void send_fatal_alert(Alert::Type type)
void note_useless_record(const Policy &policy)
@ MAX_PLAINTEXT_SIZE
Definition tls_magic.h:37
Record_Header read_record(TLS_Flavor flavor, secure_vector< uint8_t > &readbuf, const uint8_t input[], size_t input_len, size_t &consumed, secure_vector< uint8_t > &recbuf, Connection_Sequence_Numbers *sequence_numbers, const get_cipherstate_fn &get_cipherstate, bool allow_epoch0_restart)

References Botan::TLS::Alert, Botan::TLS::ApplicationData, BOTAN_ASSERT, BOTAN_ASSERT_IMPLICATION, Botan::TLS::ChangeCipherSpec, Botan::TLS::ClientHello, Botan::TLS::DTLS, dtls_epoch0_restart_enabled(), Botan::TLS::Record_Header::epoch(), Botan::TLS::Handshake, Botan::TLS::Invalid, Botan::TLS::Protocol_Version::major_version(), Botan::TLS::MAX_PLAINTEXT_SIZE, Botan::TLS::Record_Header::needed(), Botan::TLS::Channel_Impl::note_useless_record(), policy(), Botan::TLS::read_record(), Botan::TLS::Channel_Impl::reset_useless_records(), Botan::TLS::Channel_Impl::send_fatal_alert(), Botan::TLS::Record_Header::sequence(), Botan::TLS::Record_Header::type(), Botan::TLS::TLS_Exception::type(), and Botan::TLS::Record_Header::version().

◆ initiate_handshake()

virtual void Botan::TLS::Channel_Impl_12::initiate_handshake ( Handshake_State & state,
bool force_full_renegotiation )
protectedpure virtual

Referenced by renegotiate().

◆ inspect_handshake_message()

void Botan::TLS::Channel_Impl_12::inspect_handshake_message ( const Handshake_Message & msg)
protected

◆ is_active()

bool Botan::TLS::Channel_Impl_12::is_active ( ) const
overridevirtual
Returns
true iff the connection is active for sending application data

Implements Botan::TLS::Channel_Impl.

Definition at line 552 of file tls_channel_impl_12.cpp.

552 {
553 return !is_closed() && is_handshake_complete();
554}
bool is_handshake_complete() const override

References is_closed(), and is_handshake_complete().

Referenced by to_peer().

◆ is_closed()

bool Botan::TLS::Channel_Impl_12::is_closed ( ) const
overridevirtual
Returns
true iff the connection has been definitely closed

Implements Botan::TLS::Channel_Impl.

Definition at line 564 of file tls_channel_impl_12.cpp.

564 {
565 return m_has_been_closed;
566}

Referenced by is_active(), is_closed_for_reading(), is_closed_for_writing(), and send_alert().

◆ is_closed_for_reading()

bool Botan::TLS::Channel_Impl_12::is_closed_for_reading ( ) const
inlineoverridevirtual
Returns
true iff the connection is active for sending application data

Implements Botan::TLS::Channel_Impl.

Definition at line 98 of file tls_channel_impl_12.h.

98{ return is_closed(); }

References is_closed().

◆ is_closed_for_writing()

bool Botan::TLS::Channel_Impl_12::is_closed_for_writing ( ) const
inlineoverridevirtual
Returns
true iff the connection has been definitely closed

Implements Botan::TLS::Channel_Impl.

Definition at line 100 of file tls_channel_impl_12.h.

100{ return is_closed(); }

References is_closed().

◆ is_downgrading()

bool Botan::TLS::Channel_Impl::is_downgrading ( ) const
inlineprotectedinherited

Indicates whether a downgrade to TLS 1.2 or lower is in progress

See also
Downgrade_Information

Definition at line 306 of file tls_channel_impl.h.

306 {
307#if defined(BOTAN_HAS_TLS_DOWNGRADE_SUPPORT)
308 return m_downgrade_info && m_downgrade_info->will_downgrade;
309#else
310 return false;
311#endif
312 }

Referenced by Botan::TLS::Channel_Impl_13::from_peer(), Botan::TLS::Channel_Impl_13::key_material_export(), Botan::TLS::Channel_Impl_13::send_flight(), Botan::TLS::Channel_Impl_13::to_peer(), and Botan::TLS::Channel_Impl_13::update_traffic_keys().

◆ is_handshake_complete()

bool Botan::TLS::Channel_Impl_12::is_handshake_complete ( ) const
overridevirtual
Returns
true iff the TLS handshake completed successfully

Implements Botan::TLS::Channel_Impl.

Definition at line 548 of file tls_channel_impl_12.cpp.

548 {
549 return m_active_state.has_value();
550}

Referenced by is_active().

◆ key_material_export()

SymmetricKey Botan::TLS::Channel_Impl_12::key_material_export ( std::string_view label,
std::string_view context,
size_t length ) const
overridevirtual

Key material export (RFC 5705)

Parameters
labela disambiguating label string
contexta per-association context value
lengththe length of the desired key in bytes
Returns
key of length bytes

Implements Botan::TLS::Channel_Impl.

Definition at line 1170 of file tls_channel_impl_12.cpp.

1172 {
1173 if(!m_active_state.has_value()) {
1174 throw Invalid_State("Channel_Impl_12::key_material_export connection not active");
1175 }
1176
1177 // A fatal alert should have already cleared the active state:
1178 BOTAN_ASSERT_NOMSG(!m_had_fatal_alert);
1179
1180 if(pending_state() != nullptr) {
1181 throw Invalid_State("Channel_Impl_12::key_material_export cannot export during renegotiation");
1182 }
1183
1184 // RFC 7627 5.4
1185 // If a client or server chooses to continue with a full handshake
1186 // without the extended master secret extension, then the new session
1187 // becomes vulnerable to the man-in-the-middle key synchronization
1188 // attack described in Section 1. Hence, the client or server MUST NOT
1189 // export any key material based on the new master secret for any
1190 // subsequent application-level authentication. In particular, it MUST
1191 // disable [RFC5705] [...]
1192 if(!m_active_state->supports_extended_master_secret()) {
1193 throw Invalid_State("Channel_Impl_12::key_material_export requires the extended master secret");
1194 }
1195
1196 // RFC 5705 4.
1197 // The context value length is encoded as an unsigned, 16-bit quantity
1198 if(context.size() > 0xFFFF) {
1199 throw Invalid_Argument("Channel_Impl_12::key_material_export context is too long");
1200 }
1201
1202 auto prf = callbacks().tls12_protocol_specific_kdf(m_active_state->prf_algo());
1203
1204 const auto salt = [&] {
1205 if(context.empty()) {
1206 return concat(m_active_state->client_random(), m_active_state->server_random());
1207 } else {
1208 return concat(m_active_state->client_random(),
1209 m_active_state->server_random(),
1210 store_be(static_cast<uint16_t>(context.size())),
1211 as_span_of_bytes(context));
1212 }
1213 }();
1214
1215 return SymmetricKey(prf->derive_key(length, m_active_state->master_secret(), salt, as_span_of_bytes(label)));
1216}
#define BOTAN_ASSERT_NOMSG(expr)
Definition assert.h:82
virtual std::unique_ptr< KDF > tls12_protocol_specific_kdf(std::string_view prf_algo) const
OctetString SymmetricKey
Definition symkey.h:153
std::span< const uint8_t > as_span_of_bytes(const char *s, size_t len)
Definition mem_utils.h:59
constexpr auto concat(Rs &&... ranges)
Definition concat_util.h:95
constexpr auto store_be(ParamTs &&... params)
Definition loadstor.h:745

References Botan::as_span_of_bytes(), BOTAN_ASSERT_NOMSG, callbacks(), Botan::concat(), Botan::store_be(), and Botan::TLS::Callbacks::tls12_protocol_specific_kdf().

◆ maybe_arm_dtls_retransmission_timer()

void Botan::TLS::Channel_Impl_12::maybe_arm_dtls_retransmission_timer ( TimerGeneration generation_policy = TimerGeneration::Advance)
protected

Ask the user to asynchronously and transparently invoke the time-based retransmission mechanism.

Definition at line 396 of file tls_channel_impl_12.cpp.

396 {
397 auto next_timeout = next_retransmission_timeout();
398
399 // If there is no timeout, the handshake is complete or there is no handshake
400 // in progress, so there is nothing to arm a timer for.
401 if(!next_timeout.has_value()) {
402 return;
403 }
404
405 // If a new timer generation was requested, we increment the channel-wide
406 // generation counter to invalidate any other timer chain that might still be
407 // running from a backoff interval that has been cut short by incoming data
408 // from the peer.
409 if(generation_policy == TimerGeneration::Advance) {
410 ++m_retransmission_timer_generation;
411 }
412
413 // The actual asynchronous operation:
414 const auto on_timer = [self = weak_from_this(), generation = m_retransmission_timer_generation]() mutable {
415 // If this operation is called after the channel implementation is gone,
416 // the channel magically became some other type, or the operation was
417 // called more than once (see below) just return.
418 const auto channel = std::dynamic_pointer_cast<Channel_Impl_12>(self.lock());
419 if(!channel) {
420 return;
421 }
422
423 // Drop the reference to the channel in this deferred operation. If the
424 // user accidentally calls the operation more than once, the second
425 // invocation will be a harmless no-op.
426 self.reset();
427
428 // This timer-chain may have been superseded by a newer one, when a
429 // backoff interval was reset by the arrival of a belated handshake
430 // message. This generation is no longer active and ends here.
431 if(generation != channel->m_retransmission_timer_generation) {
432 return;
433 }
434
435 // Now we know that we're on the active retransmission/backoff
436 // chain...
437 if(channel->timeout_check()) {
438 // ... and a retransmission was performed: Spawn the next timer
439 // generation for the next backoff interval in this chain.
440 channel->maybe_arm_dtls_retransmission_timer(TimerGeneration::Advance);
441 } else {
442 // ... but no retransmission was performed. Probably, because the
443 // operation was invoked too-early. Re-spawn this generation's
444 // timer for the remaining time until the next deadline.
445 channel->maybe_arm_dtls_retransmission_timer(TimerGeneration::Keep);
446 }
447 };
448
449 m_callbacks->tls_register_deferred_operation(next_timeout->count(), on_timer);
450}
std::optional< std::chrono::milliseconds > next_retransmission_timeout() const override

References Advance, Keep, and next_retransmission_timeout().

◆ negotiated_application_protocol()

virtual std::string Botan::TLS::Channel_Impl_12::negotiated_application_protocol ( ) const
protectedpure virtual

The application protocol of the handshake currently in progress, which becomes the protocol of the connection once that handshake activates

Referenced by activate_session().

◆ new_handshake_state()

virtual std::unique_ptr< Handshake_State > Botan::TLS::Channel_Impl_12::new_handshake_state ( std::unique_ptr< Handshake_IO > io)
protectedpure virtual

Referenced by create_handshake_state().

◆ new_session_ticket_supported()

virtual bool Botan::TLS::Channel_Impl::new_session_ticket_supported ( ) const
inlinevirtualinherited
Returns
true if this channel can issue TLS 1.3 style session tickets.

Reimplemented in Botan::TLS::Server_Impl_13.

Definition at line 156 of file tls_channel_impl.h.

156{ return false; }

◆ next_retransmission_timeout()

std::optional< std::chrono::milliseconds > Botan::TLS::Channel_Impl_12::next_retransmission_timeout ( ) const
overridevirtual

Reimplemented from Botan::TLS::Channel_Impl.

Definition at line 556 of file tls_channel_impl_12.cpp.

556 {
557 if(m_flavor == TLS_Flavor::DTLS && !m_has_been_closed && m_pending_state) {
558 return m_pending_state->handshake_io().next_retransmission_timeout();
559 }
560
561 return std::nullopt;
562}

References Botan::TLS::DTLS.

Referenced by maybe_arm_dtls_retransmission_timer().

◆ note_resumption_handle()

void Botan::TLS::Channel_Impl_12::note_resumption_handle ( std::optional< Session_Handle > handle)
protected

Record the resumption handle this connection was established or resumed under, so that a fatal alert can invalidate it. The ServerHello session ID does not identify a ticket-backed session.

Definition at line 130 of file tls_channel_impl_12.cpp.

130 {
131 m_resumption_handle = std::move(handle);
132}

◆ note_useless_record()

void Botan::TLS::Channel_Impl::note_useless_record ( const Policy & policy)
protectedinherited

Called for each received record that was dropped without having any effect, eg an empty record or a warning alert. Throws if too many of these arrive without any useful record between.

Definition at line 14 of file tls_channel_impl.cpp.

14 {
15 m_useless_records++;
16
17 if(const auto limit = policy.max_useless_records()) {
18 if(m_useless_records > *limit) {
19 throw TLS_Exception(Alert::UnexpectedMessage, "Peer sent too many consecutive useless records");
20 }
21 }
22}

References Botan::TLS::Policy::max_useless_records().

Referenced by Botan::TLS::Channel_Impl_12::from_peer().

◆ operator=() [1/2]

Channel_Impl_12 & Botan::TLS::Channel_Impl_12::operator= ( Channel_Impl_12 && other)
delete

References Channel_Impl_12().

◆ operator=() [2/2]

Channel_Impl_12 & Botan::TLS::Channel_Impl_12::operator= ( const Channel_Impl_12 & other)
delete

References Channel_Impl_12().

◆ peer_cert_chain()

std::vector< X509_Certificate > Botan::TLS::Channel_Impl_12::peer_cert_chain ( ) const
overridevirtual
Returns
certificate chain of the peer (may be empty)

Implements Botan::TLS::Channel_Impl.

Definition at line 229 of file tls_channel_impl_12.cpp.

229 {
230 if(m_active_state.has_value()) {
231 return m_active_state->peer_certs();
232 }
233 return std::vector<X509_Certificate>();
234}

◆ peer_raw_public_key()

std::shared_ptr< const Public_Key > Botan::TLS::Channel_Impl_12::peer_raw_public_key ( ) const
inlineoverridevirtual

Note: Raw public key for authentication (RFC7250) is currently not implemented for TLS 1.2.

Returns
raw public key of the peer (will be nullptr)

Implements Botan::TLS::Channel_Impl.

Definition at line 113 of file tls_channel_impl_12.h.

113{ return nullptr; }

◆ policy()

◆ process_handshake_msg()

virtual void Botan::TLS::Channel_Impl_12::process_handshake_msg ( Handshake_State & pending_state,
Handshake_Type type,
const std::vector< uint8_t > & contents,
bool epoch0_restart )
protectedpure virtual

◆ renegotiate()

void Botan::TLS::Channel_Impl_12::renegotiate ( bool force_full_renegotiation = false)
overridevirtual

Attempt to renegotiate the session

Parameters
force_full_renegotiationif true, require a full renegotiation, otherwise allow session resumption

Implements Botan::TLS::Channel_Impl.

Definition at line 452 of file tls_channel_impl_12.cpp.

452 {
453 if(pending_state() != nullptr) { // currently in handshake?
454 return;
455 }
456
457 if(m_active_state.has_value()) {
458 // A handshake consumes one read and one write epoch. Refuse here if
459 // either is spent, so the caller learns before the handshake tears the
460 // working connection down partway through. See next_epoch().
461 if(sequence_numbers().current_read_epoch() == 0xFFFF || sequence_numbers().current_write_epoch() == 0xFFFF) {
462 throw Invalid_State("TLS epoch counter exhausted, a new connection is required");
463 }
464
465 if(!secure_renegotiation_supported() && !policy().allow_insecure_renegotiation()) {
466 throw Invalid_State("Peer does not support secure renegotiation and policy prohibits insecure renegotiation");
467 }
468
469 if(!force_full_renegotiation) {
470 force_full_renegotiation = !policy().allow_resumption_for_renegotiation();
471 }
472
473 initiate_handshake(create_handshake_state(m_active_state->version()), force_full_renegotiation);
474 } else {
475 throw Invalid_State("Cannot renegotiate on inactive connection");
476 }
477}
Handshake_State & create_handshake_state(Protocol_Version version, bool epoch0_restart=false, std::optional< uint64_t > read_sequence_number=std::nullopt, std::optional< uint64_t > write_sequence_number=std::nullopt)
virtual void initiate_handshake(Handshake_State &state, bool force_full_renegotiation)=0
bool secure_renegotiation_supported() const override
virtual bool allow_resumption_for_renegotiation() const

References Botan::TLS::Policy::allow_resumption_for_renegotiation(), create_handshake_state(), initiate_handshake(), policy(), and secure_renegotiation_supported().

◆ reset_active_association_state()

void Botan::TLS::Channel_Impl_12::reset_active_association_state ( )
protected

Definition at line 172 of file tls_channel_impl_12.cpp.

172 {
173 // This operation only makes sense for DTLS
175 m_active_state.reset();
176 // With the old association gone the restart is an ordinary handshake, whose
177 // failure must be reported rather than rolled back
178 m_dtls_pending_is_epoch0_restart = false;
179 m_read_cipher_states.clear();
180 m_write_cipher_states.clear();
181
182 m_write_cipher_states[0] = nullptr;
183 m_read_cipher_states[0] = {};
184
185 if(m_sequence_numbers) {
186 m_sequence_numbers->reset(); // NOLINT(*-ambiguous-smartptr-reset-call)
187 }
188}

References BOTAN_ASSERT_NOMSG, and Botan::TLS::DTLS.

◆ reset_useless_records()

void Botan::TLS::Channel_Impl::reset_useless_records ( )
inlineprotectedinherited

Called for each received record that made progress

Definition at line 211 of file tls_channel_impl.h.

211{ m_useless_records = 0; }

Referenced by Botan::TLS::Channel_Impl_12::from_peer().

◆ rng()

◆ secure_renegotiation_check() [1/2]

void Botan::TLS::Channel_Impl_12::secure_renegotiation_check ( const Client_Hello_12 * client_hello,
bool fresh_handshake_mode = false )
protected

Definition at line 1091 of file tls_channel_impl_12.cpp.

1091 {
1092 BOTAN_ASSERT_NONNULL(client_hello);
1093 const bool secure_renegotiation = client_hello->secure_renegotiation();
1094
1095 if(!fresh_handshake_mode && m_active_state &&
1096 m_active_state->client_supports_secure_renegotiation() != secure_renegotiation) {
1097 throw TLS_Exception(Alert::HandshakeFailure, "Client changed its mind about secure renegotiation");
1098 }
1099
1100 if(secure_renegotiation) {
1101 const std::vector<uint8_t>& data = client_hello->renegotiation_info();
1102
1103 const auto expected =
1104 fresh_handshake_mode ? std::vector<uint8_t>() : secure_renegotiation_data_for_client_hello();
1105 if(!CT::is_equal<uint8_t>(data, expected).as_bool()) {
1106 throw TLS_Exception(Alert::HandshakeFailure, "Client sent bad values for secure renegotiation");
1107 }
1108 }
1109}
std::vector< uint8_t > secure_renegotiation_data_for_client_hello() const
constexpr CT::Mask< T > is_equal(const T x[], const T y[], size_t len)
Definition ct_utils.h:803

References BOTAN_ASSERT_NONNULL, Botan::CT::is_equal(), Botan::TLS::Client_Hello_12::renegotiation_info(), Botan::TLS::Client_Hello_12::secure_renegotiation(), and secure_renegotiation_data_for_client_hello().

◆ secure_renegotiation_check() [2/2]

void Botan::TLS::Channel_Impl_12::secure_renegotiation_check ( const Server_Hello_12 * server_hello)
protected

Definition at line 1111 of file tls_channel_impl_12.cpp.

1111 {
1112 BOTAN_ASSERT_NONNULL(server_hello);
1113 const bool secure_renegotiation = server_hello->secure_renegotiation();
1114
1115 if(m_active_state && m_active_state->server_supports_secure_renegotiation() != secure_renegotiation) {
1116 throw TLS_Exception(Alert::HandshakeFailure, "Server changed its mind about secure renegotiation");
1117 }
1118
1119 if(secure_renegotiation) {
1120 const std::vector<uint8_t>& data = server_hello->renegotiation_info();
1121
1122 const auto expected = secure_renegotiation_data_for_server_hello();
1123 if(!CT::is_equal<uint8_t>(data, expected).as_bool()) {
1124 throw TLS_Exception(Alert::HandshakeFailure, "Server sent bad values for secure renegotiation");
1125 }
1126 }
1127
1128 // RFC 7366 3.1
1129 // implementations MUST NOT renegotiate a downgrade from
1130 // encrypt-then-MAC to MAC-then-encrypt.
1131 //
1132 // Note that these rules apply across potentially many rehandshakes.
1133 if(m_active_state && m_active_state->encrypt_then_mac_used() && !server_hello->supports_encrypt_then_mac()) {
1134 const auto suite = Ciphersuite::by_id(server_hello->ciphersuite());
1135 if(suite.has_value() && suite->cbc_ciphersuite()) {
1136 throw TLS_Exception(Alert::HandshakeFailure, "Renegotiation would downgrade from encrypt-then-MAC");
1137 }
1138 }
1139}
std::vector< uint8_t > secure_renegotiation_data_for_server_hello() const
static std::optional< Ciphersuite > by_id(uint16_t suite)

References BOTAN_ASSERT_NONNULL, Botan::TLS::Ciphersuite::by_id(), Botan::TLS::Server_Hello::ciphersuite(), Botan::CT::is_equal(), Botan::TLS::Server_Hello_12::renegotiation_info(), Botan::TLS::Server_Hello_12::secure_renegotiation(), secure_renegotiation_data_for_server_hello(), and Botan::TLS::Server_Hello_12::supports_encrypt_then_mac().

◆ secure_renegotiation_data_for_client_hello()

std::vector< uint8_t > Botan::TLS::Channel_Impl_12::secure_renegotiation_data_for_client_hello ( ) const
protected

Definition at line 1141 of file tls_channel_impl_12.cpp.

1141 {
1142 if(m_active_state.has_value()) {
1143 return m_active_state->client_finished_verify_data();
1144 }
1145 return std::vector<uint8_t>();
1146}

Referenced by secure_renegotiation_check().

◆ secure_renegotiation_data_for_server_hello()

std::vector< uint8_t > Botan::TLS::Channel_Impl_12::secure_renegotiation_data_for_server_hello ( ) const
protected

Definition at line 1148 of file tls_channel_impl_12.cpp.

1148 {
1149 if(m_active_state.has_value()) {
1150 return concat(m_active_state->client_finished_verify_data(), m_active_state->server_finished_verify_data());
1151 } else {
1152 return {};
1153 }
1154}

References Botan::concat().

Referenced by secure_renegotiation_check().

◆ secure_renegotiation_supported()

bool Botan::TLS::Channel_Impl_12::secure_renegotiation_supported ( ) const
overridevirtual
Returns
true iff the counterparty supports the secure renegotiation extensions.

Implements Botan::TLS::Channel_Impl.

Definition at line 1156 of file tls_channel_impl_12.cpp.

1156 {
1157 if(m_active_state.has_value()) {
1158 return m_active_state->server_supports_secure_renegotiation();
1159 }
1160
1161 if(const auto* pending = pending_state()) {
1162 if(const auto* hello = pending->maybe_server_hello()) {
1163 return hello->secure_renegotiation();
1164 }
1165 }
1166
1167 return false;
1168}

Referenced by renegotiate().

◆ send_alert()

void Botan::TLS::Channel_Impl_12::send_alert ( const Alert & alert)
overridevirtual

Send a TLS alert message. If the alert is fatal, the internal state (keys, etc) will be reset.

Parameters
alertthe Alert to send

Implements Botan::TLS::Channel_Impl.

Definition at line 1042 of file tls_channel_impl_12.cpp.

1042 {
1043 const bool ready_to_send_anything = !is_closed() && m_sequence_numbers;
1044 if(alert.is_valid() && ready_to_send_anything) {
1045 try {
1046 send_record(Record_Type::Alert, alert.serialize());
1047 } catch(...) { /* swallow it */
1048 }
1049 }
1050
1051 // RFC 5246 7.2.2:
1052 // no_renegotiation
1053 // Sent by the client in response to a hello request or by the
1054 // server in response to a client hello after initial handshaking.
1055 //
1056 // In this case we are the peer sending the refusal, so there is no reason
1057 // for our epochs to have moved. If they somehow did, clear the pending
1058 // state. A strictly better approach here would be to simply throw
1059 // Internal_Error, but send_alert is called from within catch handlers
1060 // so this is not currently viable.
1061 if(alert.type() == Alert::NoRenegotiation && m_active_state.has_value()) {
1062 if(pending_handshake_epochs_unmoved()) {
1063 clear_pending_handshake_state();
1064 }
1065 }
1066
1067 if(alert.is_fatal()) {
1068 // Order matters: the channel is made unusable and its secrets destroyed
1069 // before any application-supplied storage is touched, so a throwing
1070 // session manager cannot leave is_active() true with live keys.
1071 m_had_fatal_alert = true;
1072 m_has_been_closed = true;
1073
1074 // Alert::None is the local teardown that is never sent to the peer, used
1075 // where the trigger was unauthenticated input or a local timeout. Evicting
1076 // the resumption state on that basis would hand anyone able to reach the
1077 // address the ability to destroy it, which is what keeping the teardown
1078 // local exists to prevent.
1079 const auto invalidated =
1080 (alert.type() == Alert::None) ? std::vector<Session_Handle>() : take_sessions_to_invalidate();
1081
1082 reset_state();
1083 invalidate_sessions(invalidated);
1084 }
1085
1086 if(alert.type() == Alert::CloseNotify || alert.is_fatal()) {
1087 m_has_been_closed = true;
1088 }
1089}

References Botan::TLS::Alert, is_closed(), Botan::TLS::Alert::is_fatal(), Botan::TLS::Alert::is_valid(), Botan::TLS::Alert::serialize(), and Botan::TLS::Alert::type().

◆ send_fatal_alert()

void Botan::TLS::Channel_Impl::send_fatal_alert ( Alert::Type type)
inlineinherited

Send a fatal alert

Definition at line 85 of file tls_channel_impl.h.

85{ send_alert(Alert(type, true)); }
virtual void send_alert(const Alert &alert)=0

References Botan::TLS::Alert, and send_alert().

Referenced by Botan::TLS::Channel_Impl_12::from_peer(), and Botan::TLS::Channel_Impl_13::from_peer().

◆ send_new_session_tickets()

virtual size_t Botan::TLS::Channel_Impl::send_new_session_tickets ( const size_t )
inlinevirtualinherited

Send tickets new session tickets to the peer. This is only supported on TLS 1.3 servers.

If the server's Session_Manager does not accept the generated Session objects, the server implementation won't be able to send new tickets. Additionally, anything but TLS 1.3 servers will return 0 (because they don't support sending such session tickets).

Returns
the number of session tickets successfully sent to the client

Reimplemented in Botan::TLS::Server_Impl_13.

Definition at line 169 of file tls_channel_impl.h.

169{ return 0; }

◆ send_warning_alert()

void Botan::TLS::Channel_Impl::send_warning_alert ( Alert::Type type)
inlineinherited

Send a warning alert

Definition at line 80 of file tls_channel_impl.h.

80{ send_alert(Alert(type, false)); }

References Botan::TLS::Alert, and send_alert().

Referenced by close().

◆ session_manager()

Session_Manager & Botan::TLS::Channel_Impl_12::session_manager ( )
inlineprotected

◆ timeout_check()

bool Botan::TLS::Channel_Impl_12::timeout_check ( )
overridevirtual

Perform a handshake timeout check. This does nothing unless this is a DTLS channel with a handshake in progress.

Implements Botan::TLS::Channel_Impl.

Definition at line 381 of file tls_channel_impl_12.cpp.

381 {
382 if(m_flavor == TLS_Flavor::DTLS && !m_has_been_closed && m_pending_state) {
383 try {
384 return m_pending_state->handshake_io().timeout_check();
385 } catch(const TLS_Exception&) {
386 abandon_timed_out_handshake();
387 throw;
388 }
389 }
390
391 // Old cipher states are pruned at install time (see prune_old_cipher_states),
392 // so no periodic cleanup is needed here.
393 return false;
394}

References Botan::TLS::DTLS.

◆ to_peer()

void Botan::TLS::Channel_Impl_12::to_peer ( std::span< const uint8_t > data)
overridevirtual

Inject plaintext intended for counterparty Throws an exception if is_active() is false

Implements Botan::TLS::Channel_Impl.

Definition at line 1034 of file tls_channel_impl_12.cpp.

1034 {
1035 if(!is_active()) {
1036 throw Invalid_State("Data cannot be sent on inactive TLS connection");
1037 }
1038
1039 send_record_array(sequence_numbers().current_write_epoch(), Record_Type::ApplicationData, data.data(), data.size());
1040}

References Botan::TLS::ApplicationData, and is_active().

◆ update_traffic_keys()

void Botan::TLS::Channel_Impl_12::update_traffic_keys ( bool request_peer_update = false)
overridevirtual

Attempt to update the session's traffic key material Note that this is possible with a TLS 1.3 channel, only.

Parameters
request_peer_updateif true, require a reciprocal key update

Implements Botan::TLS::Channel_Impl.

Definition at line 479 of file tls_channel_impl_12.cpp.

479 {
480 throw Invalid_Argument("cannot update traffic keys on a TLS 1.2 channel");
481}

The documentation for this class was generated from the following files: