#include <tls_session.h>
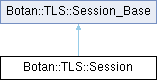
Public Member Functions | |
| Ciphersuite | ciphersuite () const |
| uint16_t | ciphersuite_code () const |
| secure_vector< uint8_t > | DER_encode () const |
| uint16_t | dtls_srtp_profile () const |
| std::vector< uint8_t > | encrypt (const SymmetricKey &key, RandomNumberGenerator &rng) const |
| secure_vector< uint8_t > | extract_master_secret () |
| std::chrono::seconds | lifetime_hint () const |
| const secure_vector< uint8_t > & | master_secret () const |
| uint32_t | max_early_data_bytes () const |
| const std::vector< X509_Certificate > & | peer_certs () const |
| std::optional< Certificate_Type > | peer_credential_type () const |
| std::shared_ptr< const Public_Key > | peer_raw_public_key () const |
| std::string | PEM_encode () const |
| const Server_Information & | server_info () const |
| Session (const secure_vector< uint8_t > &master_secret, Protocol_Version version, uint16_t ciphersuite, Connection_Side side, bool supports_extended_master_secret, bool supports_encrypt_then_mac, const std::vector< X509_Certificate > &peer_certs, const Server_Information &server_info, uint16_t srtp_profile, std::chrono::system_clock::time_point current_timestamp, std::chrono::seconds lifetime_hint=std::chrono::seconds::max()) | |
| Session (const secure_vector< uint8_t > &session_psk, const std::optional< uint32_t > &max_early_data_bytes, uint32_t ticket_age_add, std::chrono::seconds lifetime_hint, Protocol_Version version, uint16_t ciphersuite, Connection_Side side, const std::vector< X509_Certificate > &peer_certs, std::shared_ptr< const Public_Key > peer_raw_public_key, const Server_Information &server_info, std::chrono::system_clock::time_point current_timestamp) | |
| BOTAN_FUTURE_EXPLICIT | Session (std::span< const uint8_t > ber_data) |
| Session (std::string_view pem) | |
| uint32_t | session_age_add () const |
| Connection_Side | side () const |
| std::chrono::system_clock::time_point | start_time () const |
| bool | supports_early_data () const |
| bool | supports_encrypt_then_mac () const |
| bool | supports_extended_master_secret () const |
| Protocol_Version | version () const |
Static Public Member Functions | |
| static Session | decrypt (const uint8_t ctext[], size_t ctext_size, const SymmetricKey &key) |
| static Session | decrypt (std::span< const uint8_t > ctext, const SymmetricKey &key) |
Protected Attributes | |
| uint16_t | m_ciphersuite = 0 |
| Connection_Side | m_connection_side = Connection_Side::Client |
| bool | m_encrypt_then_mac = false |
| bool | m_extended_master_secret = false |
| std::vector< X509_Certificate > | m_peer_certs |
| std::shared_ptr< const Public_Key > | m_peer_raw_public_key |
| Server_Information | m_server_info |
| uint16_t | m_srtp_profile = 0 |
| std::chrono::system_clock::time_point | m_start_time |
| Protocol_Version | m_version |
Detailed Description
Represents a session's negotiated features along with all resumption information to re-establish a TLS connection later on.
Definition at line 254 of file tls_session.h.
Constructor & Destructor Documentation
◆ Session() [1/4]
| Botan::TLS::Session::Session | ( | const secure_vector< uint8_t > & | master_secret, |
| Protocol_Version | version, | ||
| uint16_t | ciphersuite, | ||
| Connection_Side | side, | ||
| bool | supports_extended_master_secret, | ||
| bool | supports_encrypt_then_mac, | ||
| const std::vector< X509_Certificate > & | peer_certs, | ||
| const Server_Information & | server_info, | ||
| uint16_t | srtp_profile, | ||
| std::chrono::system_clock::time_point | current_timestamp, | ||
| std::chrono::seconds | lifetime_hint = std::chrono::seconds::max() ) |
New TLS 1.2 session (sets session start time)
Definition at line 239 of file tls_session.cpp.
References BOTAN_ARG_CHECK, Botan::TLS::Session_Base::ciphersuite(), lifetime_hint(), master_secret(), Botan::TLS::Session_Base::server_info(), Botan::TLS::Session_Base::Session_Base(), Botan::TLS::Session_Base::side(), and Botan::TLS::Session_Base::version().
◆ Session() [2/4]
| Botan::TLS::Session::Session | ( | const secure_vector< uint8_t > & | session_psk, |
| const std::optional< uint32_t > & | max_early_data_bytes, | ||
| uint32_t | ticket_age_add, | ||
| std::chrono::seconds | lifetime_hint, | ||
| Protocol_Version | version, | ||
| uint16_t | ciphersuite, | ||
| Connection_Side | side, | ||
| const std::vector< X509_Certificate > & | peer_certs, | ||
| std::shared_ptr< const Public_Key > | peer_raw_public_key, | ||
| const Server_Information & | server_info, | ||
| std::chrono::system_clock::time_point | current_timestamp ) |
New TLS 1.3 session (sets session start time)
Definition at line 270 of file tls_session.cpp.
References BOTAN_ARG_CHECK, Botan::TLS::Session_Base::ciphersuite(), lifetime_hint(), max_early_data_bytes(), Botan::TLS::Session_Base::peer_certs(), Botan::TLS::Session_Base::peer_raw_public_key(), Botan::TLS::Session_Base::server_info(), Botan::TLS::Session_Base::Session_Base(), Botan::TLS::Session_Base::side(), and Botan::TLS::Session_Base::version().
◆ Session() [3/4]
| Botan::TLS::Session::Session | ( | std::span< const uint8_t > | ber_data | ) |
Load a session from DER representation (created by DER_encode)
- Parameters
-
ber_data DER representation buffer
Definition at line 313 of file tls_session.cpp.
References Botan::TLS::Ciphersuite::by_id(), Botan::TLS::Session_Base::ciphersuite_code(), Botan::TLS::Client, Botan::BER_Decoder::decode(), Botan::BER_Decoder::decode_and_check(), Botan::BER_Decoder::decode_integer_type(), Botan::BER_Decoder::decode_list(), Botan::BER_Decoder::Limits::DER(), lifetime_hint(), Botan::X509::load_key(), Botan::TLS::Session_Base::m_ciphersuite, Botan::TLS::Session_Base::m_connection_side, Botan::TLS::Session_Base::m_encrypt_then_mac, Botan::TLS::Session_Base::m_extended_master_secret, Botan::TLS::Session_Base::m_peer_certs, Botan::TLS::Session_Base::m_peer_raw_public_key, Botan::TLS::Session_Base::m_server_info, Botan::TLS::Session_Base::m_srtp_profile, Botan::TLS::Session_Base::m_start_time, Botan::TLS::Session_Base::m_version, Botan::OctetString, Botan::TLS::Server, Botan::BER_Decoder::start_sequence(), Botan::TLS::Session_Base::start_time(), and Botan::ASN1_String::value().
◆ Session() [4/4]
|
explicit |
Load a session from PEM representation (created by PEM_encode)
- Parameters
-
PEM PEM representation
Definition at line 311 of file tls_session.cpp.
References Session().
Member Function Documentation
◆ ciphersuite()
|
inherited |
Get the ciphersuite info of the negotiated TLS session
Definition at line 123 of file tls_session.cpp.
References Botan::TLS::Ciphersuite::by_id(), and m_ciphersuite.
Referenced by Botan::TLS::Session_Summary::cipher_algo(), Botan::TLS::Session_Summary::mac_algo(), Botan::TLS::Session_Summary::prf_algo(), Botan::TLS::Server_Hello_12::Server_Hello_12(), Botan::TLS::Session::Session(), Botan::TLS::Session::Session(), and Session_Base().
◆ ciphersuite_code()
|
inlineinherited |
Get the ciphersuite code of the negotiated TLS session
Definition at line 79 of file tls_session.h.
References m_ciphersuite.
Referenced by Botan::TLS::Session::Session().
◆ decrypt() [1/2]
|
inlinestatic |
Decrypt a session created by encrypt
- Parameters
-
ctext the ciphertext returned by encrypt ctext_size the size of ctext in bytes key the same key used by the encrypting side
Definition at line 320 of file tls_session.h.
References decrypt(), and Session().
Referenced by decrypt(), Botan::TLS::Session_Manager_SQL::find_some(), Botan::TLS::Session_Manager_SQL::retrieve_one(), and Botan::TLS::Session_Manager_Stateless::retrieve_one().
◆ decrypt() [2/2]
|
static |
Decrypt a session created by encrypt
- Parameters
-
ctext the ciphertext returned by encrypt key the same key used by the encrypting side
Definition at line 515 of file tls_session.cpp.
References Botan::BufferSlicer::copy_as_secure_vector(), Botan::AEAD_Mode::create_or_throw(), Botan::MessageAuthenticationCode::create_or_throw(), Botan::Decryption, Botan::CT::is_equal(), Botan::load_be(), Botan::BufferSlicer::remaining(), Session(), and Botan::BufferSlicer::take().
◆ DER_encode()
| secure_vector< uint8_t > Botan::TLS::Session::DER_encode | ( | ) | const |
Encode this session data for storage
- Warning
- if the master secret is compromised so is the session traffic
Definition at line 409 of file tls_session.cpp.
References Botan::DER_Encoder::encode(), Botan::DER_Encoder::encode_list(), Botan::DER_Encoder::end_cons(), Botan::DER_Encoder::get_contents(), Botan::TLS::Session_Base::m_ciphersuite, Botan::TLS::Session_Base::m_connection_side, Botan::TLS::Session_Base::m_encrypt_then_mac, Botan::TLS::Session_Base::m_extended_master_secret, Botan::TLS::Session_Base::m_peer_certs, Botan::TLS::Session_Base::m_peer_raw_public_key, Botan::TLS::Session_Base::m_server_info, Botan::TLS::Session_Base::m_srtp_profile, Botan::TLS::Session_Base::m_start_time, Botan::TLS::Session_Base::m_version, Botan::OctetString, Botan::DER_Encoder::start_sequence(), and Botan::Utf8String.
Referenced by encrypt(), and PEM_encode().
◆ dtls_srtp_profile()
|
inlineinherited |
Get the negotiated DTLS-SRTP algorithm (RFC 5764)
Definition at line 94 of file tls_session.h.
References m_srtp_profile.
Referenced by Botan::TLS::Client_Hello_12::Client_Hello_12(), and Botan::TLS::Server_Hello_12::Server_Hello_12().
◆ encrypt()
| std::vector< uint8_t > Botan::TLS::Session::encrypt | ( | const SymmetricKey & | key, |
| RandomNumberGenerator & | rng ) const |
Encrypt a session (useful for serialization or session tickets)
Definition at line 472 of file tls_session.cpp.
References BOTAN_ASSERT_NOMSG, Botan::AEAD_Mode::create_or_throw(), Botan::MessageAuthenticationCode::create_or_throw(), DER_encode(), Botan::Encryption, Botan::RandomNumberGenerator::random_vec(), and Botan::store_be().
Referenced by Botan::TLS::Session_Manager_Stateless::establish(), and Botan::TLS::Session_Manager_SQL::store().
◆ extract_master_secret()
| secure_vector< uint8_t > Botan::TLS::Session::extract_master_secret | ( | ) |
Get the contained master secret as a moved-out object
Definition at line 446 of file tls_session.cpp.
References BOTAN_STATE_CHECK.
◆ lifetime_hint()
|
inline |
- Returns
- the lifetime of the ticket as defined by the TLS server
Definition at line 366 of file tls_session.h.
Referenced by Session(), Session(), Session(), and Botan::TLS::Callbacks::tls_should_persist_resumption_information().
◆ master_secret()
|
inline |
Get a reference to the contained master secret
Definition at line 341 of file tls_session.h.
Referenced by Session().
◆ max_early_data_bytes()
|
inline |
Return the number of bytes allowed for 0-RTT early data
Definition at line 361 of file tls_session.h.
Referenced by Session().
◆ peer_certs()
|
inlineinherited |
Return the certificate chain of the peer (possibly empty)
Definition at line 111 of file tls_session.h.
References m_peer_certs.
Referenced by Botan::TLS::Session_Summary::Client_Impl_13, Botan::TLS::Session::Session(), and Session_Base().
◆ peer_credential_type()
|
inlineinherited |
Return the type of credential used by the peer, or std::nullopt if the peer did not authenticate itself
Definition at line 122 of file tls_session.h.
References m_peer_certs, m_peer_raw_public_key, Botan::TLS::RawPublicKey, and Botan::TLS::X509.
◆ peer_raw_public_key()
|
inlineinherited |
Return the raw public key of the peer (possibly empty)
Definition at line 116 of file tls_session.h.
References m_peer_raw_public_key.
Referenced by Botan::TLS::Session_Summary::Client_Impl_13, Botan::TLS::Session::Session(), and Session_Base().
◆ PEM_encode()
| std::string Botan::TLS::Session::PEM_encode | ( | ) | const |
Encode this session data for storage
- Warning
- if the master secret is compromised so is the session traffic
Definition at line 442 of file tls_session.cpp.
References DER_encode(), and Botan::PEM_Code::encode().
◆ server_info()
|
inlineinherited |
Get information about the TLS server
Returns information that identifies the server side of the connection. This is useful for the client in that it identifies what was originally passed to the constructor. For the server, it includes the name the client specified in the server name indicator extension.
Definition at line 142 of file tls_session.h.
References m_server_info.
Referenced by Botan::TLS::Client_Hello_12::Client_Hello_12(), Botan::TLS::Session_Summary::Client_Impl_13, Botan::TLS::Session::Session(), Botan::TLS::Session::Session(), Session_Base(), and Botan::TLS::Session_Manager_SQL::store().
◆ session_age_add()
|
inline |
Return the ticket obfuscation adder
Definition at line 356 of file tls_session.h.
◆ side()
|
inlineinherited |
Get which side of the connection we are/were acting as.
Definition at line 89 of file tls_session.h.
References m_connection_side.
Referenced by Botan::TLS::Session_Summary::Client_Impl_13, Botan::TLS::Session_Manager::establish(), Botan::TLS::Session_Manager_Stateless::establish(), Botan::TLS::Session::Session(), Botan::TLS::Session::Session(), and Botan::TLS::Session_Manager_SQL::store().
◆ start_time()
|
inlineinherited |
Get the wall clock time this session began
Definition at line 69 of file tls_session.h.
References m_start_time.
Referenced by Botan::TLS::Session_Manager_In_Memory::find_some(), Botan::TLS::Session::Session(), Session_Base(), and Botan::TLS::Session_Manager_SQL::store().
◆ supports_early_data()
|
inline |
Get whether the saved session supports sending/receiving of early data
Definition at line 351 of file tls_session.h.
◆ supports_encrypt_then_mac()
|
inlineinherited |
Returns true if a TLS 1.2 session negotiated "encrypt then MAC"; TLS 1.3 sessions will always return false as they always use an AEAD.
Definition at line 100 of file tls_session.h.
References m_encrypt_then_mac.
Referenced by Botan::TLS::Client_Hello_12::Client_Hello_12(), and Botan::TLS::Server_Hello_12::Server_Hello_12().
◆ supports_extended_master_secret()
|
inlineinherited |
Returns true if a TLS 1.2 session negotiated "extended master secret"; TLS 1.3 sessions will always return true (see RFC 8446 Appendix D).
Definition at line 106 of file tls_session.h.
References m_extended_master_secret.
◆ version()
|
inlineinherited |
Get the negotiated protocol version of the TLS session
Definition at line 74 of file tls_session.h.
References m_version.
Referenced by Botan::TLS::Client_Hello_12::Client_Hello_12(), Botan::TLS::Session_Manager_Hybrid::establish(), Botan::TLS::Session::Session(), Botan::TLS::Session::Session(), Session_Base(), and Botan::TLS::Callbacks::tls_should_persist_resumption_information().
Member Data Documentation
◆ m_ciphersuite
|
protectedinherited |
Definition at line 148 of file tls_session.h.
Referenced by ciphersuite(), ciphersuite_code(), Botan::TLS::Session::DER_encode(), Botan::TLS::Session::Session(), and Session_Base().
◆ m_connection_side
|
protectedinherited |
Definition at line 149 of file tls_session.h.
Referenced by Botan::TLS::Session::DER_encode(), Botan::TLS::Session::Session(), Session_Base(), and side().
◆ m_encrypt_then_mac
|
protectedinherited |
Definition at line 153 of file tls_session.h.
Referenced by Botan::TLS::Session::DER_encode(), Botan::TLS::Session::Session(), Session_Base(), and supports_encrypt_then_mac().
◆ m_extended_master_secret
|
protectedinherited |
Definition at line 152 of file tls_session.h.
Referenced by Botan::TLS::Session::DER_encode(), Botan::TLS::Session::Session(), Session_Base(), and supports_extended_master_secret().
◆ m_peer_certs
|
protectedinherited |
Definition at line 155 of file tls_session.h.
Referenced by Botan::TLS::Session::DER_encode(), peer_certs(), peer_credential_type(), Botan::TLS::Session::Session(), and Session_Base().
◆ m_peer_raw_public_key
|
protectedinherited |
Definition at line 156 of file tls_session.h.
Referenced by Botan::TLS::Session::DER_encode(), peer_credential_type(), peer_raw_public_key(), Botan::TLS::Session::Session(), and Session_Base().
◆ m_server_info
|
protectedinherited |
Definition at line 157 of file tls_session.h.
Referenced by Botan::TLS::Session::DER_encode(), server_info(), Botan::TLS::Session::Session(), and Session_Base().
◆ m_srtp_profile
|
protectedinherited |
Definition at line 150 of file tls_session.h.
Referenced by Botan::TLS::Session::DER_encode(), dtls_srtp_profile(), Botan::TLS::Session::Session(), and Session_Base().
◆ m_start_time
|
protectedinherited |
Definition at line 145 of file tls_session.h.
Referenced by Botan::TLS::Session::DER_encode(), Botan::TLS::Session::Session(), Session_Base(), and start_time().
◆ m_version
|
protectedinherited |
Definition at line 147 of file tls_session.h.
Referenced by Botan::TLS::Session::DER_encode(), Botan::TLS::Session::Session(), Session_Base(), and version().
The documentation for this class was generated from the following files:
- src/lib/tls/tls_session.h
- src/lib/tls/tls_session.cpp
Generated by
 1.16.1