#include <tls_channel.h>
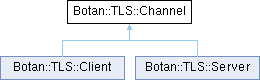
Public Member Functions | |
| virtual std::string | application_protocol () const =0 |
| Channel (Channel &&other)=default | |
| Channel (const Channel &other)=delete | |
| virtual void | close ()=0 |
| virtual std::optional< std::string > | external_psk_identity () const =0 |
| virtual bool | is_active () const =0 |
| virtual bool | is_closed () const =0 |
| virtual bool | is_closed_for_reading () const =0 |
| virtual bool | is_closed_for_writing () const =0 |
| virtual bool | is_handshake_complete () const =0 |
| virtual SymmetricKey | key_material_export (std::string_view label, std::string_view context, size_t length) const =0 |
| virtual std::optional< std::chrono::milliseconds > | next_retransmission_timeout () const =0 |
| Channel & | operator= (Channel &&other)=delete |
| Channel & | operator= (const Channel &other)=delete |
| virtual std::vector< X509_Certificate > | peer_cert_chain () const =0 |
| virtual std::shared_ptr< const Public_Key > | peer_raw_public_key () const =0 |
| size_t | received_data (const uint8_t buf[], size_t buf_size) |
| size_t | received_data (std::span< const uint8_t > data) |
| virtual void | renegotiate (bool force_full_renegotiation=false)=0 |
| virtual bool | secure_renegotiation_supported () const =0 |
| void | send (const uint8_t buf[], size_t buf_size) |
| void | send (std::span< const uint8_t > data) |
| void | send (std::string_view s) |
| virtual void | send_alert (const Alert &alert)=0 |
| virtual void | send_fatal_alert (Alert::Type type)=0 |
| virtual void | send_warning_alert (Alert::Type type)=0 |
| virtual bool | timeout_check ()=0 |
| virtual void | update_traffic_keys (bool request_peer_update=false)=0 |
| virtual | ~Channel ()=default |
Static Public Attributes | |
| static constexpr size_t | IO_BUF_DEFAULT_SIZE = 10 * 1024 |
Protected Member Functions | |
| Channel ()=default | |
| virtual size_t | from_peer (std::span< const uint8_t > data)=0 |
| virtual void | to_peer (std::span< const uint8_t > data)=0 |
Detailed Description
Generic interface for TLS endpoint
Definition at line 36 of file tls_channel.h.
Constructor & Destructor Documentation
◆ ~Channel()
|
virtualdefault |
◆ Channel() [1/3]
|
delete |
References Channel().
Referenced by Channel(), Channel(), operator=(), and operator=().
◆ Channel() [2/3]
|
default |
References Channel().
◆ Channel() [3/3]
|
protecteddefault |
Member Function Documentation
◆ application_protocol()
|
pure virtual |
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References application_protocol().
Referenced by application_protocol().
◆ close()
|
pure virtual |
Send a close notification alert
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
◆ external_psk_identity()
|
pure virtual |
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References external_psk_identity().
Referenced by external_psk_identity().
◆ from_peer()
|
protectedpure virtual |
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
Referenced by received_data(), and received_data().
◆ is_active()
|
pure virtual |
Check whether the connection is ready to send application data. Note that a TLS 1.3 server MAY send data before receiving the client's Finished message. Only after receiving the client's Finished, can the server be sure about the client's liveness and (optional) identity.
Consider using is_handshake_complete() if you need to wait until the handshake if fully complete.
- Returns
- true iff the connection is active for sending application data
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
◆ is_closed()
|
pure virtual |
Note: For TLS 1.3 a connection is closed only after both peers have signaled a "close_notify". While TLS 1.2 automatically responded in suit once the peer had sent "close_notify", TLS 1.3 allows to continue transmitting data even if the peer closed their writing end.
- Returns
- true iff the connection has been definitely closed
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References is_closed().
Referenced by is_closed().
◆ is_closed_for_reading()
|
pure virtual |
- Returns
- true iff the peer closed their channel (i.e. no more incoming data expected)
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References is_closed_for_reading().
Referenced by is_closed_for_reading().
◆ is_closed_for_writing()
|
pure virtual |
- Returns
- true iff we closed our channel (i.e. no more outgoing data allowed)
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References is_closed_for_writing().
Referenced by is_closed_for_writing().
◆ is_handshake_complete()
|
pure virtual |
Becomes true as soon as the TLS handshake is fully complete and all security assurances TLS provides can be guaranteed.
- Returns
- true once the TLS handshake has finished successfully
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
◆ key_material_export()
|
pure virtual |
Key material export (RFC 5705)
- Parameters
-
label a disambiguating label string context a per-association context value length the length of the desired key in bytes
- Returns
- key of length bytes
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References key_material_export().
Referenced by key_material_export().
◆ next_retransmission_timeout()
|
pure virtual |
- Returns
- the remaining time until timeout_check() might retransmit handshake data, or std::nullopt if no timeout check is needed.
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References next_retransmission_timeout().
Referenced by next_retransmission_timeout().
◆ operator=() [1/2]
◆ operator=() [2/2]
◆ peer_cert_chain()
|
pure virtual |
- Returns
- certificate chain of the peer (may be empty)
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References peer_cert_chain().
Referenced by peer_cert_chain().
◆ peer_raw_public_key()
|
pure virtual |
- Returns
- raw public key of the peer (may be nullptr)
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References peer_raw_public_key().
Referenced by peer_raw_public_key().
◆ received_data() [1/2]
|
inline |
Definition at line 61 of file tls_channel.h.
References from_peer().
◆ received_data() [2/2]
|
inline |
Inject TLS traffic received from counterparty
- Returns
- a hint as to how many more bytes we need to process the current record (this may be 0 if on a record boundary)
Definition at line 59 of file tls_channel.h.
References from_peer().
◆ renegotiate()
|
pure virtual |
Attempt to renegotiate the session
- Parameters
-
force_full_renegotiation if true, require a full renegotiation, otherwise allow session resumption
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References renegotiate().
Referenced by renegotiate().
◆ secure_renegotiation_supported()
|
pure virtual |
- Returns
- true iff the counterparty supports the secure renegotiation extensions.
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References BOTAN_DEPRECATED, and secure_renegotiation_supported().
Referenced by secure_renegotiation_supported().
◆ send() [1/3]
|
inline |
Definition at line 69 of file tls_channel.h.
References to_peer().
◆ send() [2/3]
|
inline |
Inject plaintext intended for counterparty Throws an exception if is_active() is false
Definition at line 67 of file tls_channel.h.
References to_peer().
◆ send() [3/3]
|
inline |
Inject plaintext intended for counterparty Throws an exception if is_active() is false
Definition at line 75 of file tls_channel.h.
References send().
Referenced by send().
◆ send_alert()
|
pure virtual |
Inject plaintext intended for counterparty Throws an exception if is_active() is false Send a TLS alert message. If the alert is fatal, the internal state (keys, etc) will be reset.
- Parameters
-
alert the Alert to send
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
◆ send_fatal_alert()
|
pure virtual |
Send a fatal alert
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
◆ send_warning_alert()
|
pure virtual |
Send a warning alert
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
◆ timeout_check()
|
pure virtual |
Perform a handshake timeout check.
This function does nothing unless the channel represents a DTLS connection with a handshake in progress.
Consider using Callbacks::tls_register_deferred_operation introduced in Botan 3.14.0 to handle retransmission timers transparently instead of polling this function at regular intervals. Never do both, though!
By default after a certain interval where no progress has been made in the handshake (controlled by the policy values TLS::Policy::dtls_initial_timeout, TLS::Policy::dtls_maximum_timeout, and TLS::Policy::dtls_maximum_retransmissions), calling timeout_check will throw indicating the handshake has failed to complete. If you wish to never fully timeout, this can be accomplished by overriding TLS::Policy::dtls_maximum_retransmissions to return std::nullopt, in which case a handshake attempt will retry indefinitely.
- Returns
- true if a timeout condition occurred
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References timeout_check().
Referenced by timeout_check().
◆ to_peer()
|
protectedpure virtual |
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
◆ update_traffic_keys()
|
pure virtual |
Attempt to update the session's traffic key material Note that this is possible with a TLS 1.3 channel, only.
- Parameters
-
request_peer_update if true, require a reciprocal key update
Implemented in Botan::TLS::Client, and Botan::TLS::Server.
References update_traffic_keys().
Referenced by update_traffic_keys().
Member Data Documentation
◆ IO_BUF_DEFAULT_SIZE
|
staticconstexpr |
Definition at line 38 of file tls_channel.h.
Referenced by Botan::TLS::Server_Impl_12::Server_Impl_12().
The documentation for this class was generated from the following file:
- src/lib/tls/tls_channel.h
Generated by
 1.16.1