#include <hmac_drbg.h>
Public Member Functions | |
| bool | accepts_input () const final |
| void | add_entropy (const uint8_t input[], size_t length) |
| void | add_entropy (std::span< const uint8_t > input) |
| template<typename T> | |
| void | add_entropy_T (const T &t) |
| void | clear () final |
| void | force_reseed () |
| HMAC_DRBG (const HMAC_DRBG &rng)=delete | |
| HMAC_DRBG (HMAC_DRBG &&rng)=delete | |
| HMAC_DRBG (std::string_view hmac_hash) | |
| HMAC_DRBG (std::unique_ptr< MessageAuthenticationCode > prf) | |
| HMAC_DRBG (std::unique_ptr< MessageAuthenticationCode > prf, Entropy_Sources &entropy_sources, size_t reseed_interval=RandomNumberGenerator::DefaultReseedInterval, size_t max_number_of_bytes_per_request=64 *1024) | |
| HMAC_DRBG (std::unique_ptr< MessageAuthenticationCode > prf, RandomNumberGenerator &underlying_rng, Entropy_Sources &entropy_sources, size_t reseed_interval=RandomNumberGenerator::DefaultReseedInterval, size_t max_number_of_bytes_per_request=64 *1024) | |
| HMAC_DRBG (std::unique_ptr< MessageAuthenticationCode > prf, RandomNumberGenerator &underlying_rng, size_t reseed_interval=RandomNumberGenerator::DefaultReseedInterval, size_t max_number_of_bytes_per_request=64 *1024) | |
| void | initialize_with (const uint8_t input[], size_t length) |
| void | initialize_with (std::span< const uint8_t > input) |
| bool | is_seeded () const final |
| size_t | max_number_of_bytes_per_request () const override |
| std::string | name () const override |
| uint8_t | next_byte () |
| uint8_t | next_nonzero_byte () |
| HMAC_DRBG & | operator= (const HMAC_DRBG &rng)=delete |
| HMAC_DRBG & | operator= (HMAC_DRBG &&rng)=delete |
| template<size_t bytes> | |
| std::array< uint8_t, bytes > | random_array () |
| template<concepts::resizable_byte_buffer T = secure_vector<uint8_t>> | |
| T | random_vec (size_t bytes) |
| void | random_vec (std::span< uint8_t > v) |
| template<concepts::resizable_byte_buffer T> | |
| void | random_vec (T &v, size_t bytes) |
| void | randomize (std::span< uint8_t > output) |
| void | randomize (uint8_t output[], size_t length) |
| void | randomize_with_input (std::span< uint8_t > output, std::span< const uint8_t > input) |
| void | randomize_with_input (uint8_t output[], size_t output_len, const uint8_t input[], size_t input_len) |
| void | randomize_with_ts_input (std::span< uint8_t > output) |
| void | randomize_with_ts_input (uint8_t output[], size_t output_len) |
| size_t | reseed (Entropy_Sources &srcs, size_t poll_bits=RandomNumberGenerator::DefaultPollBits, std::chrono::milliseconds=DefaultPollTimeout) |
| size_t | reseed_from (Entropy_Sources &srcs, size_t poll_bits=RandomNumberGenerator::DefaultPollBits) |
| void | reseed_from (RandomNumberGenerator &rng, size_t poll_bits=RandomNumberGenerator::DefaultPollBits) |
| void | reseed_from_rng (RandomNumberGenerator &rng, size_t poll_bits=RandomNumberGenerator::DefaultPollBits) final |
| size_t | reseed_from_sources (Entropy_Sources &srcs, size_t poll_bits=RandomNumberGenerator::DefaultPollBits) final |
| size_t | reseed_interval () const |
| size_t | security_level () const override |
| ~HMAC_DRBG () override | |
Static Public Attributes | |
| static constexpr size_t | DefaultPollBits = 256 |
| static constexpr auto | DefaultPollTimeout = std::chrono::milliseconds(50) |
| static constexpr size_t | DefaultReseedInterval = 1024 |
Protected Member Functions | |
| void | reseed_check () |
Detailed Description
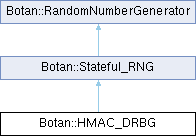
HMAC_DRBG from NIST SP800-90A
Definition at line 22 of file hmac_drbg.h.
Constructor & Destructor Documentation
◆ HMAC_DRBG() [1/7]
|
explicit |
Initialize an HMAC_DRBG instance with the given MAC as PRF (normally HMAC)
Automatic reseeding is disabled completely, as it has no access to any source for seed material.
If a fork is detected, the RNG will be unable to reseed itself in response. In this case, an exception will be thrown rather than generating duplicated output.
Definition at line 102 of file hmac_drbg.cpp.
References Botan::Stateful_RNG::clear().
Referenced by HMAC_DRBG(), HMAC_DRBG(), operator=(), and operator=().
◆ HMAC_DRBG() [2/7]
|
explicit |
Constructor taking a string for the hash
Definition at line 109 of file hmac_drbg.cpp.
References Botan::Stateful_RNG::clear(), and Botan::fmt().
◆ HMAC_DRBG() [3/7]
| Botan::HMAC_DRBG::HMAC_DRBG | ( | std::unique_ptr< MessageAuthenticationCode > | prf, |
| RandomNumberGenerator & | underlying_rng, | ||
| size_t | reseed_interval = RandomNumberGenerator::DefaultReseedInterval, | ||
| size_t | max_number_of_bytes_per_request = 64 * 1024 ) |
Initialize an HMAC_DRBG instance with the given MAC as PRF (normally HMAC)
Automatic reseeding from underlying_rng will take place after reseed_interval many requests or after a fork was detected.
- Parameters
-
prf MAC to use as a PRF underlying_rng is a reference to some RNG which will be used to perform the periodic reseeding reseed_interval specifies a limit of how many times the RNG will be called before automatic reseeding is performed (max. 2^24) max_number_of_bytes_per_request requests that are in size higher than max_number_of_bytes_per_request are treated as if multiple single requests of max_number_of_bytes_per_request size had been made. In theory SP 800-90A requires that we reject any request for a DRBG output longer than max_number_of_bytes_per_request. To avoid inconveniencing the caller who wants an output larger than max_number_of_bytes_per_request, instead treat these requests as if multiple requests of max_number_of_bytes_per_request size had been made. NIST requires for HMAC_DRBG that every implementation set a value no more than 2**19 bits (or 64 KiB). Together with reseed_interval= 1 you can enforce that for example every 512 bit automatic reseeding occurs.
Definition at line 62 of file hmac_drbg.cpp.
References Botan::Stateful_RNG::clear(), max_number_of_bytes_per_request(), Botan::Stateful_RNG::reseed_interval(), and Botan::Stateful_RNG::Stateful_RNG().
◆ HMAC_DRBG() [4/7]
| Botan::HMAC_DRBG::HMAC_DRBG | ( | std::unique_ptr< MessageAuthenticationCode > | prf, |
| Entropy_Sources & | entropy_sources, | ||
| size_t | reseed_interval = RandomNumberGenerator::DefaultReseedInterval, | ||
| size_t | max_number_of_bytes_per_request = 64 * 1024 ) |
Initialize an HMAC_DRBG instance with the given MAC as PRF (normally HMAC)
Automatic reseeding from entropy_sources will take place after reseed_interval many requests or after a fork was detected.
- Parameters
-
prf MAC to use as a PRF entropy_sources will be polled to perform reseeding periodically reseed_interval specifies a limit of how many times the RNG will be called before automatic reseeding is performed (max. 2^24) max_number_of_bytes_per_request requests that are in size higher than max_number_of_bytes_per_request are treated as if multiple single requests of max_number_of_bytes_per_request size had been made. In theory SP 800-90A requires that we reject any request for a DRBG output longer than max_number_of_bytes_per_request. To avoid inconveniencing the caller who wants an output larger than max_number_of_bytes_per_request, instead treat these requests as if multiple requests of max_number_of_bytes_per_request size had been made. NIST requires for HMAC_DRBG that every implementation set a value no more than 2**19 bits (or 64 KiB). Together with reseed_interval= 1 you can enforce that for example every 512 bit automatic reseeding occurs.
Definition at line 89 of file hmac_drbg.cpp.
References Botan::Stateful_RNG::clear(), max_number_of_bytes_per_request(), Botan::Stateful_RNG::reseed_interval(), and Botan::Stateful_RNG::Stateful_RNG().
◆ HMAC_DRBG() [5/7]
| Botan::HMAC_DRBG::HMAC_DRBG | ( | std::unique_ptr< MessageAuthenticationCode > | prf, |
| RandomNumberGenerator & | underlying_rng, | ||
| Entropy_Sources & | entropy_sources, | ||
| size_t | reseed_interval = RandomNumberGenerator::DefaultReseedInterval, | ||
| size_t | max_number_of_bytes_per_request = 64 * 1024 ) |
Initialize an HMAC_DRBG instance with the given MAC as PRF (normally HMAC)
Automatic reseeding from underlying_rng and entropy_sources will take place after reseed_interval many requests or after a fork was detected.
- Parameters
-
prf MAC to use as a PRF underlying_rng is a reference to some RNG which will be used to perform the periodic reseeding entropy_sources will be polled to perform reseeding periodically reseed_interval specifies a limit of how many times the RNG will be called before automatic reseeding is performed (max. 2^24) max_number_of_bytes_per_request requests that are in size higher than max_number_of_bytes_per_request are treated as if multiple single requests of max_number_of_bytes_per_request size had been made. In theory SP 800-90A requires that we reject any request for a DRBG output longer than max_number_of_bytes_per_request. To avoid inconveniencing the caller who wants an output larger than max_number_of_bytes_per_request, instead treat these requests as if multiple requests of max_number_of_bytes_per_request size had been made. NIST requires for HMAC_DRBG that every implementation set a value no more than 2**19 bits (or 64 KiB). Together with reseed_interval= 1 you can enforce that for example every 512 bit automatic reseeding occurs.
Definition at line 75 of file hmac_drbg.cpp.
References Botan::Stateful_RNG::clear(), max_number_of_bytes_per_request(), Botan::Stateful_RNG::reseed_interval(), and Botan::Stateful_RNG::Stateful_RNG().
◆ ~HMAC_DRBG()
|
overridedefault |
◆ HMAC_DRBG() [6/7]
|
delete |
References HMAC_DRBG().
◆ HMAC_DRBG() [7/7]
|
delete |
References HMAC_DRBG().
Member Function Documentation
◆ accepts_input()
|
inlinefinalvirtualinherited |
Test whether this RNG accepts externally provided input
- Returns
- false if this RNG is known to ignore provided inputs
Implements Botan::RandomNumberGenerator.
Definition at line 103 of file stateful_rng.h.
References accepts_input().
Referenced by accepts_input().
◆ add_entropy() [1/2]
|
inlineinherited |
Provide seed material to the RNG, see add_entropy
- Parameters
-
input a byte array containing the entropy to be added length the number of bytes in input
Definition at line 128 of file rng.h.
References add_entropy().
Referenced by add_entropy().
◆ add_entropy() [2/2]
|
inlineinherited |
Provide seed material to the RNG.
The caller asserts that the input is full entropy seed material. For a stateful RNG such as HMAC_DRBG, an input of at least security_level() bits marks the RNG as seeded.
To mix in data of unknown quality (nonces, timestamps, values from a peer's protocol message) without affecting the seeded state, instead call randomize_with_input with an empty output buffer.
A few RNG types do not accept any externally provided input, in which case this function is a no-op.
- Parameters
-
input a byte array containing the entropy to be added
Definition at line 121 of file rng.h.
References accept_seed_material().
Referenced by add_entropy_T(), Botan::ChaCha_RNG::ChaCha_RNG(), Botan::Stateful_RNG::initialize_with(), and reseed_from_rng().
◆ add_entropy_T()
|
inlineinherited |
Provide seed material to the RNG, see add_entropy
Definition at line 135 of file rng.h.
References add_entropy().
◆ clear()
|
finalvirtualinherited |
Clear all internally held values of this RNG
Implements Botan::RandomNumberGenerator.
Definition at line 39 of file stateful_rng.cpp.
References clear_state(), and Botan::lock().
Referenced by Botan::ChaCha_RNG::ChaCha_RNG(), Botan::ChaCha_RNG::ChaCha_RNG(), Botan::ChaCha_RNG::ChaCha_RNG(), Botan::ChaCha_RNG::ChaCha_RNG(), Botan::HMAC_DRBG::HMAC_DRBG(), Botan::HMAC_DRBG::HMAC_DRBG(), Botan::HMAC_DRBG::HMAC_DRBG(), Botan::HMAC_DRBG::HMAC_DRBG(), Botan::HMAC_DRBG::HMAC_DRBG(), and initialize_with().
◆ force_reseed()
|
inherited |
Mark state as requiring a reseed on next use
Definition at line 47 of file stateful_rng.cpp.
References Botan::lock().
◆ initialize_with() [1/2]
|
inlineinherited |
Reset the RNG then consume this input as seed material
The RNG is marked as seeded only if the input is at least security_level() bits long.
- Parameters
-
input the seed material length the number of bytes in input
Definition at line 91 of file stateful_rng.h.
References initialize_with().
Referenced by initialize_with().
◆ initialize_with() [2/2]
|
inherited |
Reset the RNG then consume this input as seed material
The RNG is marked as seeded only if the input is at least security_level() bits long.
Definition at line 57 of file stateful_rng.cpp.
References Botan::RandomNumberGenerator::add_entropy(), clear(), and Botan::lock().
Referenced by operator=().
◆ is_seeded()
|
finalvirtualinherited |
Test whether this RNG has been seeded
- Returns
- true if this RNG is seeded and ready for use
Implements Botan::RandomNumberGenerator.
Definition at line 52 of file stateful_rng.cpp.
References Botan::lock().
Referenced by reseed_check().
◆ max_number_of_bytes_per_request()
|
inlineoverridevirtual |
Return the largest number of bytes this DRBG will produce per request
- Returns
- the maximum request size in bytes
Implements Botan::Stateful_RNG.
Definition at line 151 of file hmac_drbg.h.
Referenced by HMAC_DRBG(), HMAC_DRBG(), and HMAC_DRBG().
◆ name()
|
overridevirtual |
Return the name of this RNG type
- Returns
- the name of this RNG type
Implements Botan::RandomNumberGenerator.
Definition at line 129 of file hmac_drbg.cpp.
References Botan::fmt().
◆ next_byte()
|
inlineinherited |
Return a random byte
- Returns
- random byte
- Exceptions
-
PRNG_Unseeded if the RNG fails because it has not enough entropy Exception if the RNG fails
Definition at line 302 of file rng.h.
References fill_bytes_with_input().
Referenced by next_nonzero_byte(), and Botan::random_prime().
◆ next_nonzero_byte()
|
inlineinherited |
Generate a single random byte which is not zero
- Returns
- a random byte that is greater than zero
- Exceptions
-
PRNG_Unseeded if the RNG fails because it has not enough entropy Exception if the RNG fails
Definition at line 314 of file rng.h.
References next_byte().
◆ operator=() [1/2]
References HMAC_DRBG().
◆ operator=() [2/2]
References HMAC_DRBG(), and security_level().
◆ random_array()
|
inlineinherited |
Create a std::array of bytes random bytes
Definition at line 290 of file rng.h.
References random_vec().
Referenced by Botan::generate_rsa_prime().
◆ random_vec() [1/3]
|
inlineinherited |
Create some byte container type and fill it with some random bytes.
- Template Parameters
-
T the desired byte container type (e.g std::vector<uint8_t>)
- Parameters
-
bytes number of random bytes to initialize the container with
- Returns
- a container of type T with
bytesrandom bytes
Definition at line 280 of file rng.h.
References random_vec().
◆ random_vec() [2/3]
|
inlineinherited |
Fill a given byte container with bytes random bytes
- Todo
- deprecate this overload (in favor of randomize())
- Parameters
-
v the container to be filled with bytesrandom bytes
Definition at line 254 of file rng.h.
References randomize().
Referenced by Botan::Classic_McEliece_PrivateKey::Classic_McEliece_PrivateKey(), Botan::TLS::Client_Key_Exchange::Client_Key_Exchange(), Botan::TLS::Client_Key_Exchange::Client_Key_Exchange(), Botan::PK_Decryptor::decrypt_or_random(), Botan::Dilithium_PrivateKey::Dilithium_PrivateKey(), Botan::Ed25519_PrivateKey::Ed25519_PrivateKey(), Botan::Kyber_KEM_Encryptor::encapsulate(), Botan::ML_KEM_Encryptor::encapsulate(), Botan::TLS::Session::encrypt(), Botan::KeyPair::encryption_consistency_check(), Botan::FrodoKEM_PrivateKey::FrodoKEM_PrivateKey(), Botan::generate_bcrypt(), Botan::Kyber_PrivateKey::Kyber_PrivateKey(), Botan::TLS::make_hello_random(), Botan::OctetString::OctetString(), random_array(), random_vec(), random_vec(), Botan::BigInt::randomize(), reseed_from_rng(), Botan::Stateful_RNG::reseed_from_rng(), Botan::SphincsPlus_PrivateKey::SphincsPlus_PrivateKey(), Botan::X25519_PrivateKey::X25519_PrivateKey(), and Botan::XMSS_PublicKey::XMSS_PublicKey().
◆ random_vec() [3/3]
|
inlineinherited |
Resize a given byte container to bytes and fill it with random bytes
- Template Parameters
-
T the desired byte container type (e.g std::vector<uint8_t>)
- Parameters
-
v the container to be filled with bytesrandom bytesbytes number of random bytes to initialize the container with
Definition at line 265 of file rng.h.
References random_vec().
◆ randomize() [1/2]
|
inlineinherited |
Randomize a byte array.
May block shortly if e.g. the RNG is not yet initialized or a retry because of insufficient entropy is needed.
- Parameters
-
output the byte array to hold the random output.
- Exceptions
-
PRNG_Unseeded if the RNG fails because it has not enough entropy Exception if the RNG fails
Definition at line 86 of file rng.h.
References fill_bytes_with_input().
Referenced by Botan::TLS::Connection_Cipher_State::aead_nonce(), Botan::argon2_generate_pwhash(), Botan::BlindingRandomness< BlindedScalar, Scalars >::BlindingRandomness(), botan_system_rng_get(), Botan::CryptoBox::encrypt(), Botan::PKCS12::export_to(), Botan::generate_dsa_primes(), Botan::generate_passhash9(), Botan::pkcs12_pbe_encrypt(), Botan::IntMod< MontgomeryRep< ScalarParams > >::random(), Botan::X509_Serial_Number::random(), Botan::random_gf2m(), Botan::McEliece_PublicKeyInternal::random_plaintext_element(), Botan::random_prime(), random_vec(), Botan::Sodium::randombytes_buf(), Botan::KeyPair::signature_consistency_check(), Botan::RTSS_Share::split(), and Botan::UUID::UUID().
◆ randomize() [2/2]
|
inlineinherited |
Randomize a byte array
- Parameters
-
output the byte array to hold the random output length the number of bytes to generate
Definition at line 93 of file rng.h.
References randomize().
Referenced by randomize().
◆ randomize_with_input() [1/2]
|
inlineinherited |
Incorporate additional input into the RNG state then produce output.
Use this to further bind the outputs to your current process/protocol state. For instance if generating a new key for use in a session, include a session ID or other such value. See NIST SP 800-90 A, B, C series for more ideas.
The input is never credited as entropy: if the output buffer is empty, the input is mixed into the state of a stateful RNG without affecting whether it is considered seeded. Use add_entropy to provide seed material.
- Parameters
-
output buffer to hold the random output input entropy buffer to incorporate
- Exceptions
-
PRNG_Unseeded if the RNG fails because it has not enough entropy Exception if the RNG fails Exception may throw if the RNG accepts input, but adding the entropy failed.
Definition at line 158 of file rng.h.
References fill_bytes_with_input().
Referenced by Botan::System_RNG::fill_bytes_with_input(), and randomize_with_input().
◆ randomize_with_input() [2/2]
|
inlineinherited |
Randomize a byte array, first incorporating additional input
- Parameters
-
output the byte array to hold the random output output_len the number of bytes to generate input a byte array containing the entropy to be added input_len the number of bytes in input
Definition at line 169 of file rng.h.
References randomize_with_input().
◆ randomize_with_ts_input() [1/2]
|
inherited |
This calls randomize_with_input using system specific values
This first attempts to provide input to the underlying RNG from some system specific source. The additional input consists of an 8 byte timestamp from the local clock. The remainder of the 22 byte input is filled from the system RNG if available, otherwise the current process ID is appended.
For a stateful RNG that was already correctly seeded with sufficient cryptographically secure material, using non-random but potentially unique data as the extra input can help protect against problems with fork, VM state rollback, or other cases where somehow an RNG state is duplicated. If both of the duplicated RNG states later incorporate some input, even predictable input, their outputs will diverge.
- Parameters
-
output buffer to hold the random output
- Exceptions
-
PRNG_Unseeded if the RNG fails because it has not enough entropy Exception if the RNG fails Exception may throw if the RNG accepts input, but adding the entropy failed.
Definition at line 73 of file rng.cpp.
References accepts_input(), and fill_bytes_with_input().
Referenced by randomize_with_ts_input().
◆ randomize_with_ts_input() [2/2]
|
inlineinherited |
Randomize a byte array, using timestamps as additional input
- Parameters
-
output the byte array to hold the random output output_len the number of bytes to generate
Definition at line 200 of file rng.h.
References randomize_with_ts_input().
◆ reseed()
|
inlineinherited |
Poll provided sources for up to poll_bits bits of entropy. Returns estimate of the number of bits collected.
Sets the seeded state to true if enough entropy was added.
TODO(Botan4) remove this function
Definition at line 347 of file rng.h.
References DefaultPollBits, DefaultPollTimeout, RandomNumberGenerator(), reseed(), and reseed_from().
Referenced by reseed().
◆ reseed_check()
|
protectedinherited |
Reseed if the reseed interval has elapsed, or throw if unseeded
Definition at line 160 of file stateful_rng.cpp.
References BOTAN_ASSERT, is_seeded(), Botan::RandomNumberGenerator::name(), reseed_from_rng(), reseed_from_sources(), and security_level().
◆ reseed_from() [1/2]
|
inlineinherited |
Poll provided sources for up to poll_bits bits of entropy. Returns estimate of the number of bits collected. Sets the seeded state to true if enough entropy was added.
Definition at line 229 of file rng.h.
References DefaultPollBits, and reseed_from_sources().
Referenced by reseed().
◆ reseed_from() [2/2]
|
inlineinherited |
Reseed by reading specified bits from the RNG
Sets the seeded state to true if enough entropy was added.
Definition at line 240 of file rng.h.
References DefaultPollBits, RandomNumberGenerator(), and reseed_from_rng().
◆ reseed_from_rng()
|
finalvirtualinherited |
Reseed this RNG from another RNG
- Parameters
-
Random Number Generators the RNG to draw seed material from poll_bits the number of bits to collect
Reimplemented from Botan::RandomNumberGenerator.
Definition at line 139 of file stateful_rng.cpp.
References Botan::lock(), Botan::RandomNumberGenerator::random_vec(), Botan::RandomNumberGenerator::RandomNumberGenerator(), and update().
Referenced by reseed_check().
◆ reseed_from_sources()
|
finalvirtualinherited |
Poll provided sources for up to poll_bits bits of entropy. Returns estimate of the number of bits collected.
Reimplemented from Botan::RandomNumberGenerator.
Definition at line 126 of file stateful_rng.cpp.
References Botan::Entropy_Sources::_gather(), BOTAN_UNUSED, Botan::lock(), and update().
Referenced by reseed_check().
◆ reseed_interval()
|
inlineinherited |
Return how many requests may be made before automatic reseeding
- Returns
- the reseed interval, or zero if automatic reseeding is disabled
Definition at line 147 of file stateful_rng.h.
Referenced by Botan::ChaCha_RNG::ChaCha_RNG(), Botan::ChaCha_RNG::ChaCha_RNG(), Botan::ChaCha_RNG::ChaCha_RNG(), Botan::HMAC_DRBG::HMAC_DRBG(), Botan::HMAC_DRBG::HMAC_DRBG(), Botan::HMAC_DRBG::HMAC_DRBG(), Stateful_RNG(), Stateful_RNG(), and Stateful_RNG().
◆ security_level()
|
overridevirtual |
Return the security level of this DRBG
- Returns
- the estimated security level in bits
Implements Botan::Stateful_RNG.
Definition at line 185 of file hmac_drbg.cpp.
Referenced by operator=().
Member Data Documentation
◆ DefaultPollBits
|
staticconstexprinherited |
Number of entropy bits polled for reseeding userspace RNGs like HMAC_DRBG
Definition at line 50 of file rng.h.
Referenced by Botan::Entropy_Source::poll(), Botan::Entropy_Sources::poll_just(), reseed(), reseed_from(), and reseed_from().
◆ DefaultPollTimeout
|
staticconstexprinherited |
◆ DefaultReseedInterval
|
staticconstexprinherited |
The documentation for this class was generated from the following files:
- src/lib/rng/hmac_drbg/hmac_drbg.h
- src/lib/rng/hmac_drbg/hmac_drbg.cpp
Generated by
 1.16.1