#include <tls_messages_12.h>
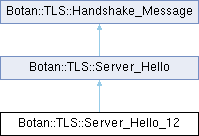
Classes | |
| class | Settings |
Public Member Functions | |
| uint16_t | ciphersuite () const |
| uint8_t | compression_method () const |
| std::set< Extension_Code > | extension_types () const |
| const Extensions & | extensions () const |
| Protocol_Version | legacy_version () const |
| std::string | next_protocol () const |
| bool | prefers_compressed_ec_points () const |
| const std::vector< uint8_t > & | random () const |
| std::optional< Protocol_Version > | random_signals_downgrade () const |
| std::vector< uint8_t > | renegotiation_info () const |
| bool | secure_renegotiation () const |
| Protocol_Version | selected_version () const final |
| std::vector< uint8_t > | serialize () const override |
| Server_Hello_12 (Handshake_IO &io, Handshake_Hash &hash, const Policy &policy, Callbacks &cb, RandomNumberGenerator &rng, std::vector< uint8_t > secure_reneg_info, const Client_Hello_12 &client_hello, const Session &resumed_session, bool offer_session_ticket, std::string_view next_protocol, TLS_Flavor flavor) | |
| Server_Hello_12 (Handshake_IO &io, Handshake_Hash &hash, const Policy &policy, Callbacks &cb, RandomNumberGenerator &rng, std::vector< uint8_t > secure_reneg_info, const Client_Hello_12 &client_hello, const Settings &settings, std::string_view next_protocol, TLS_Flavor flavor) | |
| Server_Hello_12 (std::span< const uint8_t > buf) | |
| const Session_ID & | session_id () const |
| uint16_t | srtp_profile () const |
| bool | supports_certificate_status_message () const |
| bool | supports_encrypt_then_mac () const |
| bool | supports_extended_master_secret () const |
| bool | supports_session_ticket () const |
| Handshake_Type | type () const override |
| std::string | type_string () const |
| virtual Handshake_Type | wire_type () const |
Protected Attributes | |
| std::unique_ptr< Server_Hello_Internal > | m_data |
Detailed Description
Definition at line 101 of file tls_messages_12.h.
Constructor & Destructor Documentation
◆ Server_Hello_12() [1/3]
| Botan::TLS::Server_Hello_12::Server_Hello_12 | ( | Handshake_IO & | io, |
| Handshake_Hash & | hash, | ||
| const Policy & | policy, | ||
| Callbacks & | cb, | ||
| RandomNumberGenerator & | rng, | ||
| std::vector< uint8_t > | secure_reneg_info, | ||
| const Client_Hello_12 & | client_hello, | ||
| const Settings & | settings, | ||
| std::string_view | next_protocol, | ||
| TLS_Flavor | flavor ) |
Definition at line 23 of file msg_server_hello_12.cpp.
References Botan::TLS::Ciphersuite::by_id(), Botan::TLS::Server_Hello::ciphersuite(), Botan::TLS::EcPointFormats, Botan::TLS::Client_Hello::extension_types(), Botan::TLS::Server_Hello::m_data, Botan::TLS::make_server_hello_random(), Botan::TLS::Policy::negotiate_encrypt_then_mac(), next_protocol(), Botan::TLS::Server_Hello_12::Settings::offer_session_ticket(), Botan::TLS::Client_Hello_12::secure_renegotiation(), Server_Hello_12(), Botan::TLS::Server_Hello::session_id(), Botan::TLS::Policy::support_cert_status_message(), Botan::TLS::Client_Hello::supports_alpn(), Botan::TLS::Client_Hello_12::supports_cert_status_message(), Botan::TLS::Client_Hello_12::supports_encrypt_then_mac(), Botan::TLS::Client_Hello_12::supports_extended_master_secret(), and Botan::TLS::Client_Hello_12::supports_session_ticket().
Referenced by Server_Hello_12(), Server_Hello_12(), and Server_Hello_12().
◆ Server_Hello_12() [2/3]
| Botan::TLS::Server_Hello_12::Server_Hello_12 | ( | Handshake_IO & | io, |
| Handshake_Hash & | hash, | ||
| const Policy & | policy, | ||
| Callbacks & | cb, | ||
| RandomNumberGenerator & | rng, | ||
| std::vector< uint8_t > | secure_reneg_info, | ||
| const Client_Hello_12 & | client_hello, | ||
| const Session & | resumed_session, | ||
| bool | offer_session_ticket, | ||
| std::string_view | next_protocol, | ||
| TLS_Flavor | flavor ) |
Definition at line 99 of file msg_server_hello_12.cpp.
References Botan::TLS::Ciphersuite::cbc_ciphersuite(), Botan::TLS::Session_Base::ciphersuite(), Botan::TLS::Session_Base::dtls_srtp_profile(), Botan::TLS::Ciphersuite::ecc_ciphersuite(), Botan::TLS::EcPointFormats, Botan::TLS::Client_Hello::extension_types(), Botan::TLS::Server_Hello::m_data, Botan::TLS::make_server_hello_random(), next_protocol(), Botan::TLS::Client_Hello_12::secure_renegotiation(), Botan::TLS::Handshake_IO::send(), Botan::TLS::Server, Server_Hello_12(), Botan::TLS::Server_Hello::session_id(), Botan::TLS::Client_Hello::srtp_profiles(), Botan::TLS::Client_Hello::supports_alpn(), Botan::TLS::Client_Hello_12::supports_encrypt_then_mac(), Botan::TLS::Session_Base::supports_encrypt_then_mac(), Botan::TLS::Client_Hello_12::supports_extended_master_secret(), Botan::TLS::Client_Hello_12::supports_session_ticket(), Botan::TLS::Callbacks::tls_modify_extensions(), Botan::TLS::Server_Hello::type(), Botan::TLS::Handshake_Hash::update(), and Botan::value_exists().
◆ Server_Hello_12() [3/3]
|
explicit |
Definition at line 161 of file msg_server_hello_12.cpp.
References Server_Hello_12().
Member Function Documentation
◆ ciphersuite()
|
inherited |
Definition at line 147 of file msg_server_hello.cpp.
References m_data.
Referenced by Botan::TLS::Client_Hello_13::retry(), Botan::TLS::Channel_Impl_12::secure_renegotiation_check(), Botan::TLS::Server_Hello_12::Server_Hello_12(), and ~Server_Hello().
◆ compression_method()
| uint8_t Botan::TLS::Server_Hello::compression_method | ( | ) | const |
Definition at line 198 of file msg_server_hello.cpp.
◆ extension_types()
| std::set< Extension_Code > Botan::TLS::Server_Hello::extension_types | ( | ) | const |
Definition at line 196 of file msg_server_hello.cpp.
◆ extensions()
|
inherited |
Definition at line 155 of file msg_server_hello.cpp.
References m_data.
Referenced by Botan::TLS::Server_Hello_13::basic_validation(), Botan::TLS::Client_Hello_13::retry(), Botan::TLS::Server_Hello_13::Server_Hello_13(), Botan::TLS::Server_Hello_13::Server_Hello_13(), and ~Server_Hello().
◆ legacy_version()
Definition at line 199 of file msg_server_hello.cpp.
◆ next_protocol()
| std::string Botan::TLS::Server_Hello_12::next_protocol | ( | ) | const |
Definition at line 203 of file msg_server_hello_12.cpp.
References Botan::TLS::Server_Hello::m_data.
Referenced by Server_Hello_12(), and Server_Hello_12().
◆ prefers_compressed_ec_points()
| bool Botan::TLS::Server_Hello_12::prefers_compressed_ec_points | ( | ) | const |
Definition at line 210 of file msg_server_hello_12.cpp.
References Botan::TLS::Server_Hello::m_data.
◆ random()
| const std::vector< uint8_t > & Botan::TLS::Server_Hello::random | ( | ) | const |
Definition at line 197 of file msg_server_hello.cpp.
◆ random_signals_downgrade()
|
inherited |
Return desired downgrade version indicated by hello random, if any.
Definition at line 173 of file msg_server_hello.cpp.
References Botan::TLS::DOWNGRADE_TLS11, Botan::TLS::DOWNGRADE_TLS12, Botan::load_be(), and Botan::TLS::Server_Hello::m_data.
Referenced by Server_Hello_13.
◆ renegotiation_info()
| std::vector< uint8_t > Botan::TLS::Server_Hello_12::renegotiation_info | ( | ) | const |
Definition at line 170 of file msg_server_hello_12.cpp.
References Botan::TLS::Server_Hello::m_data.
Referenced by Botan::TLS::Channel_Impl_12::secure_renegotiation_check().
◆ secure_renegotiation()
| bool Botan::TLS::Server_Hello_12::secure_renegotiation | ( | ) | const |
Definition at line 166 of file msg_server_hello_12.cpp.
References Botan::TLS::Server_Hello::m_data.
Referenced by Botan::TLS::Channel_Impl_12::secure_renegotiation_check().
◆ selected_version()
|
finalvirtualinherited |
- Returns
- the selected version as indicated in the legacy_version field
Implements Botan::TLS::Server_Hello.
Definition at line 169 of file msg_server_hello.cpp.
References Botan::TLS::Server_Hello::legacy_version().
Referenced by Server_Hello_13.
◆ serialize()
|
overridevirtualinherited |
Serialize this handshake message
Implements Botan::TLS::Handshake_Message.
Definition at line 107 of file msg_server_hello.cpp.
References Botan::TLS::append_tls_length_value(), Botan::get_byte(), m_data, serialize(), Botan::TLS::Server, and Server_Hello().
Referenced by serialize(), and ~Server_Hello().
◆ session_id()
|
inherited |
Definition at line 143 of file msg_server_hello.cpp.
References m_data.
Referenced by Botan::TLS::Hello_Retry_Request::Hello_Retry_Request(), Botan::TLS::Server_Hello_12::Server_Hello_12(), Botan::TLS::Server_Hello_12::Server_Hello_12(), Botan::TLS::Server_Hello_13::Server_Hello_13(), and ~Server_Hello().
◆ srtp_profile()
| uint16_t Botan::TLS::Server_Hello_12::srtp_profile | ( | ) | const |
Definition at line 193 of file msg_server_hello_12.cpp.
References BOTAN_ASSERT_NOMSG, and Botan::TLS::Server_Hello::m_data.
◆ supports_certificate_status_message()
| bool Botan::TLS::Server_Hello_12::supports_certificate_status_message | ( | ) | const |
Definition at line 185 of file msg_server_hello_12.cpp.
References Botan::TLS::Server_Hello::m_data.
◆ supports_encrypt_then_mac()
| bool Botan::TLS::Server_Hello_12::supports_encrypt_then_mac | ( | ) | const |
Definition at line 181 of file msg_server_hello_12.cpp.
References Botan::TLS::Server_Hello::m_data.
Referenced by Botan::TLS::Channel_Impl_12::secure_renegotiation_check().
◆ supports_extended_master_secret()
| bool Botan::TLS::Server_Hello_12::supports_extended_master_secret | ( | ) | const |
Definition at line 177 of file msg_server_hello_12.cpp.
References Botan::TLS::Server_Hello::m_data.
◆ supports_session_ticket()
| bool Botan::TLS::Server_Hello_12::supports_session_ticket | ( | ) | const |
Definition at line 189 of file msg_server_hello_12.cpp.
References Botan::TLS::Server_Hello::m_data.
◆ type()
|
overridevirtualinherited |
Return the TLS handshake type code
- Returns
- the message type
Implements Botan::TLS::Handshake_Message.
Definition at line 127 of file msg_server_hello.cpp.
References Botan::TLS::ServerHello.
Referenced by Botan::TLS::Server_Hello_12::Server_Hello_12(), and ~Server_Hello().
◆ type_string()
|
inherited |
Return a free-form string describing this message type
- Returns
- string representation of this message type
Definition at line 22 of file tls_handshake_state.cpp.
References Botan::TLS::handshake_type_to_string(), and type().
◆ wire_type()
|
inlinevirtualinherited |
Return the wire encoding of the message type code
- Returns
- the wire representation of the message's type
Reimplemented in Botan::TLS::Hello_Retry_Request.
Definition at line 47 of file tls_handshake_msg.h.
References type().
Referenced by Botan::TLS::Stream_Handshake_IO::send(), and Botan::TLS::Handshake_Layer::update_transcript_for_psk_binder_calc().
Member Data Documentation
◆ m_data
|
protectedinherited |
Definition at line 202 of file tls_messages.h.
Referenced by ciphersuite(), compression_method(), Botan::TLS::Server_Hello_13::decline_psk(), extension_types(), extensions(), Botan::TLS::Hello_Retry_Request::Hello_Retry_Request(), legacy_version(), Botan::TLS::Server_Hello_12::next_protocol(), Botan::TLS::Server_Hello_12::prefers_compressed_ec_points(), random(), Botan::TLS::Server_Hello_12_Shim::random_signals_downgrade(), Botan::TLS::Server_Hello_13::random_signals_downgrade(), Botan::TLS::Server_Hello_12::renegotiation_info(), Botan::TLS::Server_Hello_12::secure_renegotiation(), Botan::TLS::Server_Hello_13::selected_version(), serialize(), Server_Hello(), Botan::TLS::Server_Hello_12::Server_Hello_12(), Botan::TLS::Server_Hello_12::Server_Hello_12(), Botan::TLS::Server_Hello_12_Shim::Server_Hello_12_Shim(), Botan::TLS::Server_Hello_13::Server_Hello_13(), Botan::TLS::Server_Hello_13::Server_Hello_13(), Botan::TLS::Server_Hello_13::Server_Hello_13(), session_id(), Botan::TLS::Server_Hello_12::srtp_profile(), Botan::TLS::Server_Hello_12::supports_certificate_status_message(), Botan::TLS::Server_Hello_12::supports_encrypt_then_mac(), Botan::TLS::Server_Hello_12::supports_extended_master_secret(), and Botan::TLS::Server_Hello_12::supports_session_ticket().
The documentation for this class was generated from the following files:
- src/lib/tls/tls12/tls_messages_12.h
- src/lib/tls/tls12/msg_server_hello_12.cpp
Generated by
 1.16.1