#include <tpm2_ecc.h>
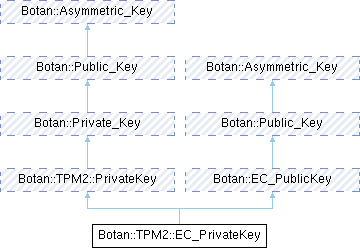
Public Member Functions | |
| virtual std::unique_ptr< PK_Ops::Decryption > | _create_decryption_op (RandomNumberGenerator &rng, const PK_Encryption_Options_Reader &options) const |
| virtual std::unique_ptr< PK_Ops::Encryption > | _create_encryption_op (RandomNumberGenerator &rng, const PK_Encryption_Options_Reader &options) const |
| virtual std::unique_ptr< PK_Ops::KEM_Decryption > | _create_kem_decryption_op (RandomNumberGenerator &rng, const PK_KEM_Options_Reader &options) const |
| virtual std::unique_ptr< PK_Ops::KEM_Encryption > | _create_kem_encryption_op (const PK_KEM_Options_Reader &options) const |
| virtual std::unique_ptr< PK_Ops::Key_Agreement > | _create_key_agreement_op (RandomNumberGenerator &rng, const PK_Key_Agreement_Options_Reader &options) const |
| std::unique_ptr< PK_Ops::Signature > | _create_signature_op (Botan::RandomNumberGenerator &rng, const PK_Signature_Options_Reader &options) const override |
| virtual std::unique_ptr< PK_Ops::Verification > | _create_verification_op (const PK_Signature_Options_Reader &options) const |
| virtual Signature_Format | _default_x509_signature_format () const |
| const EC_AffinePoint & | _public_ec_point () const |
| virtual std::optional< size_t > | _signature_element_size_for_DER_encoding () const |
| std::string | algo_name () const override |
| AlgorithmIdentifier | algorithm_identifier () const override |
| bool | check_key (RandomNumberGenerator &rng, bool strong) const override |
| std::unique_ptr< PK_Ops::Decryption > | create_decryption_op (RandomNumberGenerator &rng, std::string_view params, std::string_view provider) const |
| std::unique_ptr< PK_Ops::Encryption > | create_encryption_op (RandomNumberGenerator &rng, std::string_view params, std::string_view provider) const |
| std::unique_ptr< PK_Ops::KEM_Decryption > | create_kem_decryption_op (RandomNumberGenerator &rng, std::string_view params, std::string_view provider) const |
| std::unique_ptr< PK_Ops::KEM_Encryption > | create_kem_encryption_op (std::string_view params, std::string_view provider) const |
| std::unique_ptr< PK_Ops::Key_Agreement > | create_key_agreement_op (RandomNumberGenerator &rng, std::string_view params, std::string_view provider) const |
| std::unique_ptr< PK_Ops::Signature > | create_signature_op (RandomNumberGenerator &rng, std::string_view params, std::string_view provider) const |
| std::unique_ptr< PK_Ops::Verification > | create_verification_op (std::string_view params, std::string_view provider) const |
| virtual std::unique_ptr< PK_Ops::Verification > | create_x509_verification_op (const AlgorithmIdentifier &signature_algorithm, std::string_view provider) const |
| Signature_Format | default_x509_signature_format () const |
| std::vector< uint8_t > | DER_domain () const |
| const EC_Group & | domain () const |
| EC_Group_Encoding | domain_format () const |
| size_t | estimated_strength () const override |
| std::string | fingerprint_private (std::string_view alg) const |
| std::string | fingerprint_public (std::string_view alg="SHA-256") const |
| std::unique_ptr< Private_Key > | generate_another (Botan::RandomNumberGenerator &) const override |
| const BigInt & | get_int_field (std::string_view field) const override |
| OID | get_oid () const |
| Object & | handles () |
| const Object & | handles () const |
| bool | is_parent () const |
| size_t | key_length () const override |
| size_t | message_part_size () const |
| size_t | message_parts () const |
| virtual OID | object_identifier () const |
| virtual AlgorithmIdentifier | pkcs8_algorithm_identifier () const |
| EC_Point_Format | point_encoding () const |
| secure_vector< uint8_t > | private_key_bits () const override |
| secure_vector< uint8_t > | private_key_info () const |
| const EC_AffinePoint & | public_ec_point () const |
| std::unique_ptr< Public_Key > | public_key () const override |
| std::vector< uint8_t > | public_key_bits () const override |
| secure_vector< uint8_t > | raw_private_key_bits () const override |
| std::vector< uint8_t > | raw_public_key_bits () const override |
| virtual std::optional< uint64_t > | remaining_operations () const |
| Retrieves the number of remaining operations if this is a stateful private key. | |
| const SessionBundle & | sessions () const |
| void | set_parameter_encoding (EC_Group_Encoding enc) |
| void | set_point_encoding (EC_Point_Format enc) |
| virtual bool | stateful_operation () const |
| std::vector< uint8_t > | subject_public_key () const |
| bool | supports_operation (PublicKeyOperation op) const override |
Static Public Member Functions | |
| static std::unique_ptr< PrivateKey > | create_transient_from_template (const std::shared_ptr< Context > &ctx, const SessionBundle &sessions, ESYS_TR parent, const TPMT_PUBLIC &key_template, const TPM2B_SENSITIVE_CREATE &sensitive_data) |
| static std::unique_ptr< TPM2::PrivateKey > | create_unrestricted_transient (const std::shared_ptr< Context > &ctx, const SessionBundle &sessions, std::span< const uint8_t > auth_value, const TPM2::PrivateKey &parent, const EC_Group &group) |
| static std::unique_ptr< PrivateKey > | load_persistent (const std::shared_ptr< Context > &ctx, TPM2_HANDLE persistent_object_handle, std::span< const uint8_t > auth_value, const SessionBundle &sessions) |
| static std::unique_ptr< PrivateKey > | load_transient (const std::shared_ptr< Context > &ctx, std::span< const uint8_t > auth_value, const TPM2::PrivateKey &parent, std::span< const uint8_t > public_blob, std::span< const uint8_t > private_blob, const SessionBundle &sessions) |
Protected Member Functions | |
| EC_PrivateKey (Object handle, SessionBundle sessions, const std::pair< EC_Group, EC_AffinePoint > &public_key, std::span< const uint8_t > private_blob={}) | |
| EC_PrivateKey (Object handle, SessionBundle sessions, const TPM2B_PUBLIC *public_blob, std::span< const uint8_t > private_blob={}) | |
Static Protected Member Functions | |
| static const AlgorithmIdentifier & | assert_algorithm_identifier (const AlgorithmIdentifier &alg_id, std::string_view alg_name) |
| static std::unique_ptr< PrivateKey > | create (Object handles, const SessionBundle &sessions, const TPM2B_PUBLIC *public_info, std::span< const uint8_t > private_blob) |
Protected Attributes | |
| EC_Group_Encoding | m_domain_encoding = EC_Group_Encoding::NamedCurve |
| EC_Point_Format | m_point_encoding = EC_Point_Format::Uncompressed |
| std::shared_ptr< const EC_PublicKey_Data > | m_public_key |
Friends | |
| class | TPM2::PrivateKey |
Detailed Description
Definition at line 50 of file tpm2_ecc.h.
Constructor & Destructor Documentation
◆ EC_PrivateKey() [1/2]
|
protected |
Definition at line 32 of file tpm2_ecc.cpp.
References EC_PrivateKey(), and Botan::TPM2::PrivateKey::sessions().
Referenced by EC_PrivateKey(), and TPM2::PrivateKey.
◆ EC_PrivateKey() [2/2]
|
protected |
Definition at line 38 of file tpm2_ecc.cpp.
References Botan::EC_PublicKey::EC_PublicKey(), public_key(), Botan::TPM2::PrivateKey::sessions(), and TPM2::PrivateKey.
Member Function Documentation
◆ _create_decryption_op()
|
virtualinherited |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return a decryption operation for this key/options or throw
- Parameters
-
Random Number Generators a random number generator. The PK_Op may maintain a reference to the RNG and use it many times. The rng must outlive any operations which reference it. options which specify parameters of the encryption beyond those implicit to the key itself
Reimplemented in Botan::ElGamal_PrivateKey, Botan::RSA_PrivateKey, Botan::SM2_PrivateKey, and Botan::TPM2::RSA_PrivateKey.
Definition at line 130 of file pk_keys.cpp.
References Botan::Asymmetric_Key::algo_name(), BOTAN_UNUSED, and Botan::fmt().
Referenced by create_decryption_op(), and Botan::PK_Decryptor_EME::PK_Decryptor_EME().
◆ _create_encryption_op()
|
virtualinherited |
This is an internal library function exposed on key types. In almost all cases applications should use wrappers in pubkey.h
Return an encryption operation for this key/options or throw
- Parameters
-
Random Number Generators a random number generator. The PK_Op may maintain a reference to the RNG and use it many times. The rng must outlive any operations which reference it. options which specify parameters of the encryption beyond those implicit to the public key itself
Reimplemented in Botan::ElGamal_PublicKey, Botan::RSA_PublicKey, Botan::SM2_PublicKey, and Botan::TPM2::RSA_PublicKey.
Definition at line 107 of file pk_keys.cpp.
References Botan::Asymmetric_Key::algo_name(), BOTAN_UNUSED, and Botan::fmt().
Referenced by create_encryption_op(), and Botan::PK_Encryptor_EME::PK_Encryptor_EME().
◆ _create_kem_decryption_op()
|
virtualinherited |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return a KEM decryption operation for this key/options or throw
- Parameters
-
Random Number Generators a random number generator. The PK_Op may maintain a reference to the RNG and use it many times. The rng must outlive any operations which reference it. options which specify parameters of the KEM beyond those implicit to the key itself
Reimplemented in Botan::Classic_McEliece_PrivateKey, Botan::FrodoKEM_PrivateKey, Botan::KEX_to_KEM_Adapter_PrivateKey, Botan::Kyber_PrivateKey, Botan::McEliece_PrivateKey, Botan::RSA_PrivateKey, and Botan::TLS::Hybrid_KEM_PrivateKey.
Definition at line 136 of file pk_keys.cpp.
References Botan::Asymmetric_Key::algo_name(), BOTAN_UNUSED, and Botan::fmt().
Referenced by create_kem_decryption_op(), and Botan::PK_KEM_Decryptor::PK_KEM_Decryptor().
◆ _create_kem_encryption_op()
|
virtualinherited |
This is an internal library function exposed on key types. In almost all cases applications should use wrappers in pubkey.h
Return a KEM encryption operation for this key/options or throw
- Parameters
-
options which specify parameters of the KEM beyond those implicit to the public key itself
Reimplemented in Botan::Classic_McEliece_PublicKey, Botan::FrodoKEM_PublicKey, Botan::KEX_to_KEM_Adapter_PublicKey, Botan::Kyber_PublicKey, Botan::McEliece_PublicKey, Botan::RSA_PublicKey, and Botan::TLS::Hybrid_KEM_PublicKey.
Definition at line 113 of file pk_keys.cpp.
References Botan::Asymmetric_Key::algo_name(), BOTAN_UNUSED, and Botan::fmt().
Referenced by create_kem_encryption_op(), and Botan::PK_KEM_Encryptor::PK_KEM_Encryptor().
◆ _create_key_agreement_op()
|
virtualinherited |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return a key agreement operation for this key/options or throw
- Parameters
-
Random Number Generators a random number generator. The PK_Op may maintain a reference to the RNG and use it many times. The rng must outlive any operations which reference it. options which specify parameters of the key agreement beyond those implicit to the key itself
Reimplemented in Botan::DH_PrivateKey, Botan::ECDH_PrivateKey, Botan::X25519_PrivateKey, and Botan::X448_PrivateKey.
Definition at line 148 of file pk_keys.cpp.
References Botan::Asymmetric_Key::algo_name(), BOTAN_UNUSED, and Botan::fmt().
Referenced by create_key_agreement_op(), and Botan::PK_Key_Agreement::PK_Key_Agreement().
◆ _create_signature_op()
|
overridevirtual |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return a signature operation for this key/params or throw
- Parameters
-
Random Number Generators a random number generator. The PK_Op may maintain a reference to the RNG and use it many times. The rng must outlive any operations which reference it. options allow controlling behavior
Reimplemented from Botan::Private_Key.
Definition at line 259 of file tpm2_ecc.cpp.
References algo_name(), BOTAN_UNUSED, Botan::TPM2::PrivateKey::handles(), Botan::require_hardware_provider(), and Botan::TPM2::PrivateKey::sessions().
◆ _create_verification_op()
|
virtualinherited |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return a verification operation for this key/params or throw
- Parameters
-
options which specify parameters of the signature beyond those implicit to the public key itself
Reimplemented in Botan::Dilithium_PublicKey, Botan::DSA_PublicKey, Botan::ECDSA_PublicKey, Botan::ECGDSA_PublicKey, Botan::ECKCDSA_PublicKey, Botan::Ed25519_PublicKey, Botan::Ed448_PublicKey, Botan::GOST_3410_PublicKey, Botan::HSS_LMS_PublicKey, Botan::RSA_PublicKey, Botan::SM2_PublicKey, Botan::SphincsPlus_PublicKey, Botan::TPM2::EC_PublicKey, Botan::TPM2::RSA_PublicKey, and Botan::XMSS_PublicKey.
Definition at line 119 of file pk_keys.cpp.
References Botan::Asymmetric_Key::algo_name(), BOTAN_UNUSED, and Botan::fmt().
Referenced by create_verification_op(), and Botan::PK_Verifier::PK_Verifier().
◆ _default_x509_signature_format()
|
virtualinherited |
Reimplemented in Botan::GOST_3410_PublicKey.
Definition at line 32 of file pk_keys.cpp.
References _signature_element_size_for_DER_encoding(), Botan::DerSequence, and Botan::Standard.
Referenced by Botan::X509_Object::choose_sig_format(), Botan::Public_Key::default_x509_signature_format(), and Botan::PK_Verifier::PK_Verifier().
◆ _public_ec_point()
|
inlineinherited |
Definition at line 115 of file ecc_key.h.
References public_ec_point().
◆ _signature_element_size_for_DER_encoding()
|
inlinevirtualinherited |
Certain signatures schemes such as ECDSA have more than one element, and certain unfortunate protocols decided the thing to do was not concatenate them as normally done, but instead DER encode each of the elements as independent values.
If this returns a value x then the signature is checked to be exactly 2*x bytes and split in half for DER encoding.
Reimplemented in Botan::DSA_PublicKey, Botan::ECDSA_PublicKey, Botan::ECGDSA_PublicKey, Botan::ECKCDSA_PublicKey, Botan::GOST_3410_PublicKey, and Botan::SM2_PublicKey.
Definition at line 148 of file pk_keys.h.
Referenced by _default_x509_signature_format(), Botan::Public_Key::message_part_size(), Botan::Public_Key::message_parts(), Botan::PK_Signer::PK_Signer(), Botan::PK_Verifier::PK_Verifier(), and Botan::PK_Verifier::PK_Verifier().
◆ algo_name()
|
inlineoverridevirtual |
Get the name of the underlying public key scheme.
- Returns
- name of the public key scheme
Implements Botan::Asymmetric_Key.
Definition at line 53 of file tpm2_ecc.h.
Referenced by _create_signature_op().
◆ algorithm_identifier()
|
overridevirtualinherited |
Return the X.509 AlgorithmIdentifier for this key
Implements Botan::Public_Key.
Reimplemented in Botan::GOST_3410_PublicKey.
Definition at line 98 of file ecc_key.cpp.
References DER_domain(), and Botan::Asymmetric_Key::object_identifier().
Referenced by ~EC_PublicKey().
◆ assert_algorithm_identifier()
|
staticprotectedinherited |
Definition at line 48 of file ecc_key.cpp.
References Botan::fmt(), Botan::OID::from_string(), and Botan::AlgorithmIdentifier::oid().
Referenced by Botan::ECDSA_PrivateKey::ECDSA_PrivateKey(), Botan::ECDSA_PublicKey::ECDSA_PublicKey(), Botan::ECGDSA_PrivateKey::ECGDSA_PrivateKey(), Botan::ECGDSA_PublicKey::ECGDSA_PublicKey(), Botan::ECKCDSA_PrivateKey::ECKCDSA_PrivateKey(), and Botan::ECKCDSA_PublicKey::ECKCDSA_PublicKey().
◆ check_key()
|
overridevirtualinherited |
Test the key values for consistency.
Note this function is always "best effort"; for many algorithms it is not computationally possible to ensure the key is correctly formed in all respects. There is always the possibility a malformed key will be accepted; this is especially the case for public keys.
- Parameters
-
Random Number Generators rng to use for randomized testing (may be ignored) strong whether to perform strong and lengthy version of the test, however for many algorithms this has no effect
- Returns
- true if the tests passed
Implements Botan::Asymmetric_Key.
Reimplemented in Botan::ECDSA_PrivateKey, Botan::ECGDSA_PrivateKey, Botan::ECKCDSA_PrivateKey, and Botan::SM2_PrivateKey.
Definition at line 93 of file ecc_key.cpp.
References domain(), Botan::EC_AffinePoint::is_identity(), public_ec_point(), and Botan::EC_Group::verify_group().
Referenced by Botan::EC_PrivateKey::check_key(), and ~EC_PublicKey().
◆ create()
|
staticprotectedinherited |
Definition at line 299 of file tpm2_key.cpp.
References Botan::fmt(), handles(), and sessions().
Referenced by create_transient_from_template(), load_persistent(), and load_transient().
◆ create_decryption_op()
|
inherited |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return an decryption operation for this key/params or throw
- Parameters
-
Random Number Generators a random number generator. The PK_Op may maintain a reference to the RNG and use it many times. The rng must outlive any operations which reference it. params additional parameters provider the provider to use
Definition at line 185 of file pk_keys.cpp.
References _create_decryption_op(), Botan::Asymmetric_Key::algo_name(), Botan::parse_legacy_enc_options(), Botan::PK_Options_Reader_Access::read(), Botan::PK_Options_Reader_Access::throw_if_unexamined(), and Botan::PK_Encryption_Options::with_provider().
◆ create_encryption_op()
|
inherited |
This is an internal library function exposed on key types. In almost all cases applications should use wrappers in pubkey.h
Return an encryption operation for this key/params or throw
- Parameters
-
Random Number Generators a random number generator. The PK_Op may maintain a reference to the RNG and use it many times. The rng must outlive any operations which reference it. params additional parameters provider the provider to use
Definition at line 175 of file pk_keys.cpp.
References _create_encryption_op(), Botan::Asymmetric_Key::algo_name(), Botan::parse_legacy_enc_options(), Botan::PK_Options_Reader_Access::read(), Botan::PK_Options_Reader_Access::throw_if_unexamined(), and Botan::PK_Encryption_Options::with_provider().
◆ create_kem_decryption_op()
|
inherited |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return a KEM decryption operation for this key/params or throw
- Parameters
-
Random Number Generators a random number generator. The PK_Op may maintain a reference to the RNG and use it many times. The rng must outlive any operations which reference it. params additional parameters provider the provider to use
Definition at line 204 of file pk_keys.cpp.
References _create_kem_decryption_op(), Botan::Asymmetric_Key::algo_name(), Botan::parse_legacy_kem_options(), Botan::PK_Options_Reader_Access::read(), Botan::PK_Options_Reader_Access::throw_if_unexamined(), and Botan::PK_KEM_Options::with_provider().
◆ create_kem_encryption_op()
|
inherited |
This is an internal library function exposed on key types. In almost all cases applications should use wrappers in pubkey.h
Return a KEM encryption operation for this key/params or throw
- Parameters
-
params additional parameters provider the provider to use
Definition at line 195 of file pk_keys.cpp.
References _create_kem_encryption_op(), Botan::Asymmetric_Key::algo_name(), Botan::parse_legacy_kem_options(), Botan::PK_Options_Reader_Access::read(), Botan::PK_Options_Reader_Access::throw_if_unexamined(), and Botan::PK_KEM_Options::with_provider().
◆ create_key_agreement_op()
|
inherited |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return a key agreement operation for this key/params or throw
- Parameters
-
Random Number Generators a random number generator. The PK_Op may maintain a reference to the RNG and use it many times. The rng must outlive any operations which reference it. params additional parameters provider the provider to use
Definition at line 214 of file pk_keys.cpp.
References _create_key_agreement_op(), Botan::Asymmetric_Key::algo_name(), Botan::parse_legacy_ka_options(), Botan::PK_Options_Reader_Access::read(), Botan::PK_Options_Reader_Access::throw_if_unexamined(), and Botan::PK_Key_Agreement_Options::with_provider().
◆ create_signature_op()
|
inherited |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return a signature operation for this key/params or throw
- Parameters
-
Random Number Generators a random number generator. The PK_Op may maintain a reference to the RNG and use it many times. The rng must outlive any operations which reference it. params additional parameters provider the provider to use
Definition at line 165 of file pk_keys.cpp.
References _create_signature_op(), Botan::Asymmetric_Key::algo_name(), Botan::PK_Options_Reader_Access::for_signing(), Botan::parse_legacy_sig_options(), Botan::PK_Options_Reader_Access::throw_if_unexamined(), and Botan::PK_Signature_Options::with_provider().
◆ create_transient_from_template()
|
staticinherited |
This is a wrapper around Esys_CreateLoaded creating a transient key from a given key_template with sensitive_data. It gives maximal flexibility to the caller to create a key with their own TSS2 template configuration.
Please use this if you know what you are doing, only! Most users should use the more convenient create_transient() methods of the derived classes.
- Parameters
-
ctx The TPM context to use sessions The session bundle to use in Esys_CreateLoaded(). parent The handle of the parent object to create the new key under (this may reference a "Primary Seed" to create a "Primary Key", a "Storage Parent" to create an "Ordinary Key", or a "Derivation Parent" to create a "Derived Key"). key_template The template data to use for the key creation. It will be passed to Tss2_MU_TPMT_PUBLIC_Marshal() and Esys_CreateLoaded(). sensitive_data The sensitive data (e.g. with the desired auth value) to use for the key creation.
Definition at line 224 of file tpm2_key.cpp.
References Botan::TPM2::as_span(), BOTAN_ASSERT_NOMSG, BOTAN_ASSERT_NONNULL, Botan::TPM2::check_rc(), create(), Botan::TPM2::Object::has_transient_handle(), Botan::out_ptr(), Botan::TPM2::out_transient_handle(), and sessions().
Referenced by Botan::TPM2::EC_PrivateKey::create_unrestricted_transient(), and Botan::TPM2::RSA_PrivateKey::create_unrestricted_transient().
◆ create_unrestricted_transient()
|
static |
Create a transient EC key with the given group EC Group, under the given parent key, with the given auth_value. This key may only be used for ECDSA signatures.
- Parameters
-
ctx The TPM context to use sessions The session bundle to use in the creation of the key auth_value The auth value to use for the key parent The parent key to create the new key under group The desired EC Group
Definition at line 65 of file tpm2_ecc.cpp.
References BOTAN_ARG_CHECK, Botan::TPM2::copy_into(), Botan::TPM2::PrivateKey::create_transient_from_template(), Botan::EC_Group::get_curve_oid(), Botan::TPM2::get_tpm2_curve_id(), Botan::TPM2::PrivateKey::handles(), Botan::TPM2::init_empty(), Botan::TPM2::PrivateKey::is_parent(), Botan::TPM2::ObjectAttributes::render(), Botan::TPM2::PrivateKey::sessions(), and Botan::TPM2::Object::transient_handle().
◆ create_verification_op()
|
inherited |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return a verification operation for this key/params or throw
- Parameters
-
params additional parameters provider the provider to use
Definition at line 156 of file pk_keys.cpp.
References _create_verification_op(), Botan::Asymmetric_Key::algo_name(), Botan::PK_Options_Reader_Access::for_verification(), Botan::parse_legacy_sig_options(), Botan::PK_Options_Reader_Access::throw_if_unexamined(), and Botan::PK_Signature_Options::with_provider().
◆ create_x509_verification_op()
|
virtualinherited |
This is an internal library function exposed on key types. In all cases applications should use wrappers in pubkey.h
Return a verification operation for this combination of key and signature algorithm or throw.
- Parameters
-
signature_algorithm is the X.509 algorithm identifier encoding the padding scheme and hash hash function used in the signature if applicable. provider the provider to use
Reimplemented in Botan::Dilithium_PublicKey, Botan::DSA_PublicKey, Botan::ECDSA_PublicKey, Botan::ECGDSA_PublicKey, Botan::ECKCDSA_PublicKey, Botan::Ed25519_PublicKey, Botan::Ed448_PublicKey, Botan::GOST_3410_PublicKey, Botan::HSS_LMS_PublicKey, Botan::RSA_PublicKey, Botan::SphincsPlus_PublicKey, and Botan::XMSS_PublicKey.
Definition at line 125 of file pk_keys.cpp.
References Botan::Asymmetric_Key::algo_name(), and Botan::fmt().
Referenced by Botan::PK_Verifier::PK_Verifier().
◆ default_x509_signature_format()
|
inlineinherited |
Definition at line 245 of file pk_keys.h.
References Botan::Asymmetric_Key::_default_x509_signature_format(), and default_x509_signature_format().
Referenced by default_x509_signature_format().
◆ DER_domain()
|
inherited |
Return the DER encoding of this keys domain in whatever format is preset for this particular key
Definition at line 110 of file ecc_key.cpp.
References Botan::EC_Group::DER_encode(), domain(), and domain_format().
Referenced by algorithm_identifier(), and ~EC_PublicKey().
◆ domain()
|
inherited |
Get the domain parameters of this key.
- Exceptions
-
Invalid_State is thrown if the domain parameters of this point are not set
- Returns
- the domain parameters of this key
Definition at line 76 of file ecc_key.cpp.
References BOTAN_STATE_CHECK, and m_public_key.
Referenced by Botan::ECDSA_PublicKey::_signature_element_size_for_DER_encoding(), Botan::ECGDSA_PublicKey::_signature_element_size_for_DER_encoding(), Botan::ECKCDSA_PublicKey::_signature_element_size_for_DER_encoding(), Botan::GOST_3410_PublicKey::_signature_element_size_for_DER_encoding(), Botan::SM2_PublicKey::_signature_element_size_for_DER_encoding(), Botan::GOST_3410_PublicKey::algo_name(), Botan::GOST_3410_PublicKey::algorithm_identifier(), botan_ec_privkey_get_group(), botan_ec_pubkey_get_group(), botan_pubkey_ecc_key_used_explicit_encoding(), botan_pubkey_sm2_compute_za(), check_key(), Botan::SM2_PrivateKey::check_key(), DER_domain(), Botan::EC_PrivateKey::EC_PrivateKey(), Botan::EC_PrivateKey::EC_PrivateKey(), Botan::EC_PrivateKey::EC_PrivateKey(), Botan::EC_PrivateKey::EC_PrivateKey(), EC_PublicKey(), EC_PublicKey(), Botan::ECDH_PublicKey::generate_another(), Botan::ECDSA_PublicKey::generate_another(), Botan::ECGDSA_PublicKey::generate_another(), Botan::ECKCDSA_PublicKey::generate_another(), Botan::GOST_3410_PublicKey::generate_another(), Botan::SM2_PublicKey::generate_another(), get_int_field(), Botan::GOST_3410_PrivateKey::GOST_3410_PrivateKey(), Botan::GOST_3410_PrivateKey::GOST_3410_PrivateKey(), Botan::GOST_3410_PrivateKey::GOST_3410_PrivateKey(), key_length(), Botan::ECDH_PrivateKey::public_key(), Botan::ECDSA_PrivateKey::public_key(), Botan::ECGDSA_PrivateKey::public_key(), Botan::ECKCDSA_PrivateKey::public_key(), Botan::GOST_3410_PrivateKey::public_key(), Botan::SM2_PrivateKey::public_key(), Botan::TPM2::EC_PrivateKey::public_key(), Botan::ECDSA_PublicKey::recovery_param(), set_parameter_encoding(), Botan::SM2_PrivateKey::SM2_PrivateKey(), Botan::SM2_PrivateKey::SM2_PrivateKey(), Botan::SM2_PrivateKey::SM2_PrivateKey(), and ~EC_PublicKey().
◆ domain_format()
|
inlineinherited |
Get the domain parameter encoding to be used when encoding this key.
- Returns
- the encoding to use
Definition at line 96 of file ecc_key.h.
References domain_format(), and m_domain_encoding.
Referenced by DER_domain(), and domain_format().
◆ estimated_strength()
|
overridevirtualinherited |
Return the estimated strength of the underlying key against the best currently known attack. Note that this ignores anything but pure attacks against the key itself and do not take into account padding schemes, usage mistakes, etc which might reduce the strength. However it does suffice to provide an upper bound.
- Returns
- estimated strength in bits
Implements Botan::Asymmetric_Key.
Definition at line 32 of file ecc_key.cpp.
References Botan::ecp_work_factor(), and key_length().
◆ fingerprint_private()
|
inherited |
- Returns
- Hash of the algorithm specific private key encoding
- Warning
- This hashes private_key_bits(), which does not include the algorithm identifier; keys of different algorithms with identical raw encodings (such as an Ed25519 and an X25519 key built from the same 32 bytes) share a fingerprint.
Definition at line 103 of file pk_keys.cpp.
References Botan::create_hex_fingerprint(), and private_key_bits().
Referenced by Botan::Certificate_Store_In_SQL::find_certs_for_key(), Botan::Certificate_Store_In_SQL::insert_key(), and Botan::Certificate_Store_In_SQL::remove_key().
◆ fingerprint_public()
|
inherited |
- Returns
- Hash of the subject public key
Definition at line 96 of file pk_keys.cpp.
References Botan::create_hex_fingerprint(), and subject_public_key().
Referenced by public_key_bits().
◆ generate_another()
|
inlineoverridevirtual |
Generate another (cryptographically independent) key pair using the same algorithm parameters as this key. This is most useful for algorithms that support PublicKeyOperation::KeyAgreement to generate a fitting ephemeral key pair. For other key types it might throw Not_Implemented.
Implements Botan::Asymmetric_Key.
Definition at line 62 of file tpm2_ecc.h.
◆ get_int_field()
|
overridevirtualinherited |
Access an algorithm specific field
If the field is not known for this algorithm, an Invalid_Argument is thrown. The interpretation of the result requires knowledge of which algorithm is involved. For instance for RSA "p" represents one of the secret primes, while for DSA "p" is the public prime.
Some algorithms may not implement this method at all.
This is primarily used to implement the FFI botan_pubkey_get_field and botan_privkey_get_field functions.
TODO(Botan4) Change this to return by value
Reimplemented from Botan::Asymmetric_Key.
Definition at line 252 of file ecc_key.cpp.
References domain(), Botan::fmt(), Botan::EC_Group::get_a(), Botan::EC_Group::get_b(), Botan::EC_Group::get_cofactor(), Botan::EC_Group::get_g_x(), Botan::EC_Group::get_g_y(), Botan::Asymmetric_Key::get_int_field(), Botan::EC_Group::get_order(), and Botan::EC_Group::get_p().
Referenced by Botan::EC_PrivateKey::get_int_field().
◆ get_oid()
|
inlineinherited |
Deprecated version of object_identifier
Definition at line 172 of file pk_keys.h.
References get_oid(), and Botan::Asymmetric_Key::object_identifier().
Referenced by get_oid().
◆ handles() [1/2]
|
inlineinherited |
Definition at line 220 of file tpm2_key.h.
Referenced by Botan::TPM2::RSA_PrivateKey::_create_decryption_op(), Botan::TPM2::EC_PrivateKey::_create_signature_op(), Botan::TPM2::RSA_PrivateKey::_create_signature_op(), Botan::TPM2::Session::authenticated_session(), create(), Botan::TPM2::EC_PrivateKey::create_unrestricted_transient(), Botan::TPM2::RSA_PrivateKey::create_unrestricted_transient(), load_transient(), and Botan::TPM2::Context::persist().
◆ handles() [2/2]
|
inlineinherited |
Definition at line 222 of file tpm2_key.h.
◆ is_parent()
|
inherited |
Definition at line 291 of file tpm2_key.cpp.
Referenced by Botan::TPM2::EC_PrivateKey::create_unrestricted_transient(), and Botan::TPM2::RSA_PrivateKey::create_unrestricted_transient().
◆ key_length()
|
overridevirtualinherited |
Return an integer value best approximating the length of the primary security parameter. For example for RSA this will be the size of the modulus, for ECDSA the size of the ECC group, and for McEliece the size of the code will be returned.
Implements Botan::Public_Key.
Definition at line 28 of file ecc_key.cpp.
References domain(), and Botan::EC_Group::get_p_bits().
Referenced by estimated_strength().
◆ load_persistent()
|
staticinherited |
Load a private key that resides in the TPM's persistent storage.
- Parameters
-
ctx The TPM context to use persistent_object_handle The handle of the persistent object to load auth_value The auth value required to use the key sessions The session bundle to use for the key's operations
Definition at line 184 of file tpm2_key.cpp.
References create(), and sessions().
Referenced by Botan::TPM2::Context::storage_root_key().
◆ load_transient()
|
staticinherited |
Load a private key from the public and private blobs obtained by a TPM key creation.
Transient keys don't reside inside the TPM but must be loaded by the application as required. Once this object is destructed, the transient memory on the TPM is cleared.
- Parameters
-
ctx The TPM context to use auth_value The auth value required to use the key parent The parent key the key was originally created under public_blob The public blob of the key to load private_blob The private blob of the key to load sessions The session bundle to use for loading
Definition at line 194 of file tpm2_key.cpp.
References BOTAN_ASSERT_NONNULL, Botan::TPM2::check_rc(), Botan::TPM2::copy_into(), create(), handles(), Botan::TPM2::out_transient_handle(), sessions(), and Botan::TPM2::Object::transient_handle().
◆ message_part_size()
|
inlineinherited |
Returns how large each of the message parts referred to by message_parts() is
This function is public but applications should have few reasons to ever call this.
- Returns
- size of the message parts in bits
Definition at line 236 of file pk_keys.h.
References Botan::Asymmetric_Key::_signature_element_size_for_DER_encoding(), and message_part_size().
Referenced by message_part_size().
◆ message_parts()
|
inlineinherited |
Returns more than 1 if the output of this algorithm (ciphertext, signature) should be treated as more than one value. This is used for algorithms like DSA and ECDSA, where the (r,s) output pair can be encoded as either a plain binary list or a TLV tagged DER encoding depending on the protocol.
This function is public but applications should have few reasons to ever call this.
- Returns
- number of message parts
Definition at line 223 of file pk_keys.h.
References Botan::Asymmetric_Key::_signature_element_size_for_DER_encoding(), and message_parts().
Referenced by message_parts().
◆ object_identifier()
|
virtualinherited |
Get the OID of the underlying public key scheme.
- Returns
- OID of the public key scheme
Reimplemented in Botan::Classic_McEliece_PublicKey, Botan::Dilithium_PublicKey, Botan::FrodoKEM_PublicKey, Botan::HSS_LMS_PublicKey, Botan::Kyber_PublicKey, and Botan::SphincsPlus_PublicKey.
Definition at line 24 of file pk_keys.cpp.
References algo_name(), Botan::fmt(), and Botan::OID::from_string().
Referenced by Botan::DH_PublicKey::algorithm_identifier(), Botan::DSA_PublicKey::algorithm_identifier(), Botan::EC_PublicKey::algorithm_identifier(), Botan::Ed25519_PublicKey::algorithm_identifier(), Botan::Ed448_PublicKey::algorithm_identifier(), Botan::ElGamal_PublicKey::algorithm_identifier(), Botan::GOST_3410_PublicKey::algorithm_identifier(), Botan::McEliece_PublicKey::algorithm_identifier(), Botan::RSA_PublicKey::algorithm_identifier(), Botan::TPM_PrivateKey::algorithm_identifier(), Botan::X25519_PublicKey::algorithm_identifier(), Botan::X448_PublicKey::algorithm_identifier(), Botan::XMSS_PublicKey::algorithm_identifier(), estimated_strength(), and Botan::Public_Key::get_oid().
◆ pkcs8_algorithm_identifier()
|
inlinevirtualinherited |
Return the PKCS #8 AlgorithmIdentifier for this key
- Note
- normally this is the same as the public key identifier, but a few oddball algorithms use a different value
Reimplemented in Botan::GOST_3410_PrivateKey, and Botan::HSS_LMS_PrivateKey.
Definition at line 390 of file pk_keys.h.
References Botan::Public_Key::algorithm_identifier().
Referenced by private_key_info().
◆ point_encoding()
|
inlineinherited |
Get the point encoding method to be used when encoding this key.
- Returns
- the encoding to use
Definition at line 102 of file ecc_key.h.
References m_point_encoding.
Referenced by raw_public_key_bits().
◆ private_key_bits()
|
inlineoverridevirtualinherited |
- Exceptions
-
Not_Implemented keys hosted in a TPM2 cannot be exported
Implements Botan::Private_Key.
Definition at line 205 of file tpm2_key.h.
◆ private_key_info()
|
inherited |
Return PKCS #8 private key encoding for this key object
Definition at line 77 of file pk_keys.cpp.
References Botan::DER_Encoder::encode(), Botan::DER_Encoder::end_cons(), Botan::DER_Encoder::get_contents(), Botan::OctetString, pkcs8_algorithm_identifier(), private_key_bits(), and Botan::DER_Encoder::start_sequence().
Referenced by Botan::PKCS8::BER_encode(), Botan::PKCS8::BER_encode_encrypted_pbkdf_iter(), Botan::PKCS8::BER_encode_encrypted_pbkdf_msec(), Botan::PKCS8::PEM_encode(), and public_key().
◆ public_ec_point()
|
inherited |
Return the public point of this key
Definition at line 88 of file ecc_key.cpp.
References BOTAN_STATE_CHECK, and m_public_key.
Referenced by _public_ec_point(), botan_pubkey_sm2_compute_za(), Botan::EC_PrivateKey::check_key(), check_key(), Botan::ECDH_PrivateKey::public_key(), Botan::ECDSA_PrivateKey::public_key(), Botan::ECGDSA_PrivateKey::public_key(), Botan::ECKCDSA_PrivateKey::public_key(), Botan::GOST_3410_PrivateKey::public_key(), Botan::SM2_PrivateKey::public_key(), Botan::TPM2::EC_PrivateKey::public_key(), Botan::GOST_3410_PublicKey::public_key_bits(), Botan::ECDH_PublicKey::public_value(), raw_public_key_bits(), and Botan::ECDSA_PublicKey::recovery_param().
◆ public_key()
|
overridevirtual |
Allocate a new object for the public key associated with this private key.
- Returns
- public key
Implements Botan::Private_Key.
Definition at line 45 of file tpm2_ecc.cpp.
References Botan::EC_PublicKey::domain(), and Botan::EC_PublicKey::public_ec_point().
Referenced by EC_PrivateKey().
◆ public_key_bits()
|
overridevirtual |
- Returns
- the public key encoding in ordinary point encoding
Implements Botan::Public_Key.
Definition at line 57 of file tpm2_ecc.cpp.
References Botan::EC_PublicKey::raw_public_key_bits().
◆ raw_private_key_bits()
|
overridevirtualinherited |
- Returns
- the encrypted private key blob, if the key is transient
- Exceptions
-
Invalid_State if the key is persistent
Reimplemented from Botan::Private_Key.
Definition at line 281 of file tpm2_key.cpp.
References BOTAN_ASSERT_NOMSG, BOTAN_STATE_CHECK, and Botan::lock().
◆ raw_public_key_bits()
|
overridevirtual |
- Returns
- the public key encoding in TPM2B_PUBLIC format
Implements Botan::Public_Key.
Definition at line 61 of file tpm2_ecc.cpp.
References Botan::TPM2::PrivateKey::raw_public_key_bits().
◆ remaining_operations()
|
inlinevirtualinherited |
Retrieves the number of remaining operations if this is a stateful private key.
- Returns
- the number of remaining operations or std::nullopt if not applicable.
Reimplemented in Botan::HSS_LMS_PrivateKey, and Botan::XMSS_PrivateKey.
Definition at line 403 of file pk_keys.h.
◆ sessions()
|
inlineinherited |
Definition at line 224 of file tpm2_key.h.
Referenced by Botan::TPM2::RSA_PrivateKey::_create_decryption_op(), Botan::TPM2::EC_PrivateKey::_create_signature_op(), Botan::TPM2::RSA_PrivateKey::_create_signature_op(), create(), create_transient_from_template(), Botan::TPM2::EC_PrivateKey::create_unrestricted_transient(), Botan::TPM2::RSA_PrivateKey::create_unrestricted_transient(), Botan::TPM2::EC_PrivateKey::EC_PrivateKey(), Botan::TPM2::EC_PrivateKey::EC_PrivateKey(), load_persistent(), load_transient(), PrivateKey(), Botan::TPM2::EC_PrivateKey::TPM2::PrivateKey, and Botan::TPM2::RSA_PrivateKey::TPM2::PrivateKey.
◆ set_parameter_encoding()
|
inherited |
Set the domain parameter encoding to be used when encoding this key.
- Parameters
-
enc the encoding to use
This function is deprecated; in a future major release only namedCurve encoding of domain parameters will be allowed.
Definition at line 122 of file ecc_key.cpp.
References domain(), m_domain_encoding, and Botan::NamedCurve.
Referenced by ~EC_PublicKey().
◆ set_point_encoding()
|
inherited |
Set the point encoding method to be used when encoding this key.
- Parameters
-
enc the encoding to use
Definition at line 114 of file ecc_key.cpp.
References Botan::Compressed, Botan::Hybrid, m_point_encoding, and Botan::Uncompressed.
Referenced by ~EC_PublicKey().
◆ stateful_operation()
|
inlinevirtualinherited |
Indicates if this key is stateful, ie that performing a private key operation requires updating the key storage.
Reimplemented in Botan::HSS_LMS_PrivateKey, and Botan::XMSS_PrivateKey.
Definition at line 396 of file pk_keys.h.
◆ subject_public_key()
|
inherited |
Return the SubjectPublicKeyInfo encoding of this public key
This is the subjectPublicKey field plus the algorithm-specific parameters
Definition at line 65 of file pk_keys.cpp.
References algorithm_identifier(), Botan::DER_Encoder::encode(), Botan::DER_Encoder::encode_octet_aligned_bitstring(), Botan::DER_Encoder::end_cons(), public_key_bits(), and Botan::DER_Encoder::start_sequence().
Referenced by Botan::X509::BER_encode(), Botan::PKCS10_Request::create(), fingerprint_public(), Botan::X509::PEM_encode(), and public_key_bits().
◆ supports_operation()
|
inlineoverridevirtual |
Return true if this key could be used for the specified type of operation.
Implements Botan::Asymmetric_Key.
Definition at line 97 of file tpm2_ecc.h.
References Botan::Signature.
Friends And Related Symbol Documentation
◆ TPM2::PrivateKey
|
friend |
Definition at line 103 of file tpm2_ecc.h.
References EC_PrivateKey(), and Botan::TPM2::PrivateKey::sessions().
Referenced by EC_PrivateKey().
Member Data Documentation
◆ m_domain_encoding
|
protectedinherited |
Definition at line 149 of file ecc_key.h.
Referenced by domain_format(), Botan::EC_PrivateKey::EC_PrivateKey(), Botan::EC_PrivateKey::EC_PrivateKey(), Botan::EC_PrivateKey::EC_PrivateKey(), Botan::EC_PrivateKey::EC_PrivateKey(), EC_PublicKey(), EC_PublicKey(), and set_parameter_encoding().
◆ m_point_encoding
|
protectedinherited |
Definition at line 150 of file ecc_key.h.
Referenced by point_encoding(), and set_point_encoding().
◆ m_public_key
|
protectedinherited |
Definition at line 148 of file ecc_key.h.
Referenced by domain(), Botan::EC_PrivateKey::EC_PrivateKey(), Botan::EC_PrivateKey::EC_PrivateKey(), Botan::EC_PrivateKey::EC_PrivateKey(), Botan::EC_PrivateKey::EC_PrivateKey(), EC_PublicKey(), EC_PublicKey(), Botan::GOST_3410_PublicKey::GOST_3410_PublicKey(), Botan::EC_PrivateKey::private_key_bits(), and public_ec_point().
The documentation for this class was generated from the following files:
- src/lib/prov/tpm2/tpm2_ecc/tpm2_ecc.h
- src/lib/prov/tpm2/tpm2_ecc/tpm2_ecc.cpp
Generated by
 1.16.1