#include <tls_session_manager_sqlite.h>
Public Member Functions | |
| virtual std::optional< std::pair< Session, uint16_t > > | choose_from_offered_tickets (const std::vector< PskIdentity > &tickets, std::string_view hash_function, Callbacks &callbacks, const Policy &policy) |
| bool | emits_session_tickets () override |
| virtual std::optional< Session_Handle > | establish (const Session &session, const std::optional< Session_ID > &id=std::nullopt, bool tls12_no_ticket=false) |
| Save a new Session and assign a Session_Handle (TLS Server). | |
| virtual std::vector< Session_with_Handle > | find (const Server_Information &info, Callbacks &callbacks, const Policy &policy) |
Find all sessions that match a given server info. | |
| size_t | remove (const Session_Handle &handle) override |
| size_t | remove_all () override |
| virtual std::optional< Session > | retrieve (const Session_Handle &handle, Callbacks &callbacks, const Policy &policy) |
Retrieves a specific session given a handle. | |
| Session_Manager_SQLite (std::string_view passphrase, const std::shared_ptr< RandomNumberGenerator > &rng, std::string_view db_filename, size_t max_sessions=1000) | |
| void | store (const Session &session, const Session_Handle &handle) override |
| Save a Session under a Session_Handle (TLS Client). | |
Protected Member Functions | |
| virtual bool | database_is_threadsafe () const |
| std::vector< Session_with_Handle > | find_some (const Server_Information &info, size_t max_sessions_hint) override |
| Internal retrieval function to find sessions to resume. | |
| recursive_mutex_type & | mutex () |
| std::optional< Session > | retrieve_one (const Session_Handle &handle) override |
| Internal retrieval function for a single session. | |
Protected Attributes | |
| std::shared_ptr< RandomNumberGenerator > | m_rng |
Detailed Description
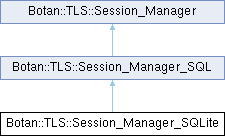
An implementation of Session_Manager that saves values in a SQLite3 database file, with the session data encrypted using a passphrase.
- Warning
- For clients, the hostnames associated with the saved sessions are stored in the database in plaintext. This may be a serious privacy risk in some situations.
Definition at line 27 of file tls_session_manager_sqlite.h.
Constructor & Destructor Documentation
◆ Session_Manager_SQLite()
| Botan::TLS::Session_Manager_SQLite::Session_Manager_SQLite | ( | std::string_view | passphrase, |
| const std::shared_ptr< RandomNumberGenerator > & | rng, | ||
| std::string_view | db_filename, | ||
| size_t | max_sessions = 1000 ) |
- Parameters
-
passphrase used to encrypt the session data Random Number Generators a random number generator db_filename filename of the SQLite database file. The table names tls_sessions and tls_sessions_metadata will be used. A new file is created with the default permissions of the process, so it should be placed in a directory that is not accessible to other users. max_sessions the maximum number of sessions kept in the database; whenever a session is stored, the oldest sessions beyond this limit are permanently deleted. (If zero, don't cap)
Definition at line 14 of file tls_session_manager_sqlite.cpp.
References Botan::TLS::Session_Manager_SQL::Session_Manager_SQL().
Member Function Documentation
◆ choose_from_offered_tickets()
|
virtualinherited |
Lets the server application choose a PSK to use for a new TLS connection. Implementers must make sure that the PSK's associated hash function is equal to the passed hash_function.
RFC 8446 4.2.11 The server MUST ensure that it selects a compatible PSK (if any) and cipher suite.
The default implementation simply tries to retrieve all tickets in the order offered by the peer and picks the first that is found and features a matching hash algorithm.
This method is called only by TLS 1.3 servers. Implementations must only return sessions that were established by a TLS server (via Session_Manager::establish()), as applications may share a single manager between a client and a server role. The TLS server treats a session that was stored by a TLS client as an internal error. The default implementation relies on Session_Manager::retrieve() for this.
- Parameters
-
tickets a list of tickets that were offered by the client hash_function the hash algorithm name we are going to use for the to-be-negotiated connection callbacks callbacks to be used for session policy decisions policy policy to be used for session policy decisions
- Returns
- a std::pair of the Session associated to the chosen PSK and the index of the selected ticket; std::nullopt if no PSK was chosen for usage (will result in a full handshake)
- Note
- if no PSK is chosen, the server will attempt a regular handshake.
Definition at line 252 of file tls_session_manager.cpp.
References retrieve().
Referenced by Botan::TLS::PSK::select_offered_psk(), and store().
◆ database_is_threadsafe()
|
inlineprotectedvirtualinherited |
Decides whether the underlying database is considered threadsafe in the context the Session_Manager is used. If this returns false, accesses to the database are serialized with the base class' recursive mutex.
Definition at line 69 of file tls_session_manager_sql.h.
Referenced by find_some(), retrieve_one(), and store().
◆ emits_session_tickets()
|
inlineoverridevirtualinherited |
Declares whether the given Session_Manager implementation may emit session tickets. Note that this does not mean that the implementation must always emit tickets.
Concrete implementations should declare this, to allow the TLS implementations to act accordingly. E.g. to advertise support for session tickets in their Server Hello.
- Returns
- true if the Session_Manager produces session tickets
Reimplemented from Botan::TLS::Session_Manager.
Definition at line 58 of file tls_session_manager_sql.h.
◆ establish()
|
virtualinherited |
Save a new Session and assign a Session_Handle (TLS Server).
Save a new session on a best effort basis; the manager may not in fact be able to save the session for whatever reason; this is not an error. Callers cannot assume that calling establish() followed immediately by retrieve() or choose_from_offered_tickets() will result in a successful lookup. In case no session was stored, std::nullopt is returned.
This method is only called on TLS servers.
Note that implementations will silently refrain from sending session tickets to the client when this method returns std::nullopt.
- Parameters
-
session to save id to use (instead of an ID chosen by the manager) tls12_no_ticket disable tickets for this establishment (set when TLS 1.2 client does not support them)
- Returns
- a Session_Handle containing either an ID or a ticket if the session was saved, otherwise std::nullopt
Reimplemented in Botan::TLS::Session_Manager_Hybrid, Botan::TLS::Session_Manager_Noop, and Botan::TLS::Session_Manager_Stateless.
Definition at line 48 of file tls_session_manager.cpp.
References BOTAN_ASSERT, BOTAN_UNUSED, m_rng, Botan::TLS::Server, Botan::TLS::Session_Base::side(), and store().
◆ find()
|
virtualinherited |
Find all sessions that match a given server info.
TLS clients use this to obtain session resumption information for a server they are wishing to handshake with. Typically, session info will have been received in prior connections to that same server and stored using Session_Manager::store().
The default implementation will invoke Session_Manager::find_some() and filter the result against a policy. Most notably an expiry check. Expired sessions will be removed via Session_Manager::remove().
Sessions that were established by a TLS server (via Session_Manager::establish()) are never returned, as applications may share a single manager between a client and a server role. Such sessions are not removed; they remain valid for the server role.
The TLS client implementations will query the session manager exactly once per handshake attempt. If no reuse is desired, the session manager may remove the sessions internally when handing them out to the client. The default implementation adheres to Policy::reuse_session_tickets().
For TLS 1.2 the client implementation will attempt a resumption with the first session in the returned list. For TLS 1.3, it will offer all found sessions to the server.
Applications that wish to implement their own Session_Manager may override the default implementation to add further policy checks. Though, typically implementing Session_Manager::find_some() and relying on the default implementation is enough.
- Parameters
-
info the info about the server we want to handshake with callbacks callbacks to be used for session policy decisions policy policy to be used for session policy decisions
- Returns
- a list of usable sessions that might be empty if no such session exists or passed the policy validation
Reimplemented in Botan::TLS::Session_Manager_Hybrid.
Definition at line 207 of file tls_session_manager.cpp.
References BOTAN_ASSERT_NOMSG, Botan::TLS::Policy::maximum_session_tickets_per_client_hello(), mutex(), remove(), and Botan::TLS::Policy::reuse_session_tickets().
Referenced by store().
◆ find_some()
|
overrideprotectedvirtualinherited |
Internal retrieval function to find sessions to resume.
Try to find saved sessions using info about the server we're planning to connect to. It should return a list of sessions in preference order of the session manager.
Applications that wish to implement their own Session_Manager will have to provide an implementation for it.
Note that the TLS client implementations do not perform any checks on the validity of the session for a given info. Particularly, it is the Session_Manager's responsibility to ensure the restrictions posed in RFC 8446 4.6.1 regarding server certificate validity for the given info.
This is called for TLS clients only. Sessions that were established by a TLS server (via Session_Manager::establish()) must not be returned, as applications may share a single manager between a client and a server role. Session_Manager::find() discards them regardless, but they would use up the max_sessions_hint budget.
- Parameters
-
info the information about the server max_sessions_hint a non-binding guideline for an upper bound of sessions to return from this method (will be at least 1 but potentially more)
- Returns
- the found sessions along with their handles (containing either a session ID or a ticket)
Implements Botan::TLS::Session_Manager.
Definition at line 221 of file tls_session_manager_sql.cpp.
References Botan::TLS::Client, database_is_threadsafe(), Botan::TLS::Session::decrypt(), Botan::hex_decode(), Botan::TLS::Server_Information::hostname(), Botan::TLS::Session_Manager::mutex(), and Botan::TLS::Server_Information::port().
◆ mutex()
|
inlineprotectedinherited |
Returns the base class' recursive mutex for reuse in derived classes
Definition at line 292 of file tls_session_manager.h.
Referenced by find(), Botan::TLS::Session_Manager_In_Memory::find_some(), Botan::TLS::Session_Manager_SQL::find_some(), Botan::TLS::Session_Manager_In_Memory::remove(), Botan::TLS::Session_Manager_SQL::remove(), Botan::TLS::Session_Manager_In_Memory::remove_all(), Botan::TLS::Session_Manager_SQL::remove_all(), Botan::TLS::Session_Manager_In_Memory::retrieve_one(), Botan::TLS::Session_Manager_SQL::retrieve_one(), Botan::TLS::Session_Manager_In_Memory::store(), and Botan::TLS::Session_Manager_SQL::store().
◆ remove()
|
overridevirtualinherited |
Remove a specific session from the cache, if it exists. The handle might contain either a session ID or a ticket.
- Parameters
-
handle a Session_Handle of the session to be removed
- Returns
- the number of sessions that were removed
Implements Botan::TLS::Session_Manager.
Definition at line 264 of file tls_session_manager_sql.cpp.
References Botan::hex_encode(), Botan::TLS::Session_Handle::id(), Botan::TLS::Session_Manager::mutex(), and Botan::TLS::Session_Handle::ticket().
Referenced by ~Session_Manager_SQL().
◆ remove_all()
|
overridevirtualinherited |
Remove all sessions from the cache
- Returns
- the number of sessions that were removed
Implements Botan::TLS::Session_Manager.
Definition at line 285 of file tls_session_manager_sql.cpp.
References Botan::TLS::Session_Manager::mutex().
Referenced by ~Session_Manager_SQL().
◆ retrieve()
|
virtualinherited |
Retrieves a specific session given a handle.
This is typically used by TLS servers to obtain resumption information for a previous call to Session_Manager::establish() when a client requested resumption using the handle.
Even if the session is found successfully, it is returned only if it passes policy validations. Most notably an expiry check. If the expiry check fails, the default implementation calls Session_Manager::remove() for the provided handle.
Sessions that were stored by a TLS client (via Session_Manager::store()) are never returned, as applications may share a single manager between a client and a server role. Such sessions are not removed; they remain valid for the client role. Overriding implementations must uphold this; the TLS server treats a client session returned here as an internal error.
Applications that wish to implement their own Session_Manager may override the default implementation to add further policy checks. Though, typically implementing Session_Manager::retrieve_one() and relying on the default implementation is enough.
- Parameters
-
handle the Session_Handle to be retrieved callbacks callbacks to be used for session policy decisions policy policy to be used for session policy decisions
- Returns
- the obtained session or std::nullopt if no session was found or the policy checks failed
Reimplemented in Botan::TLS::Session_Manager_Hybrid.
Definition at line 63 of file tls_session_manager.cpp.
References remove(), retrieve_one(), Botan::TLS::Server, Botan::TLS::Policy::session_ticket_lifetime(), and Botan::TLS::Callbacks::tls_current_timestamp().
Referenced by choose_from_offered_tickets(), and store().
◆ retrieve_one()
|
overrideprotectedvirtualinherited |
Internal retrieval function for a single session.
Try to obtain a Session from a Session_Handle that contains either a session ID or a session ticket. This method should not apply any policy decision (such as ticket expiry) but simply be a storage interface.
Applications that wish to implement their own Session_Manager will have to provide an implementation for it.
This method is called only by servers. Sessions that were stored by a TLS client (via Session_Manager::store()) must not be returned, as applications may share a single manager between a client and a server role. Session_Manager::retrieve() discards them regardless.
- Parameters
-
handle a Session_Handle containing either an ID or a ticket
- Returns
- the obtained session or std::nullopt if none can be obtained
Implements Botan::TLS::Session_Manager.
Definition at line 196 of file tls_session_manager_sql.cpp.
References database_is_threadsafe(), Botan::TLS::Session::decrypt(), Botan::hex_encode(), Botan::TLS::Session_Handle::id(), Botan::TLS::Session_Manager::mutex(), and Botan::TLS::Server.
◆ store()
|
overridevirtualinherited |
Save a Session under a Session_Handle (TLS Client).
Save a session on a best effort basis; the manager may not in fact be able to save the session for whatever reason; this is not an error. Callers cannot assume that calling store() followed immediately by find() will result in a successful lookup.
In contrast to establish(), this stores sessions that were created by the server along with a Session_Handle also coined by the server.
This method is only called on TLS clients.
- Parameters
-
session to save handle a Session_Handle on which this session should by stored
Implements Botan::TLS::Session_Manager.
Definition at line 164 of file tls_session_manager_sql.cpp.
References Botan::TLS::Client, database_is_threadsafe(), Botan::TLS::Session::encrypt(), Botan::hex_encode(), Botan::TLS::Server_Information::hostname(), Botan::TLS::Session_Handle::id(), Botan::TLS::Session_Manager::m_rng, Botan::TLS::Session_Manager::mutex(), Botan::TLS::Server_Information::port(), Botan::TLS::Session_Base::server_info(), Botan::TLS::Session_Base::side(), Botan::TLS::Session_Base::start_time(), and Botan::TLS::Session_Handle::ticket().
Referenced by ~Session_Manager_SQL().
Member Data Documentation
◆ m_rng
|
protectedinherited |
Definition at line 300 of file tls_session_manager.h.
Referenced by establish(), Botan::TLS::Session_Manager_Stateless::establish(), Session_Manager(), Botan::TLS::Session_Manager_In_Memory::store(), and Botan::TLS::Session_Manager_SQL::store().
The documentation for this class was generated from the following files:
- src/lib/tls/sessions_sqlite3/tls_session_manager_sqlite.h
- src/lib/tls/sessions_sqlite3/tls_session_manager_sqlite.cpp
Generated by
 1.16.1