Botan 3.14.1
Crypto and TLS for C&
Botan::Certificate_Store_In_SQL Class Reference

#include <certstor_sql.h>
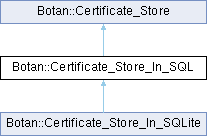
Inheritance diagram for Botan::Certificate_Store_In_SQL:
Botan::Certificate_Store Botan::Certificate_Store_In_SQLite

Public Member Functions

void affirm_cert (const X509_Certificate &cert)
 Reverses the revocation for "cert".
std::vector< X509_DN > all_subjects () const override
bool certificate_known (const X509_Certificate &cert) const
 Certificate_Store_In_SQL (std::shared_ptr< SQL_Database > db, std::string_view passwd, RandomNumberGenerator &rng, std::string_view table_prefix="")
bool contains (const X509_Certificate &cert) const override
std::vector< X509_Certificate > find_all_certs (const X509_DN &subject_dn, const std::vector< uint8_t > &key_id) const override
std::optional< X509_Certificate > find_cert (const X509_DN &subject_dn, const std::vector< uint8_t > &key_id) const override
std::optional< X509_Certificate > find_cert_by_issuer_dn_and_serial_number (const X509_DN &issuer_dn, std::span< const uint8_t > serial_number) const override
std::optional< X509_Certificate > find_cert_by_pubkey_sha1 (const std::vector< uint8_t > &key_hash) const override
std::optional< X509_Certificate > find_cert_by_raw_subject_dn_sha256 (const std::vector< uint8_t > &subject_hash) const override
std::vector< X509_Certificate > find_certs_for_key (const Private_Key &key) const
 Returns all certificates for private key "key".
std::optional< X509_CRL > find_crl_for (const X509_Certificate &issuer) const override
std::shared_ptr< const Private_Key > find_key (const X509_Certificate &cert) const
 Returns the private key for "cert" or an empty shared_ptr if none was found.
std::vector< X509_CRL > generate_crls () const
bool insert_cert (const X509_Certificate &cert)
bool insert_key (const X509_Certificate &cert, const Private_Key &key)
bool remove_cert (const X509_Certificate &cert)
void remove_key (const Private_Key &key)
 Removes "key" from the store.
void revoke_cert (const X509_Certificate &cert, CRL_Code reason)
 Marks "cert" as revoked with no time specified.
void revoke_cert (const X509_Certificate &cert, CRL_Code reason, const X509_Time &time)
 Marks "cert" as revoked starting from "time".

Detailed Description

Certificate and private key store backed by an SQL database.

Definition at line 24 of file certstor_sql.h.

Constructor & Destructor Documentation

◆ Certificate_Store_In_SQL()

Botan::Certificate_Store_In_SQL::Certificate_Store_In_SQL ( std::shared_ptr< SQL_Database > db,
std::string_view passwd,
RandomNumberGenerator & rng,
std::string_view table_prefix = "" )
explicit

Create/open a certificate store.

Parameters
dbunderlying database storage
passwdpassword to encrypt private keys in the database
Random Number Generatorsused for encrypting keys
table_prefixoptional prefix for db table names

Definition at line 23 of file certstor_sql.cpp.

26 :
27 m_rng(rng),
28 m_database(std::move(db)),
29 m_db_cert_table(fmt("{}certificates", table_prefix)),
30 m_db_keys_table(fmt("{}keys", table_prefix)),
31 m_db_crls_table(fmt("{}revoked", table_prefix)),
32 m_password(passwd) {
33 using DB = SQL_Database;
34 const auto blob = DB::Column_Type::Blob;
35 const auto integer = DB::Column_Type::Integer;
36
37 BOTAN_ARG_CHECK(m_database != nullptr, "Database must not be null");
38 BOTAN_ARG_CHECK(m_database->is_valid_table_name(m_db_cert_table), "Invalid table name");
39 BOTAN_ARG_CHECK(m_database->is_valid_table_name(m_db_keys_table), "Invalid table name");
40 BOTAN_ARG_CHECK(m_database->is_valid_table_name(m_db_crls_table), "Invalid table name");
41
42 m_database->create_table(DB::Table_Schema(m_db_cert_table,
43 {
44 DB::Column("fingerprint", blob).primary_key(),
45 DB::Column("subject_dn", blob),
46 DB::Column("key_id", blob),
47 DB::Column("priv_fingerprint", blob),
48 DB::Column("certificate", blob).not_null(),
49 })
50 .if_not_exists());
51
52 m_database->create_table(DB::Table_Schema(m_db_keys_table,
53 {
54 DB::Column("fingerprint", blob).primary_key(),
55 DB::Column("key", blob).not_null(),
56 })
57 .if_not_exists());
58
59 m_database->create_table(DB::Table_Schema(m_db_crls_table,
60 {
61 DB::Column("fingerprint", blob).primary_key(),
62 DB::Column("reason", integer).not_null(),
63 DB::Column("time", integer),
64 })
65 .if_not_exists());
66}
#define BOTAN_ARG_CHECK(expr, msg)
Definition assert.h:33
std::string fmt(std::string_view format, const T &... args)
Definition fmt.h:53

References BOTAN_ARG_CHECK, and Botan::fmt().

Referenced by Botan::Certificate_Store_In_SQLite::Certificate_Store_In_SQLite().

Member Function Documentation

◆ affirm_cert()

void Botan::Certificate_Store_In_SQL::affirm_cert ( const X509_Certificate & cert)

Reverses the revocation for "cert".

Definition at line 296 of file certstor_sql.cpp.

296 {
297 const auto stmt = m_database->new_statement(fmt("DELETE FROM {} WHERE fingerprint = ?1", m_db_crls_table));
298
299 stmt->bind(1, cert.fingerprint("SHA-256"));
300 stmt->spin();
301}

References Botan::X509_Certificate::fingerprint(), and Botan::fmt().

◆ all_subjects()

std::vector< X509_DN > Botan::Certificate_Store_In_SQL::all_subjects ( ) const
overridevirtual

Returns all subject DNs known to the store instance.

Implements Botan::Certificate_Store.

Definition at line 143 of file certstor_sql.cpp.

143 {
144 std::vector<X509_DN> ret;
145 const auto stmt = m_database->select("subject_dn", m_db_cert_table);
146
147 while(stmt->step()) {
148 BER_Decoder dec(stmt->get_blob(0), BER_Decoder::Limits::DER());
149 X509_DN dn;
150
151 dn.decode_from(dec);
152
153 ret.push_back(dn);
154 }
155
156 return ret;
157}
static Limits DER()
Definition ber_dec.h:44

References Botan::X509_DN::decode_from(), and Botan::BER_Decoder::Limits::DER().

◆ certificate_known()

bool Botan::Certificate_Store::certificate_known ( const X509_Certificate & cert) const
inherited

Old version of contains

Definition at line 24 of file certstor.cpp.

24 {
25 return contains(cert);
26}
virtual bool contains(const X509_Certificate &cert) const
Definition certstor.cpp:28

References contains().

Referenced by find_cert_by_issuer_dn_and_serial_number().

◆ contains()

bool Botan::Certificate_Store_In_SQL::contains ( const X509_Certificate & cert) const
overridevirtual
Returns
whether this certificate is contained within the store
Parameters
certcertificate to be searched

Default implementation uses find_all_certs

Reimplemented from Botan::Certificate_Store.

Definition at line 176 of file certstor_sql.cpp.

176 {
177 const auto stmt = m_database->select("1", m_db_cert_table, "fingerprint = ?1");
178 stmt->bind(1, cert.fingerprint("SHA-256"));
179 return stmt->step();
180}

References Botan::X509_Certificate::fingerprint().

◆ find_all_certs()

std::vector< X509_Certificate > Botan::Certificate_Store_In_SQL::find_all_certs ( const X509_DN & subject_dn,
const std::vector< uint8_t > & key_id ) const
overridevirtual

Find all certificates with a given Subject DN. Subject DN and even the key identifier might not be unique.

Implements Botan::Certificate_Store.

Definition at line 92 of file certstor_sql.cpp.

93 {
94 std::vector<X509_Certificate> certs;
95
96 std::shared_ptr<SQL_Database::Statement> stmt;
97
98 const std::vector<uint8_t> dn_encoding = subject_dn.BER_encode();
99
100 if(key_id.empty()) {
101 stmt = m_database->select("certificate", m_db_cert_table, "subject_dn = ?1");
102 stmt->bind(1, dn_encoding);
103 } else {
104 stmt = m_database->select("certificate", m_db_cert_table, "subject_dn = ?1 AND (key_id IS NULL OR key_id = ?2)");
105 stmt->bind(1, dn_encoding);
106 stmt->bind(2, key_id);
107 }
108
109 while(stmt->step()) {
110 certs.push_back(X509_Certificate(stmt->get_blob(0)));
111 }
112
113 return certs;
114}

References Botan::ASN1_Object::BER_encode().

◆ find_cert()

std::optional< X509_Certificate > Botan::Certificate_Store_In_SQL::find_cert ( const X509_DN & subject_dn,
const std::vector< uint8_t > & key_id ) const
overridevirtual

Returns the first certificate with matching subject DN and optional key ID.

Reimplemented from Botan::Certificate_Store.

Definition at line 69 of file certstor_sql.cpp.

70 {
71 std::shared_ptr<SQL_Database::Statement> stmt;
72
73 const std::vector<uint8_t> dn_encoding = subject_dn.BER_encode();
74
75 if(key_id.empty()) {
76 stmt = m_database->select("certificate", m_db_cert_table, "subject_dn = ?1", 1);
77 stmt->bind(1, dn_encoding);
78 } else {
79 stmt =
80 m_database->select("certificate", m_db_cert_table, "subject_dn = ?1 AND (key_id IS NULL OR key_id = ?2)", 1);
81 stmt->bind(1, dn_encoding);
82 stmt->bind(2, key_id);
83 }
84
85 while(stmt->step()) {
86 return X509_Certificate(stmt->get_blob(0));
87 }
88
89 return std::optional<X509_Certificate>();
90}

References Botan::ASN1_Object::BER_encode().

Referenced by remove_cert().

◆ find_cert_by_issuer_dn_and_serial_number()

std::optional< X509_Certificate > Botan::Certificate_Store_In_SQL::find_cert_by_issuer_dn_and_serial_number ( const X509_DN & issuer_dn,
std::span< const uint8_t > serial_number ) const
overridevirtual

Find a certificate by searching for one with a matching issuer DN and serial number. Used for CMS or PKCS#7.

Parameters
issuer_dnthe distinguished name of the issuer
serial_numberthe certificate's serial number
Returns
a matching certificate or nullopt otherwise

TODO(Botan4) change this to use X509_Serial_Number

Implements Botan::Certificate_Store.

Definition at line 126 of file certstor_sql.cpp.

127 {
128 throw Not_Implemented("Certificate_Store_In_SQL::find_cert_by_issuer_dn_and_serial_number");
129}

◆ find_cert_by_pubkey_sha1()

std::optional< X509_Certificate > Botan::Certificate_Store_In_SQL::find_cert_by_pubkey_sha1 ( const std::vector< uint8_t > & key_hash) const
overridevirtual

Find a certificate by searching for one with a matching SHA-1 hash of public key. Used for OCSP.

Parameters
key_hashSHA-1 hash of the subject's public key
Returns
a matching certificate or nullopt otherwise

Implements Botan::Certificate_Store.

Definition at line 116 of file certstor_sql.cpp.

117 {
118 throw Not_Implemented("Certificate_Store_In_SQL::find_cert_by_pubkey_sha1");
119}

◆ find_cert_by_raw_subject_dn_sha256()

std::optional< X509_Certificate > Botan::Certificate_Store_In_SQL::find_cert_by_raw_subject_dn_sha256 ( const std::vector< uint8_t > & subject_hash) const
overridevirtual

Find a certificate by searching for one with a matching SHA-256 hash of raw subject name. Used for OCSP.

Parameters
subject_hashSHA-256 hash of the subject's raw name
Returns
a matching certificate or nullopt otherwise

Implements Botan::Certificate_Store.

Definition at line 121 of file certstor_sql.cpp.

122 {
123 throw Not_Implemented("Certificate_Store_In_SQL::find_cert_by_raw_subject_dn_sha256");
124}

◆ find_certs_for_key()

std::vector< X509_Certificate > Botan::Certificate_Store_In_SQL::find_certs_for_key ( const Private_Key & key) const

Returns all certificates for private key "key".

Definition at line 216 of file certstor_sql.cpp.

216 {
217 const auto fprint = key.fingerprint_private("SHA-256");
218 const auto stmt = m_database->select("certificate", m_db_cert_table, "priv_fingerprint = ?1");
219
220 stmt->bind(1, fprint);
221
222 std::vector<X509_Certificate> certs;
223 while(stmt->step()) {
224 certs.push_back(X509_Certificate(stmt->get_blob(0)));
225 }
226
227 return certs;
228}

References Botan::Private_Key::fingerprint_private().

◆ find_crl_for()

std::optional< X509_CRL > Botan::Certificate_Store_In_SQL::find_crl_for ( const X509_Certificate & issuer) const
overridevirtual

Generates a CRL for all certificates issued by the given issuer.

Reimplemented from Botan::Certificate_Store.

Definition at line 131 of file certstor_sql.cpp.

131 {
132 const auto all_crls = generate_crls();
133
134 for(const auto& crl : all_crls) {
135 if(!crl.get_revoked().empty() && crl.issuer_dn() == subject.issuer_dn()) {
136 return crl;
137 }
138 }
139
140 return std::optional<X509_CRL>();
141}
std::vector< X509_CRL > generate_crls() const
botan_x509_crl_t crl
Definition ffi_tls.h:127

References crl, generate_crls(), and Botan::X509_Certificate::issuer_dn().

◆ find_key()

std::shared_ptr< const Private_Key > Botan::Certificate_Store_In_SQL::find_key ( const X509_Certificate & cert) const

Returns the private key for "cert" or an empty shared_ptr if none was found.

Definition at line 196 of file certstor_sql.cpp.

196 {
197 const auto stmt =
198 m_database->new_statement(fmt("SELECT key FROM {} JOIN {} ON {}.fingerprint = {}.priv_fingerprint "
199 "WHERE {}.fingerprint = ?1",
200 m_db_keys_table,
201 m_db_cert_table,
202 m_db_keys_table,
203 m_db_cert_table,
204 m_db_cert_table));
205 stmt->bind(1, cert.fingerprint("SHA-256"));
206
207 std::shared_ptr<const Private_Key> key;
208 while(stmt->step()) {
209 DataSource_Memory src(stmt->get_blob(0));
210 key = PKCS8::load_key(src, m_password);
211 }
212
213 return key;
214}
std::unique_ptr< Private_Key > load_key(DataSource &source, const std::function< std::string()> &get_pass)
Definition pkcs8.cpp:320

References Botan::X509_Certificate::fingerprint(), Botan::fmt(), and Botan::PKCS8::load_key().

Referenced by insert_key().

◆ generate_crls()

std::vector< X509_CRL > Botan::Certificate_Store_In_SQL::generate_crls ( ) const

Generates Certificate Revocation Lists for all certificates marked as revoked. A CRL is returned for each unique issuer DN.

Definition at line 303 of file certstor_sql.cpp.

303 {
304 const auto stmt =
305 m_database->new_statement(fmt("SELECT certificate,reason,time FROM {} JOIN {} ON {}.fingerprint = "
306 "{}.fingerprint",
307 m_db_crls_table,
308 m_db_cert_table,
309 m_db_cert_table,
310 m_db_crls_table));
311
312 std::map<X509_DN, std::vector<CRL_Entry>> crls;
313 while(stmt->step()) {
314 const auto cert = X509_Certificate(stmt->get_blob(0));
315 const auto code = static_cast<CRL_Code>(stmt->get_size_t(1));
316 const auto ent = CRL_Entry(cert, code);
317
318 const auto i = crls.find(cert.issuer_dn());
319 if(i == crls.end()) {
320 crls.insert(std::make_pair(cert.issuer_dn(), std::vector<CRL_Entry>({ent})));
321 } else {
322 i->second.push_back(ent);
323 }
324 }
325
326 const X509_Time t(std::chrono::system_clock::now());
327
328 std::vector<X509_CRL> ret;
329 ret.reserve(crls.size());
330
331 for(const auto& p : crls) {
332 ret.push_back(X509_CRL(p.first, t, t, p.second));
333 }
334
335 return ret;
336}
ASN1_Time X509_Time
Definition asn1_obj.h:27

References Botan::CRL_Entry, and Botan::fmt().

Referenced by find_crl_for().

◆ insert_cert()

bool Botan::Certificate_Store_In_SQL::insert_cert ( const X509_Certificate & cert)

Inserts "cert" into the store, returns false if the certificate is already known and true if insertion was successful.

Definition at line 159 of file certstor_sql.cpp.

159 {
160 const std::vector<uint8_t> dn_encoding = cert.subject_dn().BER_encode();
161 const std::vector<uint8_t> cert_encoding = cert.BER_encode();
162
163 const auto stmt =
164 m_database->upsert(m_db_cert_table, {"fingerprint", "subject_dn", "key_id", "priv_fingerprint", "certificate"});
165
166 stmt->bind(1, cert.fingerprint("SHA-256"));
167 stmt->bind(2, dn_encoding);
168 stmt->bind(3, cert.subject_key_id());
169 stmt->bind(4, std::vector<uint8_t>());
170 stmt->bind(5, cert_encoding);
171 stmt->spin();
172
173 return true;
174}

References Botan::ASN1_Object::BER_encode(), Botan::X509_Certificate::fingerprint(), Botan::X509_Certificate::subject_dn(), and Botan::X509_Certificate::subject_key_id().

Referenced by insert_key(), revoke_cert(), and revoke_cert().

◆ insert_key()

bool Botan::Certificate_Store_In_SQL::insert_key ( const X509_Certificate & cert,
const Private_Key & key )

Inserts "key" for "cert" into the store, returns false if the key is already known and true if insertion was successful.

Definition at line 230 of file certstor_sql.cpp.

230 {
231 insert_cert(cert);
232
233 if(find_key(cert)) {
234 return false;
235 }
236
237 auto pkcs8 = PKCS8::BER_encode(key, m_rng, m_password);
238 const auto fprint = key.fingerprint_private("SHA-256");
239
240 const auto stmt1 = m_database->upsert(m_db_keys_table, {"fingerprint", "key"});
241
242 stmt1->bind(1, fprint);
243 stmt1->bind(2, pkcs8.data(), pkcs8.size());
244 stmt1->spin();
245
246 const auto stmt2 =
247 m_database->new_statement(fmt("UPDATE {} SET priv_fingerprint = ?1 WHERE fingerprint = ?2", m_db_cert_table));
248
249 stmt2->bind(1, fprint);
250 stmt2->bind(2, cert.fingerprint("SHA-256"));
251 stmt2->spin();
252
253 return true;
254}
bool insert_cert(const X509_Certificate &cert)
std::shared_ptr< const Private_Key > find_key(const X509_Certificate &cert) const
Returns the private key for "cert" or an empty shared_ptr if none was found.
std::vector< uint8_t > BER_encode(const Private_Key &key, RandomNumberGenerator &rng, std::string_view pass, std::chrono::milliseconds msec, std::string_view pbe_algo)
Definition pkcs8.cpp:168

References Botan::PKCS8::BER_encode(), find_key(), Botan::X509_Certificate::fingerprint(), Botan::Private_Key::fingerprint_private(), Botan::fmt(), and insert_cert().

◆ remove_cert()

bool Botan::Certificate_Store_In_SQL::remove_cert ( const X509_Certificate & cert)

Removes "cert" from the store. Returns false if the certificate could not be found and true if removal was successful.

Definition at line 182 of file certstor_sql.cpp.

182 {
183 if(!find_cert(cert.subject_dn(), cert.subject_key_id())) {
184 return false;
185 }
186
187 const auto stmt = m_database->new_statement(fmt("DELETE FROM {} WHERE fingerprint = ?1", m_db_cert_table));
188
189 stmt->bind(1, cert.fingerprint("SHA-256"));
190 stmt->spin();
191
192 return true;
193}
std::optional< X509_Certificate > find_cert(const X509_DN &subject_dn, const std::vector< uint8_t > &key_id) const override

References find_cert(), Botan::X509_Certificate::fingerprint(), Botan::fmt(), Botan::X509_Certificate::subject_dn(), and Botan::X509_Certificate::subject_key_id().

◆ remove_key()

void Botan::Certificate_Store_In_SQL::remove_key ( const Private_Key & key)

Removes "key" from the store.

Definition at line 256 of file certstor_sql.cpp.

256 {
257 const auto fprint = key.fingerprint_private("SHA-256");
258 const auto stmt = m_database->new_statement(fmt("DELETE FROM {} WHERE fingerprint = ?1", m_db_keys_table));
259
260 stmt->bind(1, fprint);
261 stmt->spin();
262}

References Botan::Private_Key::fingerprint_private(), and Botan::fmt().

◆ revoke_cert() [1/2]

void Botan::Certificate_Store_In_SQL::revoke_cert ( const X509_Certificate & cert,
CRL_Code reason )

Marks "cert" as revoked with no time specified.

Definition at line 284 of file certstor_sql.cpp.

284 {
285 insert_cert(cert);
286
287 const auto stmt1 = m_database->upsert(m_db_crls_table, {"fingerprint", "reason", "time"});
288
289 stmt1->bind(1, cert.fingerprint("SHA-256"));
290 stmt1->bind(2, static_cast<uint32_t>(code));
291 stmt1->bind_null(3);
292
293 stmt1->spin();
294}

References Botan::X509_Certificate::fingerprint(), and insert_cert().

◆ revoke_cert() [2/2]

void Botan::Certificate_Store_In_SQL::revoke_cert ( const X509_Certificate & cert,
CRL_Code reason,
const X509_Time & time )

Marks "cert" as revoked starting from "time".

Definition at line 265 of file certstor_sql.cpp.

265 {
266 // TODO(Botan4) require that time be valid
267 insert_cert(cert);
268
269 const auto stmt1 = m_database->upsert(m_db_crls_table, {"fingerprint", "reason", "time"});
270
271 stmt1->bind(1, cert.fingerprint("SHA-256"));
272 stmt1->bind(2, static_cast<uint32_t>(code));
273
274 if(time.time_is_set()) {
275 stmt1->bind(3, time.to_std_timepoint());
276 } else {
277 stmt1->bind_null(3);
278 }
279
280 stmt1->spin();
281}

References Botan::X509_Certificate::fingerprint(), insert_cert(), Botan::ASN1_Time::time_is_set(), and Botan::ASN1_Time::to_std_timepoint().


The documentation for this class was generated from the following files: